Post Syndicated from The Atlantic original https://www.youtube.com/watch?v=mkKa5-KW0f4
Mike Karels has passed away
Post Syndicated from corbet original https://lwn.net/Articles/977070/
We have just received the
sad news that longtime core BSD developer Mike Karels has died; he will
certainly be missed.
Incus 6.2 released
Post Syndicated from corbet original https://lwn.net/Articles/977059/
Version 6.2 of the Incus container-management system is out. “This
” The features include a new incus top
release contains the second wave of changes contributed by students of the
University of Texas at Austin and a few other features and
improvements.
command, a new API for system load information, and more.
Application Security at re:Inforce 2024
Post Syndicated from Daniel Begimher original https://aws.amazon.com/blogs/security/application-security-at-reinforce-2024/
Join us in Philadelphia, Pennsylvania, on June 10–12, 2024, for AWS re:Inforce, a security learning conference where you can enhance your skills and confidence in cloud security, compliance, identity, and privacy. As an attendee, you will have access to hundreds of technical and non-technical sessions, an Expo featuring Amazon Web Services (AWS) experts and AWS Security Competency Partners, and keynote sessions led by industry leaders. AWS re:Inforce offers a comprehensive focus on six key areas, including Application Security.
The Application Security track helps you understand and implement best practices for securing your applications throughout the development lifecycle. This year, we are focusing on several key themes:
- Building a culture of security – Learn how to define and influence organizational behavior to speed up application development, while reducing overall security risk through implementing best practices, training your internal teams, and defining ownership.
- Security of the pipeline – Discover how to embed governance and guardrails to allow developer agility, while maintaining security across your continuous integration and delivery (CI/CD) pipelines.
- Security in the pipeline – Explore tooling and automation to reduce the mean time of security reviews and embed continuous security into each stage of the development pipeline.
- Supply chain security – Gain improved awareness of how risks are introduced by extension, track dependencies, and identify vulnerabilities used in your software.
Additionally, this year the Application Security track will have sessions focused on generative AI (gen AI), covering how to secure gen AI applications and use gen AI for development. Join these sessions to deepen your knowledge and up-level your skills, so that you can build modern applications that are robust, resilient, and secure.
Breakout sessions, chalk talks, lightning talks, and code talks
APS201 | Breakout session | Accelerate securely: The Generative AI Security Scoping Matrix
As generative AI ignites business innovation, cybersecurity teams need to keep up with the accelerating domain. Security leaders are seeking tools and answers to help drive requirements around governance, compliance, legal, privacy, threat mitigations, resiliency, and more. This session introduces you to the Generative AI Security Scoping Matrix, which is designed to provide a common language and thought model for approaching generative AI security. Leave the session with a framework, techniques, and best practices that you can use to support responsible adoption of generative AI solutions designed to help your business move at an ever-increasing pace.
APS301 | Breakout session | Enhance AppSec: Generative AI integration in AWS testing
This session presents an in-depth look at the AWS Security Testing program, emphasizing its scaling efforts to help ensure new products and services meet a high security bar pre-launch. With a focus on integrating generative AI into its testing framework, the program showcases how AWS anticipates and mitigates complex security threats to maintain cloud security. Learn about AWS’s proactive approaches to collaboration across teams and mitigating vulnerabilities, enriched by case studies that highlight the program’s flexibility and dedication to security excellence. Ideal for security experts and cloud architects, this session offers valuable insights into safeguarding cloud computing technologies.
APS302 | Breakout session | Building a secure MLOps pipeline, featuring PathAI
DevOps and MLOps are both software development strategies that focus on collaboration between developers, operations, and data science teams. In this session, learn how to build modern, secure MLOps using AWS services and tools for infrastructure and network isolation, data protection, authentication and authorization, detective controls, and compliance. Discover how AWS customer PathAI, a leading digital pathology and AI company, uses seamless DevOps and MLOps strategies to run their AISight intelligent image management system and embedded AI products to support anatomic pathology labs and bio-pharma partners globally.
APS401 | Breakout session | Keeping your code secure
Join this session to dive deep into how AWS implemented generative AI tooling in our developer workflows. Learn about the AWS approach to creating the underlying code scanning and remediation engines that AWS uses internally. Also, explore how AWS integrated these tools into the services we offer through reactive and proactive security features. Leave this session with a better understanding of how you can use AWS to secure code and how the code offered to you through AWS generative AI services is designed to be secure.
APS402 | Breakout session | Verifying code using automated reasoning
In this session, AWS principal applied scientists discuss how they use automated reasoning to certify bug-free code mathematically and help secure underlying infrastructure. Explore how to use Kani, an AWS created open source engine that analyzes, verifies, and detects errors in safe and unsafe Rust code. Hear how AWS built and implemented Kani internally with examples taken from real-world AWS open source code. Leave this session with the tools you need to get started using this Rust verification engine for your own workloads.
APS232 | Chalk talk | Successful security team patterns
It’s more common to hear what a security team does than to hear how the security team does it, or with whom the security team works rather than how it was designed to work. Organizational design is often demoted to a secondary consideration behind the goals of a security team, despite intentional design generally being what empowers, or hinders, security teams from achieving their goals. Security must work across the organization, not in isolation. This chalk talk focuses on designing effective security teams for organizations moving to the cloud, which necessitates outlining both what the security team works on and how it achieves that work.
APS331 | Chalk talk | Verifiable and auditable security inside the pipeline
In this chalk talk, explore platform engineering best practices at AWS. AWS deploys more than 150 million times per year while maintaining 143 different compliance framework attestations and certifications. Internally, AWS has learned how to make security easier for builder teams. Learn key risks associated with operating pipelines at scale and Amazonian mechanisms to make security controls inside the pipeline verifiable and auditable so that you can shift compliance and auditing left into the pipeline.
APS233 | Chalk talk | Threat modeling your generative AI workload to evaluate security risk
As the capabilities and possibilities of machine learning continue to expand with advances in generative AI, understanding the security risks introduced by these advances is essential for protecting your valuable AWS workloads. This chalk talk guides you through a practical threat modeling approach, empowering you to create a threat model for your own generative AI applications. Gain confidence to build your next generative AI workload securely on AWS with the help of threat modeling and leave with actionable steps you can take to get started.
APS321 | Lightning talk | Using generative AI to create more secure applications
Generative AI revolutionizes application development by enhancing security and efficiency. This lightning talk explores how Amazon Q, your generative AI assistant, empowers you to build, troubleshoot, and transform applications securely. Discover how its capabilities streamline the process, allowing you to focus on innovation while ensuring robust security measures. Unlock the power of generative AI for helping build secure, cutting-edge applications.
APS341 | Code talk | Shifting left, securing right: Container supply chain security
Supply chain security for containers helps ensure you can detect software security risks in third-party packages and remediate them during the container image build process. This prevents container images with vulnerabilities from being pushed to your container registry and causing potential harm to your production systems. In this code talk, learn how you can apply a shift-left approach to container image security testing in your deployment pipelines.
Hands-on sessions
APS373 | Workshop | Build a more secure generative AI chatbot with security guardrails
Generative AI is an emerging technology that is disrupting multiple industries. An early generative AI use case is interactive chat in customer service applications. As users interact with generative AI chatbots, there are security risks, such as prompt injection and jailbreaking resulting from specially crafted inputs sent to large language models. In this workshop, learn how to build an AI chatbot using Amazon Bedrock and protect it using Guardrails for Amazon Bedrock. You must bring your laptop to participate.
APS351 | Builders’ session | Implement controls for the OWASP Top 10 for LLM applications
In this builders’ session, learn how to implement security controls that address the OWASP Top 10 for LLM applications on AWS. Experts guide you through the use of AWS security tooling to provide practical insights and solutions to mitigate the most critical security risks outlined by OWASP. Discover technical options and choices you can make in cloud infrastructure and large-scale enterprise environments augmented by AWS generative AI technology. You must bring your laptop to participate.
APS271 | Workshop | Threat modeling for builders
In this workshop, learn threat modeling core concepts and how to apply them through a series of group exercises. Key topics include threat modeling personas, key phases, data flow diagrams, STRIDE, and risk response strategies as well as the introduction of a “threat grammar rule” with an associated tool. In exercises, identify threats and mitigations through the lens of each threat modeling persona. Assemble in groups and walk through a case study, with AWS threat modeling experts on hand to guide you and provide feedback. You must bring your laptop to participate.
APS371 | Workshop | Integrating open source security tools with AWS code services
AWS, open source, and partner tooling work together to accelerate your software development lifecycle. In this workshop, learn how to use the Automated Security Helper (ASH), an open source application security tool, to quickly integrate various security testing tools into your software build and deployment flows. AWS experts guide you through the process of security testing locally on your machines and within the AWS CodeCommit, AWS CodeBuild, and AWS CodePipeline services. In addition, discover how to identify potential security issues in your applications through static analysis, software composition analysis, and infrastructure-as-code testing. You must bring your laptop to participate.
This blog post highlighted some of the unique sessions in the Application Security track at the upcoming re:Inforce 2024 conference in Philadelphia. If these sessions pique your interest, register for re:Inforce 2024 to attend them, along with the numerous other Application Security sessions offered at the conference. For a comprehensive overview of sessions across all tracks, explore the AWS re:Inforce catalog preview.
If you have feedback about this post, submit comments in the Comments section below. If you have questions about this post, contact AWS Support.
New site feature: comment subthread hiding
Post Syndicated from corbet original https://lwn.net/Articles/977033/
In the recent discussion on commenting at
LWN, several readers asked for the ability to hide subthreads of a long
comment stream. That feature has just been added; it is also integrated
with the three comment-display modes and with comment filtering, removing
the need for JavaScript for filtering. Hiding is not persistent; no extra
data is stored at either end.
Give it a try; if you have comments on the new mechanism, this is the place
to put them.
Do I Need a Continuous Backup Solution?
Post Syndicated from Stephanie Doyle original https://backblaze.com/blog/do-i-need-a-continuous-backup-solution/
Most IT administrators and businesses know that you need to employ a 3-2-1 backup solution to meet minimum backup durability requirements, though many folks are of the opinion that that methodology is just table stakes these days. Once you get into the variety of ways you can ensure reliable, robust backups, you learn about strategies like 3-2-1-1-0, bare metal recovery, cyber resilience, and more.
Which method your business ultimately ascribes to depends on your risk tolerance—but no business wants to experience the costs associated with extended downtime. In a world where the threat of ransomware is not an “if”, but a “when,” and disaster recovery is front-of-mind for businesses of all sizes, getting granular with your backup and recovery options is key. That brings us to today’s topic: continuous backup solutions, aka continuous data protection (CDP).
What Is Continuous Data Protection (CDP)?
A continuous data protection solution is an automated data backup method that keeps track of changes to your files and backs them up constantly. This is different from traditional backups that copy your data at set intervals. While you can set the interval that you’d want to have your data backup (e.g., daily, weekly, monthly), you’d still be relying on a systemic approach, and would have data loss exposure correlating to the duration you set. What if you had a day of particularly high volume of new data? What if you’re dealing with sensitive customer information that your business needs to show an accurate audit trail for?
Quick Refresher: The 3-2-1 Backup Strategy
The 3-2-1 backup solution calls for three copies of your data, to be stored on two different media types, with one copy off-site (and preferably geographically separate from your primary data storage region).
Continuous backup solutions work by tracking every change to your data in real time, then they asynchronously create a second copy of those changes. Compare this with traditional backups, where data is written to a destination, then a copy (often, a snapshot) of the data is made to be distributed to other backup locations. With a continuous backup solution, you can reduce your recovery point objection (RPO)—that is, the point in time from which you can recover your data—to near zero. And, because your continuous backups typically have to be stored in more accessible storage tiers, you can reduce your recovery time object (RTO) as well.
Here are some of the key qualities of a continuous backup solution:
- Automatic backups. With continuous backup, you don’t need to remember to manually back up your data. The system continuously monitors your files for changes and backs them up automatically.
- Real-time or frequent backups. Continuous backup solutions can back up your data in real-time, or at least very frequently. This means you’ll always have a very recent copy of your data available in case of data loss.
- Restore to any point in time. Because continuous backups keep track of all the changes made to your files, you can restore your data to any point in time, not just the last time a full backup was run.
Benefits of Continuous Backup Solutions
There are several advantages to using a continuous backup solution:
- Reduced risk of data loss. You’re less likely to lose data due to hardware failure, software corruption, ransomware attacks, or accidental deletion.
- Faster recovery times. If you do lose data, you can restore it from a recent backup much faster than you could with a traditional backup system, especially those that rely on hardware (air gaps) or cold storage for archival storage.
- Improved business continuity. Continuous backup can help businesses keep running smoothly even if they experience a data loss event.
- User-friendly for diverse levels of tech proficiency. Within a business, there are always going to be folks who are more or less proficient with technology. When you have an automatic backup utility that runs in the background—particularly one with advanced central administrative controls like Backblaze Business Backup with Enterprise Control—you aren’t relying on employees’ tech proficiency (or memory) to create backups.
Continuous Backup vs. Near Continuous Backup Solutions
True CDP solutions run at the level where you’re writing changes to your file—according to the patent, at the basic input/output system (BIOS) of the computer such that normal operations are unaffected. In a practical sense, that means you’re nearly always using virtual machines.
There are several near-continuous backup solutions, however, that back up in intervals of one hour or less and leverage a high-availability system. For transparency’s sake, it’s worth noting that Backblaze Computer Backup is a near continuous backup using native code over Java to reduce impact on your computer’s operations—see our documentation for more.
Downsides of Continuous Backup Solutions
There are some challenges to consider when implementing a continuous backup solution:
- Cost: Continuous backup solutions can be more expensive than traditional backup solutions. As time has gone on, there are more solutions available—which has led to more competitive pricing—but it is still a factor to consider.
- Storage requirements: Continuous backup can generate a lot of data. If you’re provisioning storage yourself, you’ll need to make sure you have enough to accommodate the backups. If you’re considering using a cloud backup utility, make sure you look into unlimited backups. Many common backup utilities create pricing tiers that take into account the volume of data a user generates and stores.
- System resources and compatibility: Solutions can use up system resources, which could slow down your computer or server. For example, many utilities use Java instead of native code, which can noticeably slow down your devices.
What’s the Diff: Continuous Backup vs. Synced Cloud Drive
Because a continuous backup solution updates backups in near real-time, it can be confused with cloud sync services. You may have heard us say it before—sync is not backup. The main difference between a continuous backup service and a synced cloud drive boils down to their purpose:
Continuous Backup Service: This prioritizes data protection and recovery. It constantly monitors your files for changes and backs them up frequently, often in real-time. You can restore your data to any specific point in time, making it ideal for disaster recovery or retrieving accidentally deleted files.
Synced Cloud Drive: This focuses on accessibility and collaboration. It keeps a mirrored copy of your designated folders across multiple devices. Any edits you make on one device are reflected in the cloud storage and on all other connected devices. This is great for working on the same files from different locations and keeping everyone, well, in sync.
While some cloud drives have introduced a backup or version history function, they are often limited in scope and subject to the shared responsibility model. Both undermine a true backup strategy, especially if your business has cyber insurance or compliance standards to meet.
Here’s a table summarizing the key differences:
| Feature | Continuous Backup Service | Synced Cloud Drive |
|---|---|---|
| Main Purpose | Data protection and recovery | Accessibility and collaboration |
| Backup Frequency | Continuous or very frequent | User-defined, automatic at intervals, often limited |
| Version Control | Supports restoring to any point in time | May or may not have version history |
| Focus | Protecting against data loss | Sharing and working on files across devices |
| Ideal Use Case | Disaster recovery; accidental deletion recovery; ransomware protection | Remote work; team collaboration |
In short:
- Use a continuous backup service if you’re worried about losing important data due to hardware failure, software corruption, or accidental deletion.
- Use a synced cloud drive if you want to access and edit your files from anywhere and keep them updated across all your devices.
Some services might offer both features, but it’s important to understand which functionality takes priority. And, if in doubt—use both.
Conclusion
Backups continue to be one of the cornerstones of any business’ ransomware protection strategy. As you’re considering what kind of backup you need, consider how much your business needs a granular, point-in-time recovery option to maintain business continuity. As always, you should balance functionality with costs, and the needs of your particular business. But, given the relative affordability of backup tools—and the amount they can save you in the event of a data disaster—solutions like continuous backup are worth considering for businesses of all sizes.
The post Do I Need a Continuous Backup Solution? appeared first on Backblaze Blog | Cloud Storage & Cloud Backup
[$] Handling the NFS change attribute
Post Syndicated from jake original https://lwn.net/Articles/975863/
The saga of the i_version field for inodes, which tracks the
occurrence of changes
to the data or metadata of a file, continued in a discussion at the 2024 Linux Storage,
Filesystem, Memory Management, and BPF Summit. In a session led by
Jeff Layton, who has been doing a lot the work on changing the semantics and functioning of
i_version over the years, he updated attendees on the status of the effort since a session at last year’s summit. His summary
was that things are
“pretty much where we started last year”, but the discussion this time
pointed to some possible ways forward.
Top 5 new improvements in Home Assistant 2024.6
Post Syndicated from BeardedTinker original https://www.youtube.com/watch?v=slHgiE5iguI
[$] An instruction-level BPF memory model
Post Syndicated from daroc original https://lwn.net/Articles/976071/
There are few topics as arcane as memory models, so it was a pleasant surprise
when the double-length session on the BPF memory model at the
Linux Storage,
Filesystem, Memory Management, and BPF Summit turned out to be
understandable. Paul McKenney led the session, although he was clear that the
work he was presenting was also due to Puranjay Mohan, who unfortunately could
not attend the summit.
BPF does not actually have a formalized memory model yet;
instead it has relied on a history of talks like this one and a general informal understanding.
Unfortunately, ignoring memory models does not make them go away, and this has
already caused at least one BPF-related bug on weakly-ordered architectures.
Figuring out what a formal memory model for BPF should define was the focus of
McKenney’s talk.
Security updates for Tuesday
Post Syndicated from corbet original https://lwn.net/Articles/976977/
Security updates have been issued by Mageia (chromium-browser-stable, git, libreoffice, microcode, python-requests, webkit2, and wireshark), Oracle (container-tools:ol8, glibc, go-toolset:ol8, idm:DL1 and idm:client, less, python39:3.9 and python39-devel:3.9, ruby:3.0, and virt:ol and virt-devel:rhel), Red Hat (nodejs, nodejs:18, python-idna, and ruby:3.1), and SUSE (389-ds, ffmpeg, ffmpeg-4, gnutls, gstreamer-plugins-base, libhtp, mariadb104, poppler, python-python-jose, squid, and unbound).
The Dreaded Network Pivot: An Attack Intelligence Story
Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/06/04/the-dreaded-network-pivot-an-attack-intelligence-story/
Rapid7 recently released our 2024 Attack Intelligence Report, a 14-month deep dive into the vulnerability and attacker landscape. The spiritual successor to our annual Vulnerability Intelligence Report, the AIR includes data from the Rapid7 research team combined with our detection and response and threat intelligence teams. It is designed to provide the clearest view yet into what security professionals face day to day.
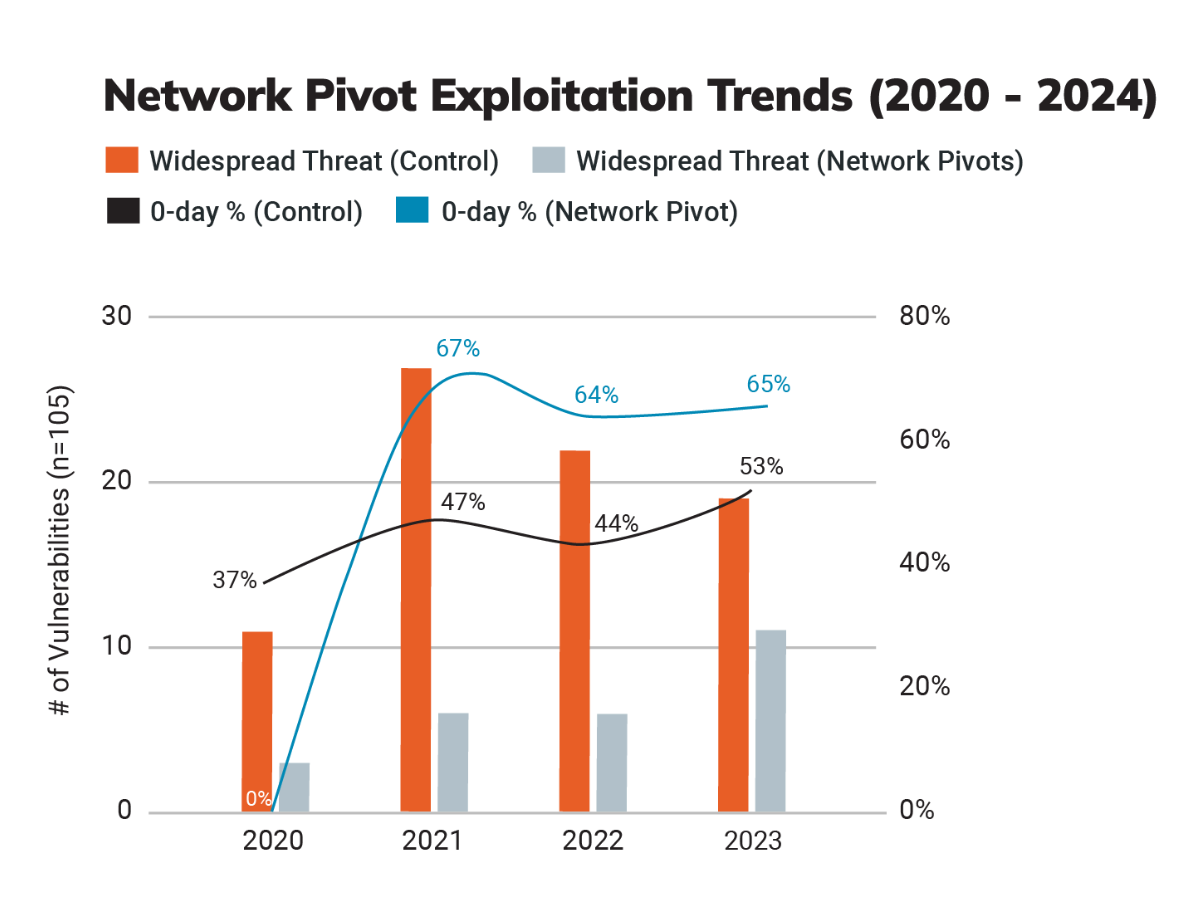
In this blog, we would like to focus on one area of research the AIR highlights: network edge technologies. In 2023 (and early 2024) Rapid7 found some startling information about the vulnerability of these critical devices. Essentially, of the mass compromise events we studied, exploitation of network edge tech increased significantly over the 14 months the report covers — something we will cover in detail shortly.
But first, some background. Way back in 2020, Rapid7 created a new attacker utility category for vulnerabilities that functioned as network pivots. These are vulnerabilities that give external attackers internal network access. Think VPNs, firewalls, security gateways, etc. They serve an important function in any network but visibility into these devices can be challenging, making them prime targets for attackers.
In 2023 we saw a surge in attacks on these network appliances. Mass compromise events stemming from exploitation of network edge tech nearly doubled over the period studied — with 36% of all widely exploited vulnerabilities occurring within network perimeter technology. Looking back over the previous reports, we determined some 60% of all of the vulnerabilities Rapid7 analyzed in network edge devices over a three year period were exploited as zero-days, a disproportionate number when looking at the entirety of the vulnerabilities studied.
Over the four years Rapid7 has been categorizing this type of vulnerability, network edge devices have comprised 24% of exploited vulnerabilities and a quarter of all widespread threats.
State-sponsored groups and ransomware groups like Cl0p, Inc, Bl00dy, Akira, Play, LockBit, and more went after network edge tech in 2023. Network edge devices are essential for modern network operations, but they also represent a major weak spot in cybersecurity defenses — one that these organized groups took advantage of in 2023.
There are a number of reasons for this. It can be difficult to detect intrusions on these types of devices as the capabilities for logging and threat detection vary depending on the specific devices used. Some do not log key events, they use a variety of firmware and (often proprietary) operating systems, and in some cases the firmware itself may be encrypted or obfuscated. This makes monitoring and detecting intrusions troublesome across different devices and developing a strategy for the entire spectrum of devices complex.
For more information about network edge technology vulnerabilities, as well as the latest data on ransomware, attacker utilities, widespread threats, file transfer vulns, and more, download the 2024 Attack Intelligence Report.
THG Podcast: The "Proto" Mafia
Post Syndicated from The History Guy: History Deserves to Be Remembered original https://www.youtube.com/watch?v=BJ_uy_joKHI
Breaking a Password Manager
Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2024/06/breaking-a-password-manager.html
Interesting story of breaking the security of the RoboForm password manager in order to recover a cryptocurrency wallet password.
Grand and Bruno spent months reverse engineering the version of the RoboForm program that they thought Michael had used in 2013 and found that the pseudo-random number generator used to generate passwords in that version—and subsequent versions until 2015—did indeed have a significant flaw that made the random number generator not so random. The RoboForm program unwisely tied the random passwords it generated to the date and time on the user’s computer—it determined the computer’s date and time, and then generated passwords that were predictable. If you knew the date and time and other parameters, you could compute any password that would have been generated on a certain date and time in the past.
If Michael knew the day or general time frame in 2013 when he generated it, as well as the parameters he used to generate the password (for example, the number of characters in the password, including lower- and upper-case letters, figures, and special characters), this would narrow the possible password guesses to a manageable number. Then they could hijack the RoboForm function responsible for checking the date and time on a computer and get it to travel back in time, believing the current date was a day in the 2013 time frame when Michael generated his password. RoboForm would then spit out the same passwords it generated on the days in 2013.
Протестите не смущават Пеевски
Post Syndicated from Bozho original https://blog.bozho.net/blog/4324
На 14-ти юни 2013 г. на площада бяхме хиляди. И в следващите месец и половина също. И искахме оставката на правителството на Орешарски, защото беше недопустимо Пеевски да му дърпа конците. После дойде август и хората оредяхме. После заваляха есенни дъждове и зимни снегове и протестът стана бутиков.
За тези месеци бяхме наречени пренебрежително „умнокрасиви“, „платени протестиращи“, „соросоиди“, „организирани от кръга Капитал и олигарсите“, че „искаме да върнем Борисов на власт“. Телевизиите, вестниците, част от онлайн медиите успешно притъпиха ефекта от протеста.
И Орешарски не падна. Кри се, мънка по интервюта, но остана. Остана, докато ДПС не прецениха, че е време да разтурят седянката. Според слуховете, Пеевски и Борисов „са се разбрали“ още в първите седмици на протеста и само за изчакали евроизборите 2014 г., за да имат повод. А електоралните щети отнесе БСП, които искаха на всяка цена да са срещу ГЕРБ и Пеевски им изглеждаше единственият аритметично възможен вариант.
И аз романтизирам 2013 г. и тя безспорно беше позитивна за гражданското общество, което се намери на площада и там се създадоха много контакти и приятелства, които и до днес са важни за средата. Аз бях на площада и през лятото, и с чадър през есента, и с ръкавици през зимата. Но протестът не свали правителството на Пеевски.
Протестът 2020 г. не свали Борисов. Бързо бяха вкарани същите пропагандни техники, бързо протестиращите бяха разделени „ама вие що под юмрука на Радев“, „защо протестирате в деня, в който влизаме в чакалнята на еврозоната“. Борисов извади димката с новата Конституция. Беше август, протестите пак оредяха, дойде есента и си зачакахме изборите. Да, тогава Борисов загуби много периферия и ГЕРБ се сви. После се сви още. Безспорно Росенец и последващите протести бяха нужни, важни и затвърдиха заявката на 2013 г, че има граници, които не бива да се преминават.
Но Борисов не падна. Защото си имаше покдрепа в парламента, патриотите отдавна бяха изсмукани електорално и нямаха стимул да ходят на избори, а Пеевски си управляваше.
Ако след тези избори ГЕРБ и ДПС (с някоя малка патеричка, като ИТН, които вече дадоха такава заявка) направят правителство, ще има протести при първия голяма скандал, който ще сътворят (а той ще е на първата седмица). Само че протестът няма да ги свали. Протестиращите пак ще бъдем „платени“, „кръга капитал“, ще „обслужваме олигарсите, дето искат да няма съдебна система“ и т.н. И това ще се лее от телевизора от сутрин до вечер, докато анализатори цъкат с език и развиват теории за политическата стабилност.
За да не се разочароваме, че протестът пак не е успял, можем да гласуваме в неделя. Това е единственият начин да не излезе математиката. Предния път ИТН също бяха готови, по-предния път Стефан Янев беше готов. Но все стигаха докъм 115-116 гласа.
Знам, че сега няколко човека бързо ще напишат коментари „Ама то и вие управлявахте с Пеевски“. Такива обвинения, между другото, чувахме от опозицията в парламента през ден. Нещо, което само понякога влиза в стенограмите, са подвикванията от залата. Но на тези обвинения от ДПС имаше подвиквания „аа, ние само за Конституцията“. И това беше именно така. Затова след като мина Конституцията и ДПС не си видя гарантираните постове в съдебната власт, които винаги преди това е имало, започнаха атаките.
Признавам, че нуждата да променим Конституцията, за да отнемем част от властта на Пеевски, беше използвана добре от него публично, за да може сега да има хора, които едновременно не го понасят и му вярват за „скутовете и турските кафета“. За да може да чуваме „изпрахте Пеевски“, при положение, че не вярвам да има и един човек , който 2023 г. да не е хареавал Пеевски, а 2024 г. вече да му е фен, ‘щото е „изпран“.
Те играят добре тактически. Там ни бият. Ние гледаме да свършим работата, за която сме пратени, и понякога сме незащитени от такива атаки. И когато оставихме властта, защото ни се отказаха следващите реформи, позволихме тяхната версия (за „постовете“) да бъде прокарана успешно в обществото и да замени реалната причина да отидем на избори.
Именно защото са добри тактически играчи, те вече са подготвили антипротестната тактика. И ако чакаме да излезем на площада след 9-ти юни, вече ще е късно.
Материалът Протестите не смущават Пеевски е публикуван за пръв път на БЛОГодаря.
Intel Xeon 6 6700E Sierra Forest Shatters Xeon Expectations
Post Syndicated from Patrick Kennedy original https://www.servethehome.com/intel-xeon-6-6700e-sierra-forest-shatters-xeon-expectations/
The Intel Xeon 6 “Sierra Forest” is here shattering expectations on what it means to be a Xeon with 144 cores and very low power consumption
The post Intel Xeon 6 6700E Sierra Forest Shatters Xeon Expectations appeared first on ServeTheHome.
Intel Gaudi 2 8x OAM UBB $65K Gaudi 3 $125K and Includes Networking
Post Syndicated from Cliff Robinson original https://www.servethehome.com/intel-gaudi-2-8x-oam-ubb-65k-gaudi-3-125k-and-includes-networking/
Intel has hard list prices for its 8x OAM UBB assemblies at $65K for Gaudi 2 and $125K for Gaudi 3, and that includes networking
The post Intel Gaudi 2 8x OAM UBB $65K Gaudi 3 $125K and Includes Networking appeared first on ServeTheHome.
Comic for 2024.06.04 – Baby Shoes
Post Syndicated from Explosm.net original https://explosm.net/comics/baby-shoes-5
New Cyanide and Happiness Comic
Tree-huggers
Post Syndicated from Oglaf! -- Comics. Often dirty. original https://www.oglaf.com/treehuggers/


Comic for 2024.06.03 – A Tiny Mermaid
Post Syndicated from Explosm.net original https://explosm.net/comics/a-tiny-mermaid
New Cyanide and Happiness Comic
LyX 2.4.0 Released
Post Syndicated from jzb original https://lwn.net/Articles/976826/
Version 2.4.0 of the LyX
document processor has been released. LyX is a “What You See Is What You
Mean” (WYSIWYM) application that offers GUI editing of LaTeX
documents with import and export to PDF, HTML, OpenDocument, Word, and
other formats. LyX 2.4.0 is the first major release in six years, and
brings support for EPUB, DocBook 5, improved
table styles, and now uses Unicode (utf8) as its default encoding. See
the full list of new
features on the LyX wiki, and release
notes for information on known issues and caveats for those
upgrading from earlier versions of LyX.