Зеленият ринг в София vs. „ма туй си е мое бе“

Post Syndicated from Боян Юруков original https://yurukov.net/blog/2026/zelen-ring-sech/

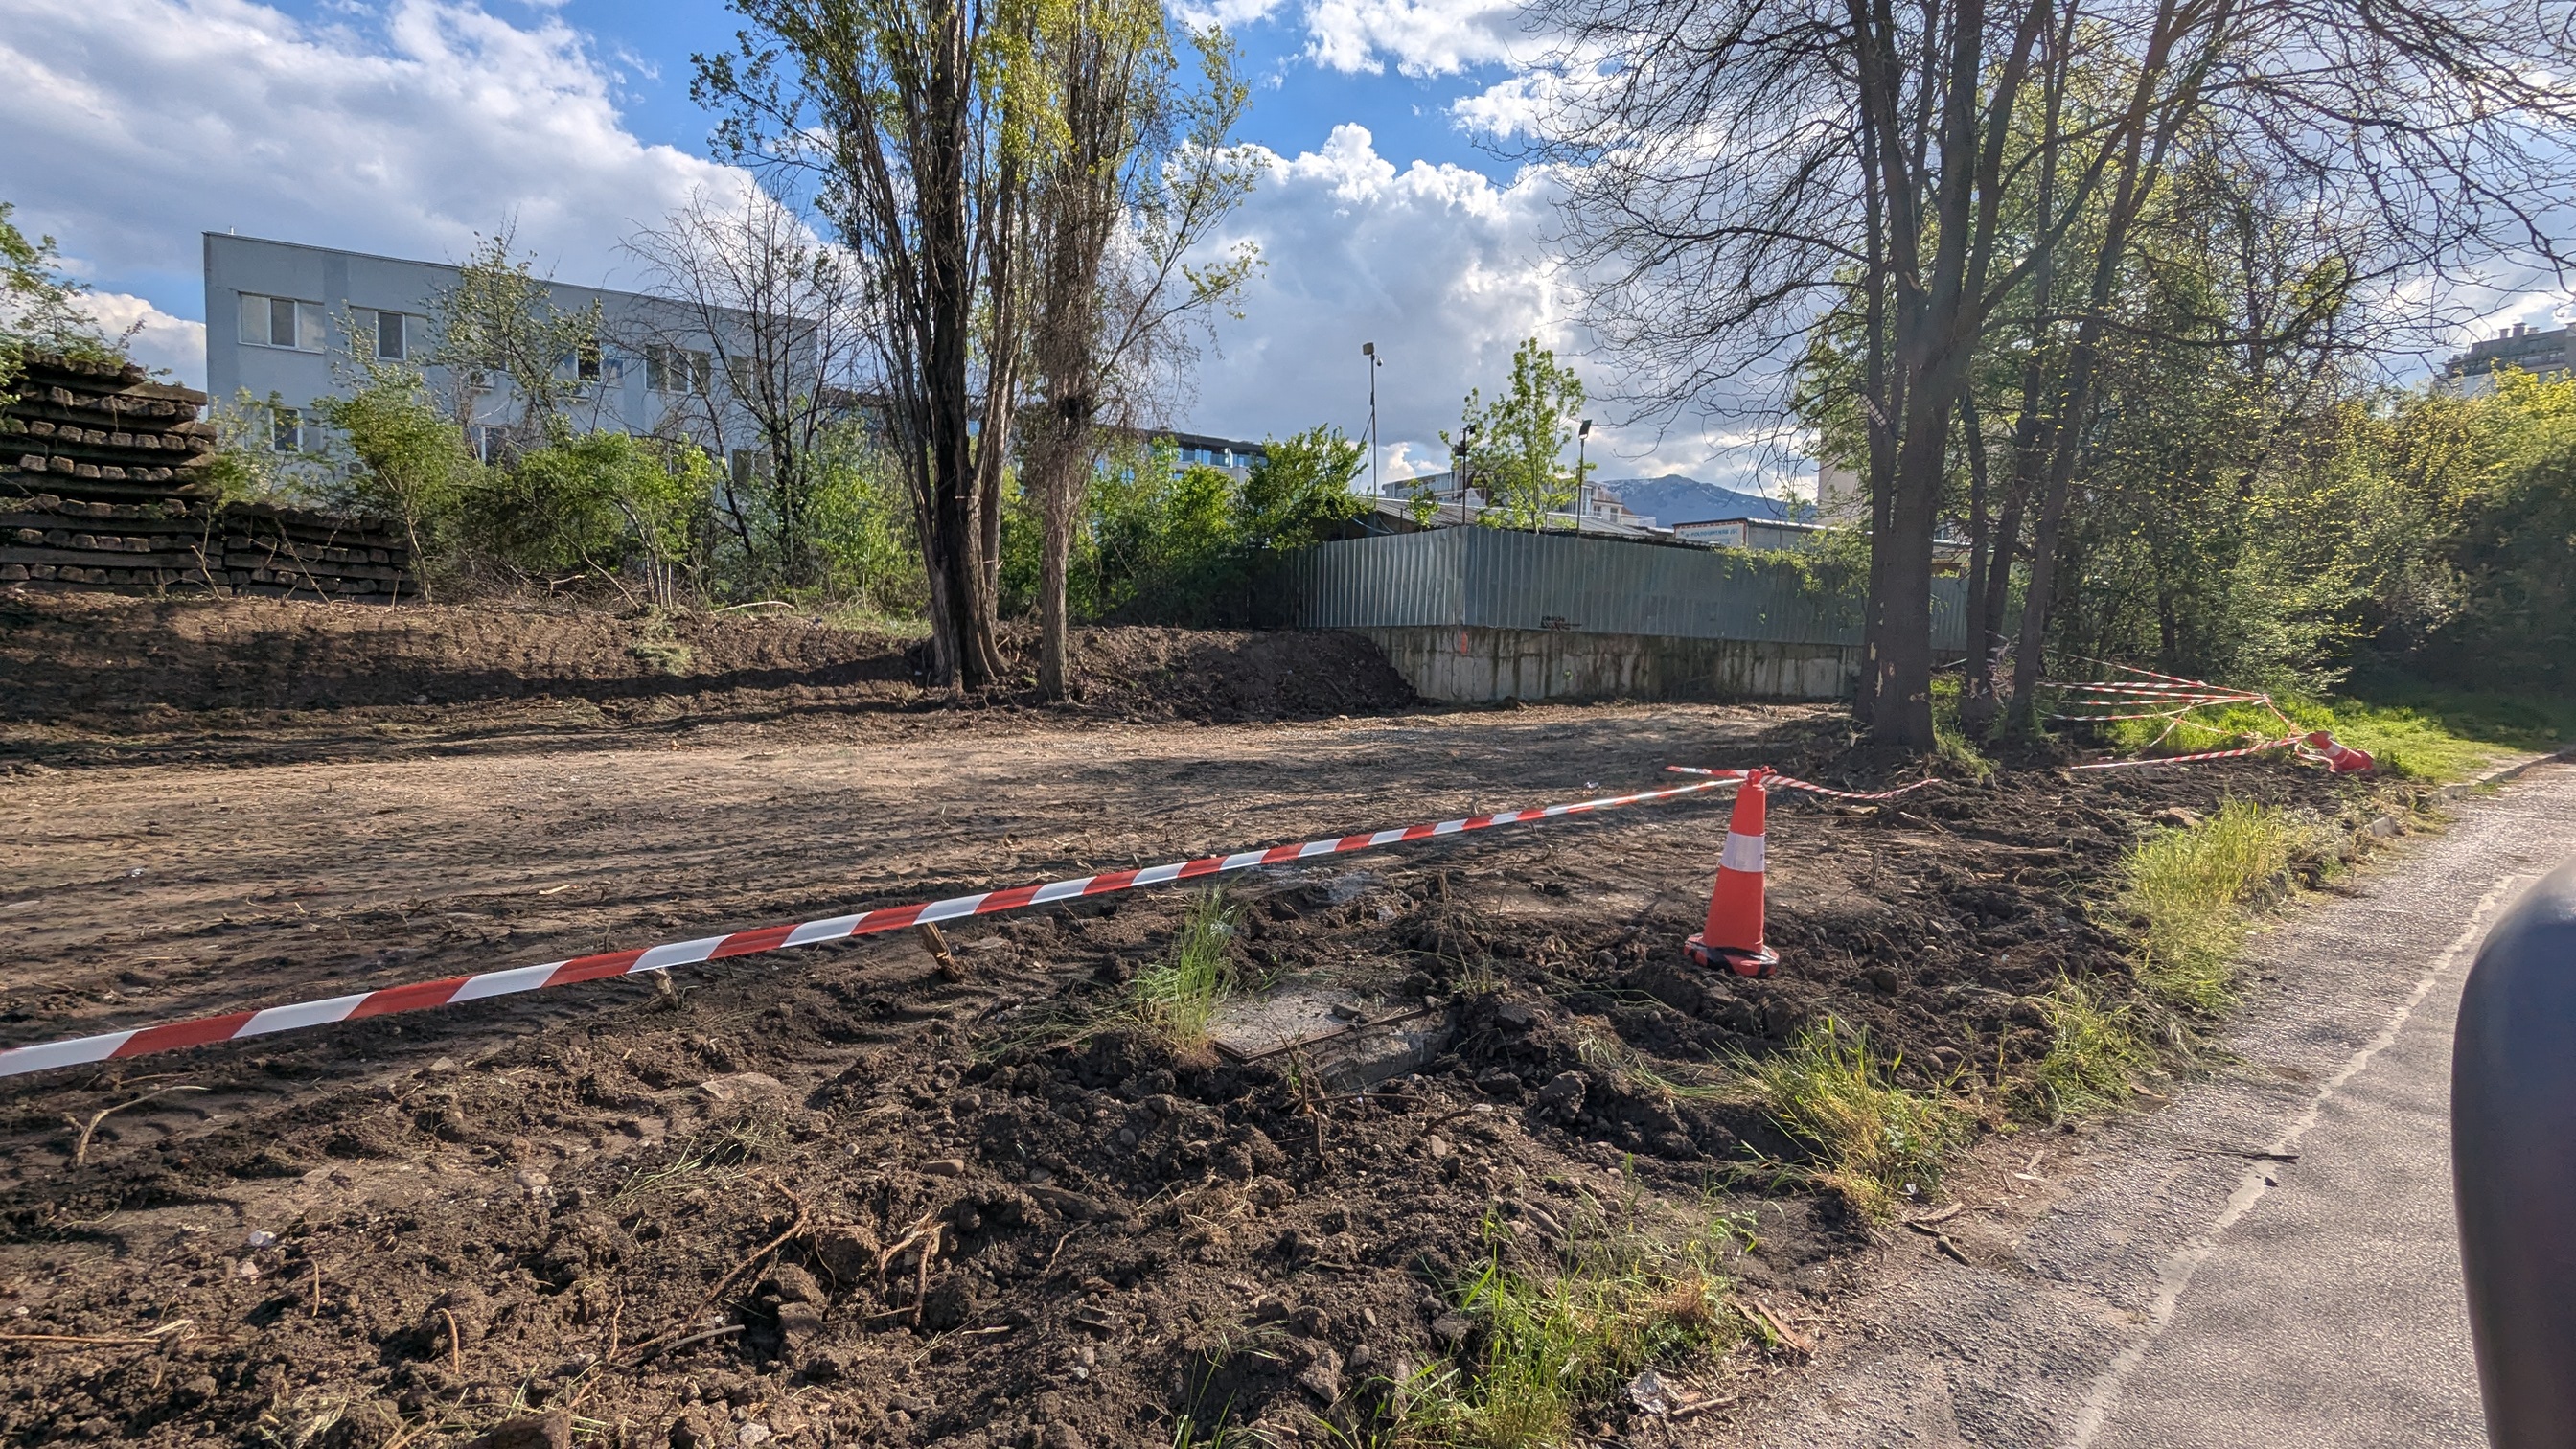
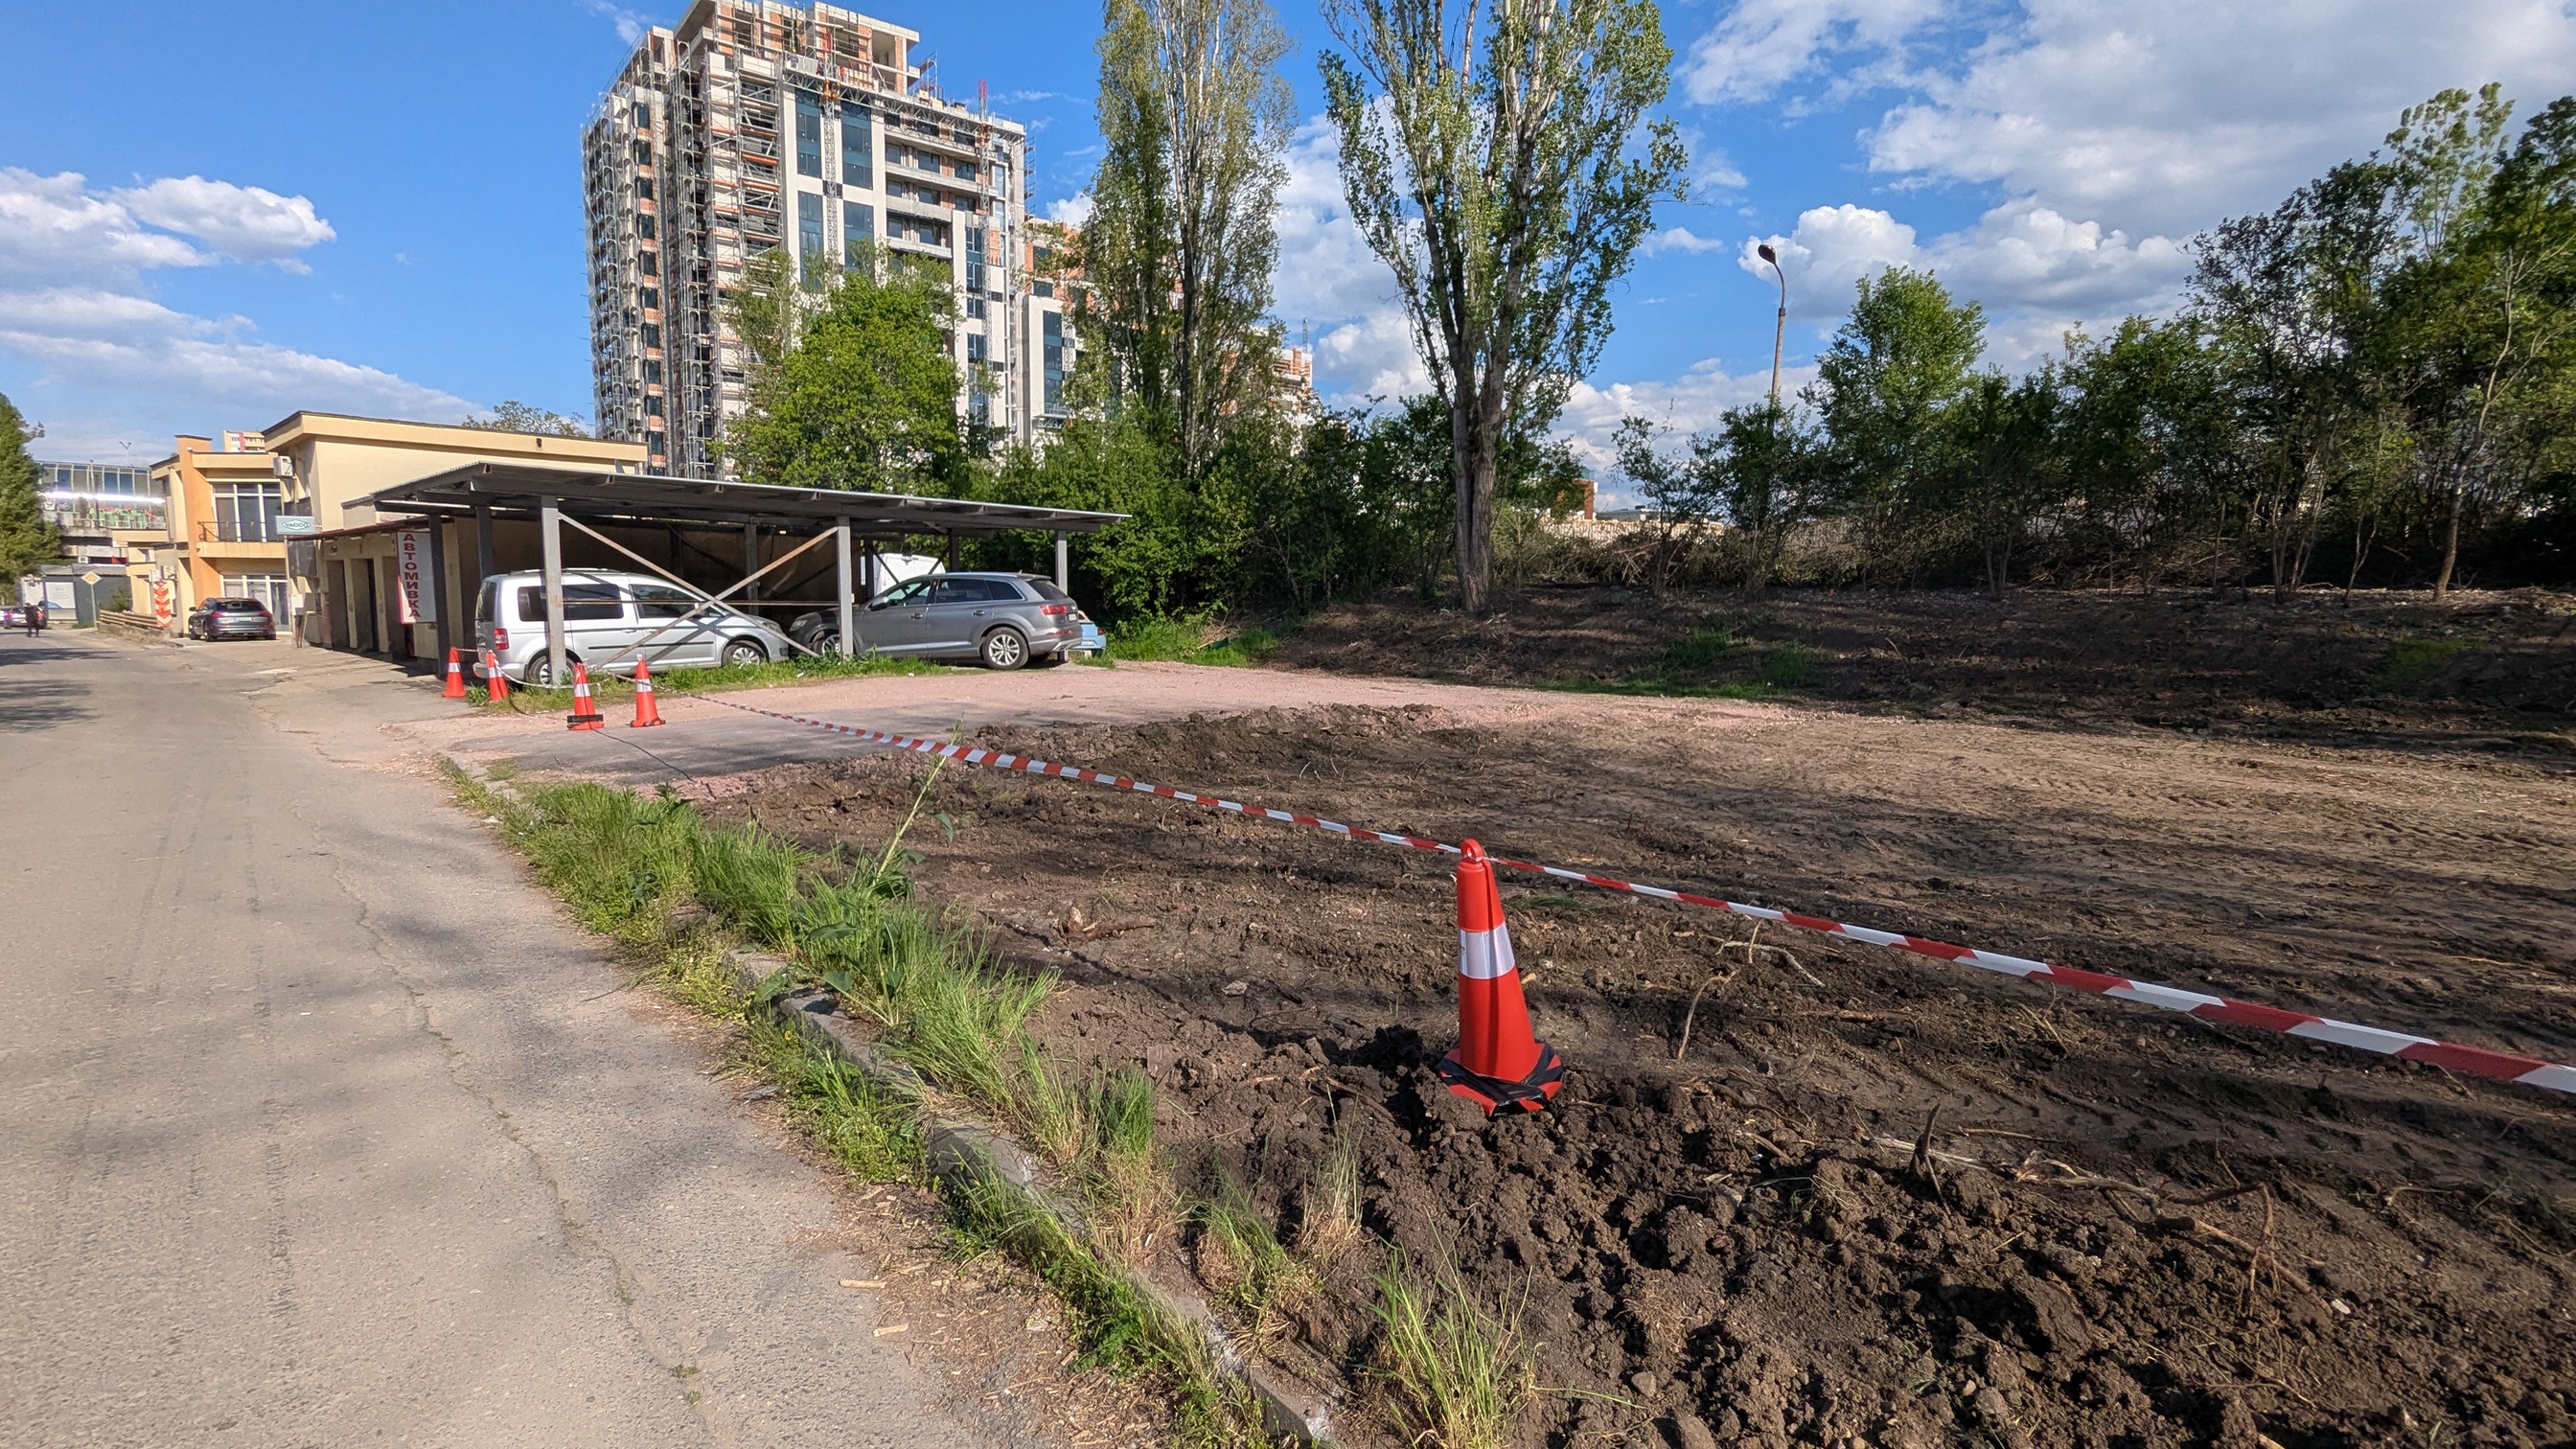
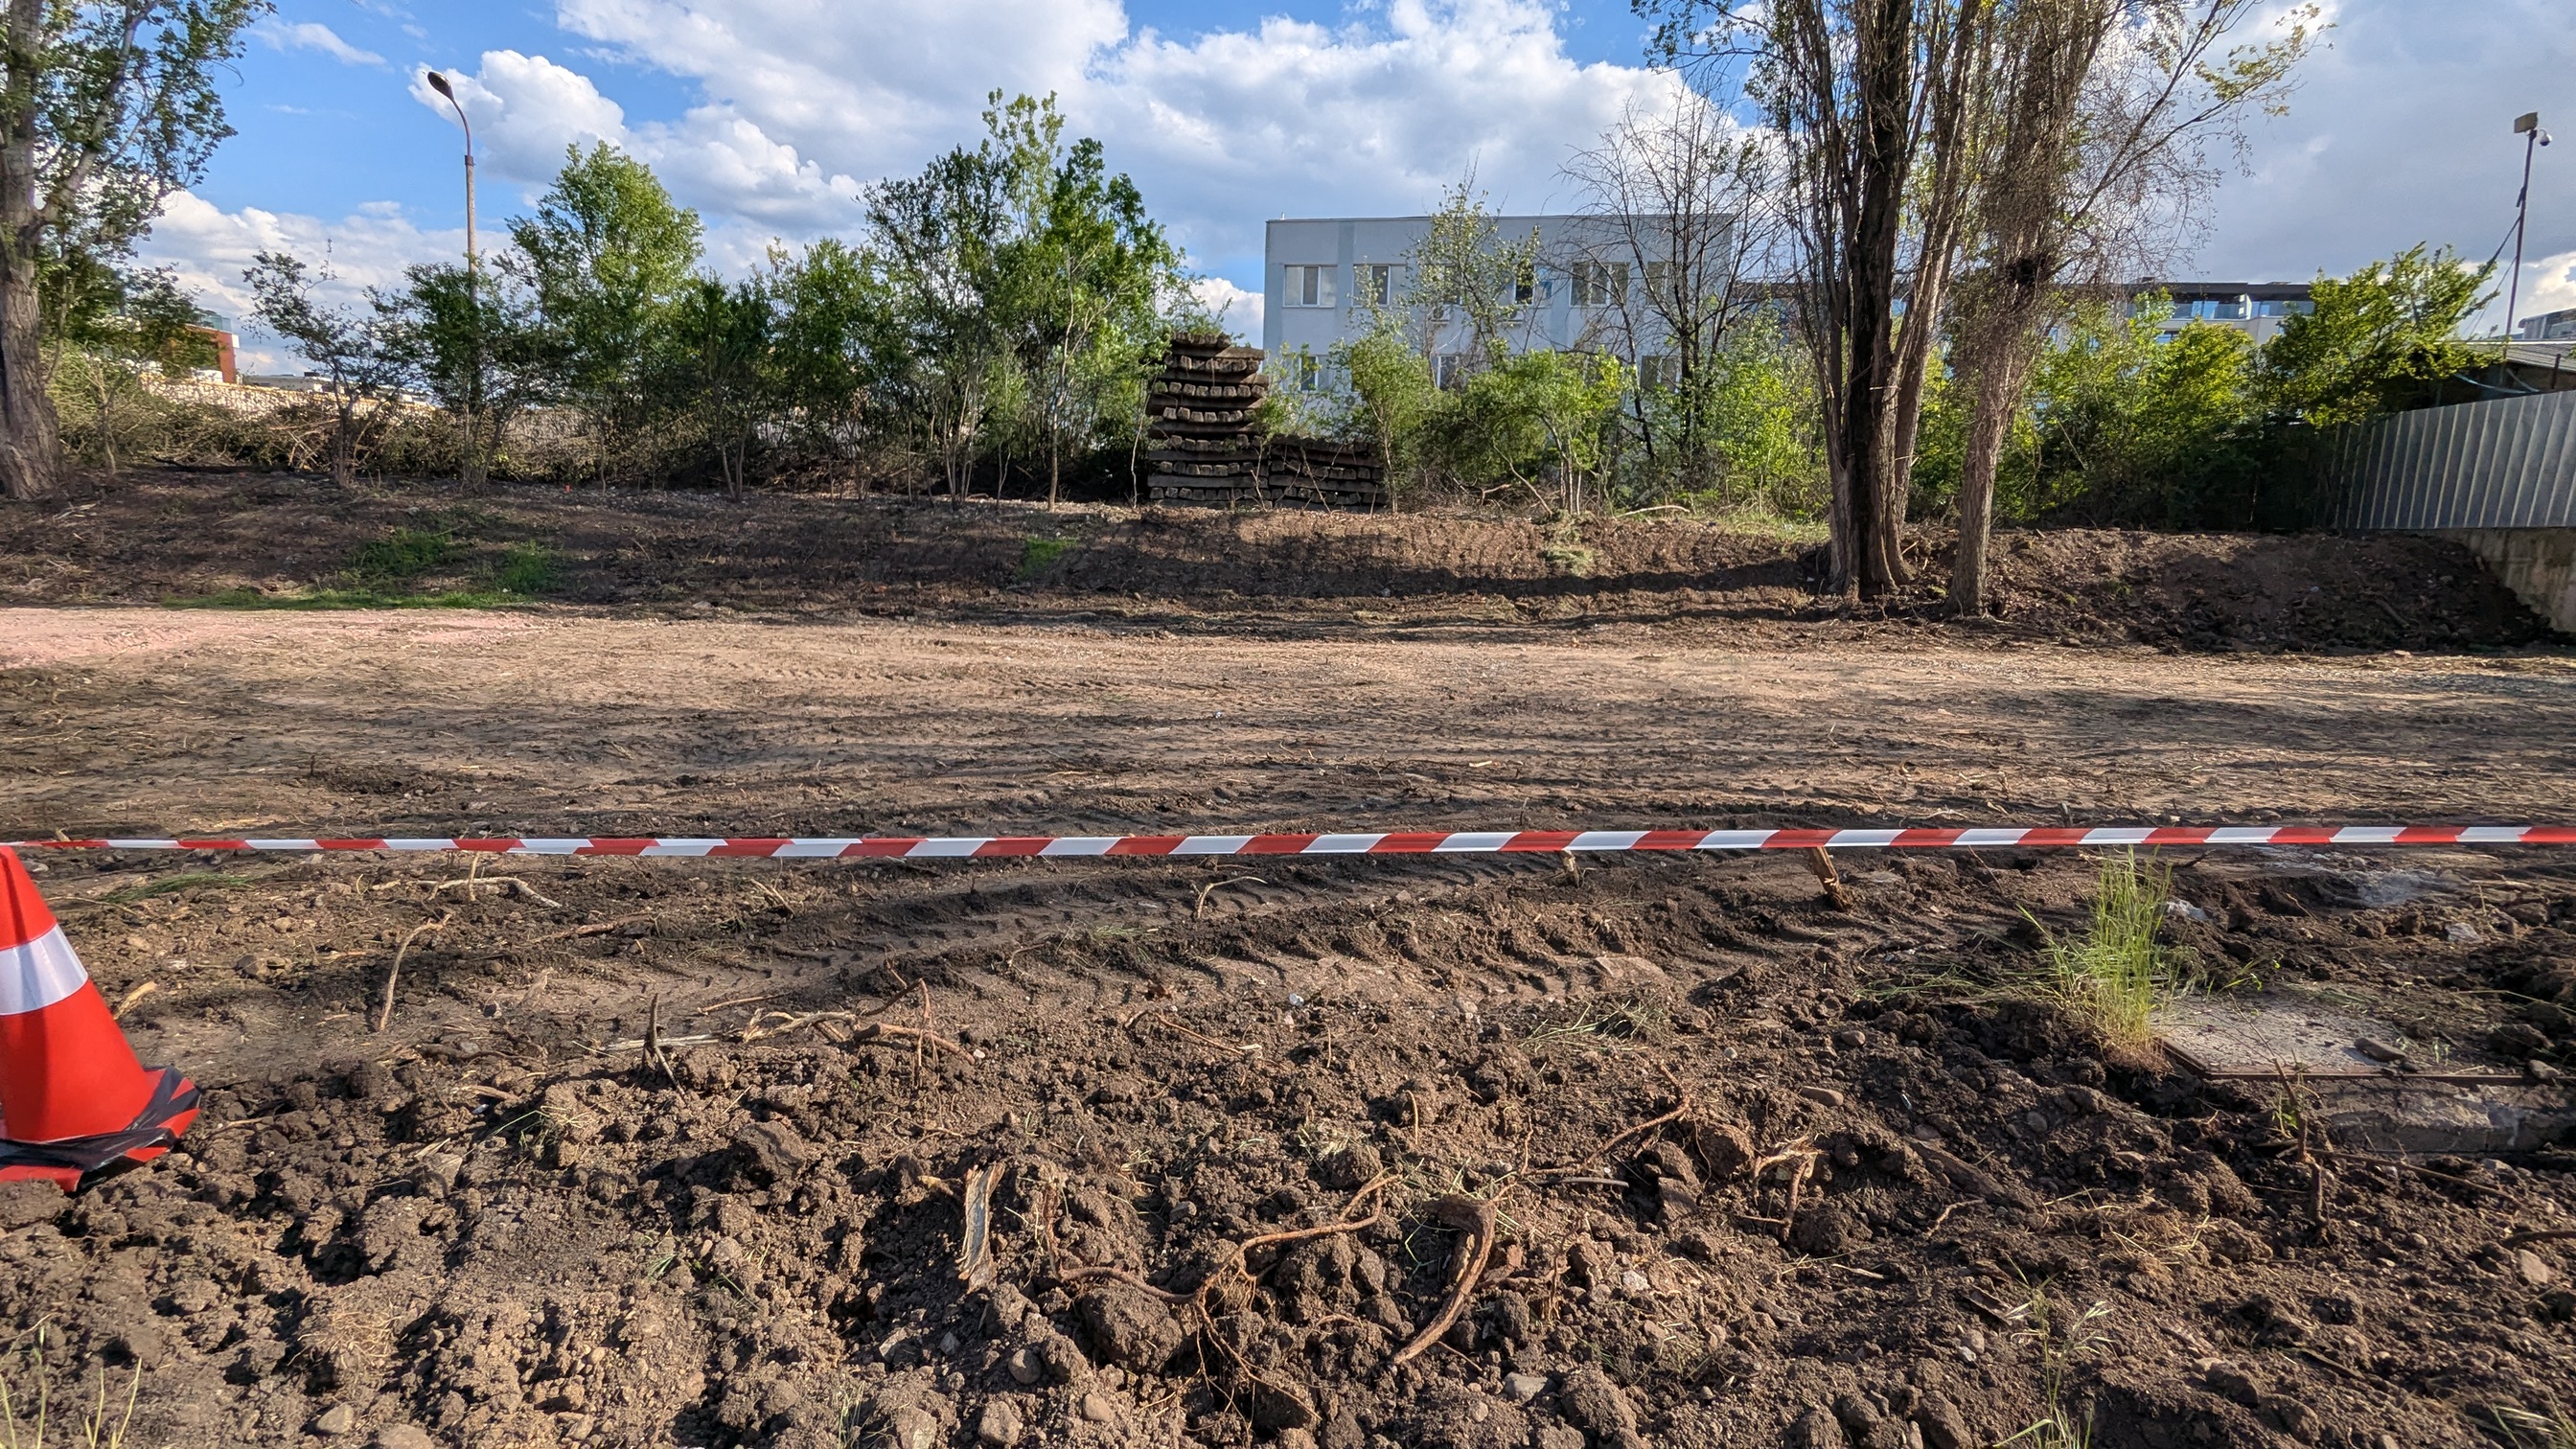
Днес имах интересна среща и разговор. На път да взема щерката от градина забелязах, че една от автомивките наместила се покрай заветния бъдещ Зелен ринг в частта на район Изгрев е изсекла между 15 и 30 дървета и е изчистила терен от 2 декара държавна земя. Всъщност 500 кв. м. от тях са били заравнени и се използват в последните 7 години като паркинг, но там поне не е имало дървета.

Спрях се да снимам, при което двама мъже ме заградиха. Единият се представи като собственик (което не мога да потвърдя) и ми поиска лична карта, защото съм снимал частен имот. Казах му, че няма такова право и снимам, за да подам сигнал за незаконна сеч на дървета и разчистване на държавна земя. Тогава стана още по-нападателен и настоя, че е частен имота и може да прави каквото си иска. След малко разправии смени версията, че всъщност било на държавна фирма, но имал разрешение и кой па съм бил аз и прочие.

По стечение на обстоятелствата знам наизуст парцелите и границите им в района, та още там видях три проблема с твърденията му.

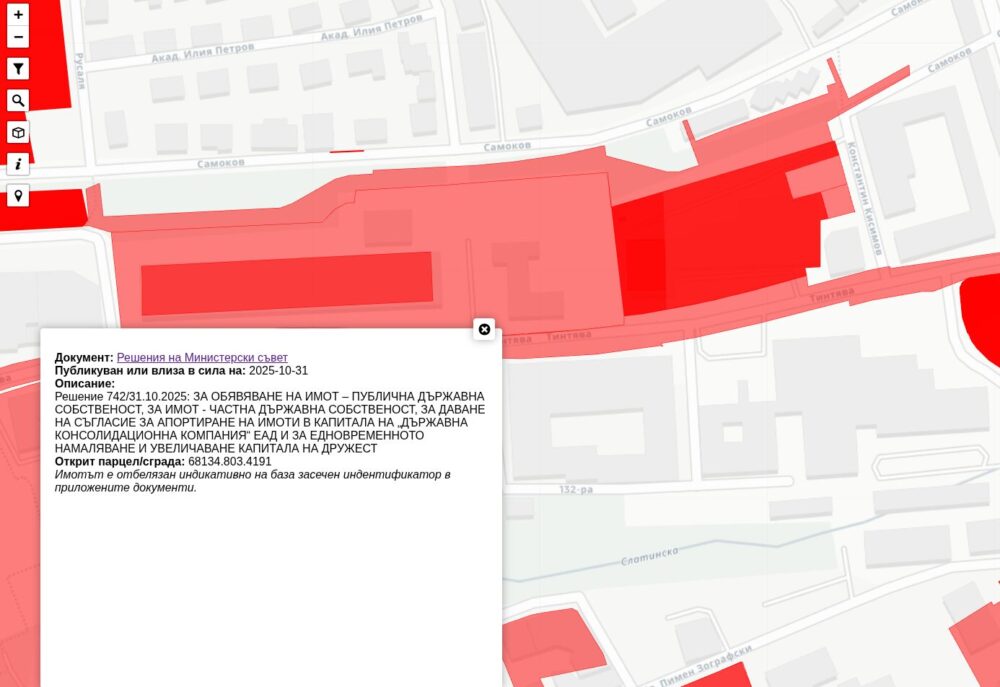
Първо, това, което виждате на снимките са три имота. Сградите са плътно бетонирали парцел, който незнайно как е станал частен преди 2000 г. и още по-малко ясно е дали са законни въобще. Има апокрифно разрешение за строеж на кафене и автосервиз, но на пръв поглед се вижда, че доста са надстроявали. Имотът, за който вероятно единия заградил ме говореше, е 68134.803.4182. Той е част от Железопътна инфраструктура и през ноември 2025-та е имало търг за наем. Не е обявено кой го е спечелил, но предполагаме, че за тях си е направен търга и те са си го спечелили. Интересното тук е, че точно този търг не е обявен на специалната страница на АППК за разлика от търговете на всички останали държавни дружества, както и други на това предприятие.

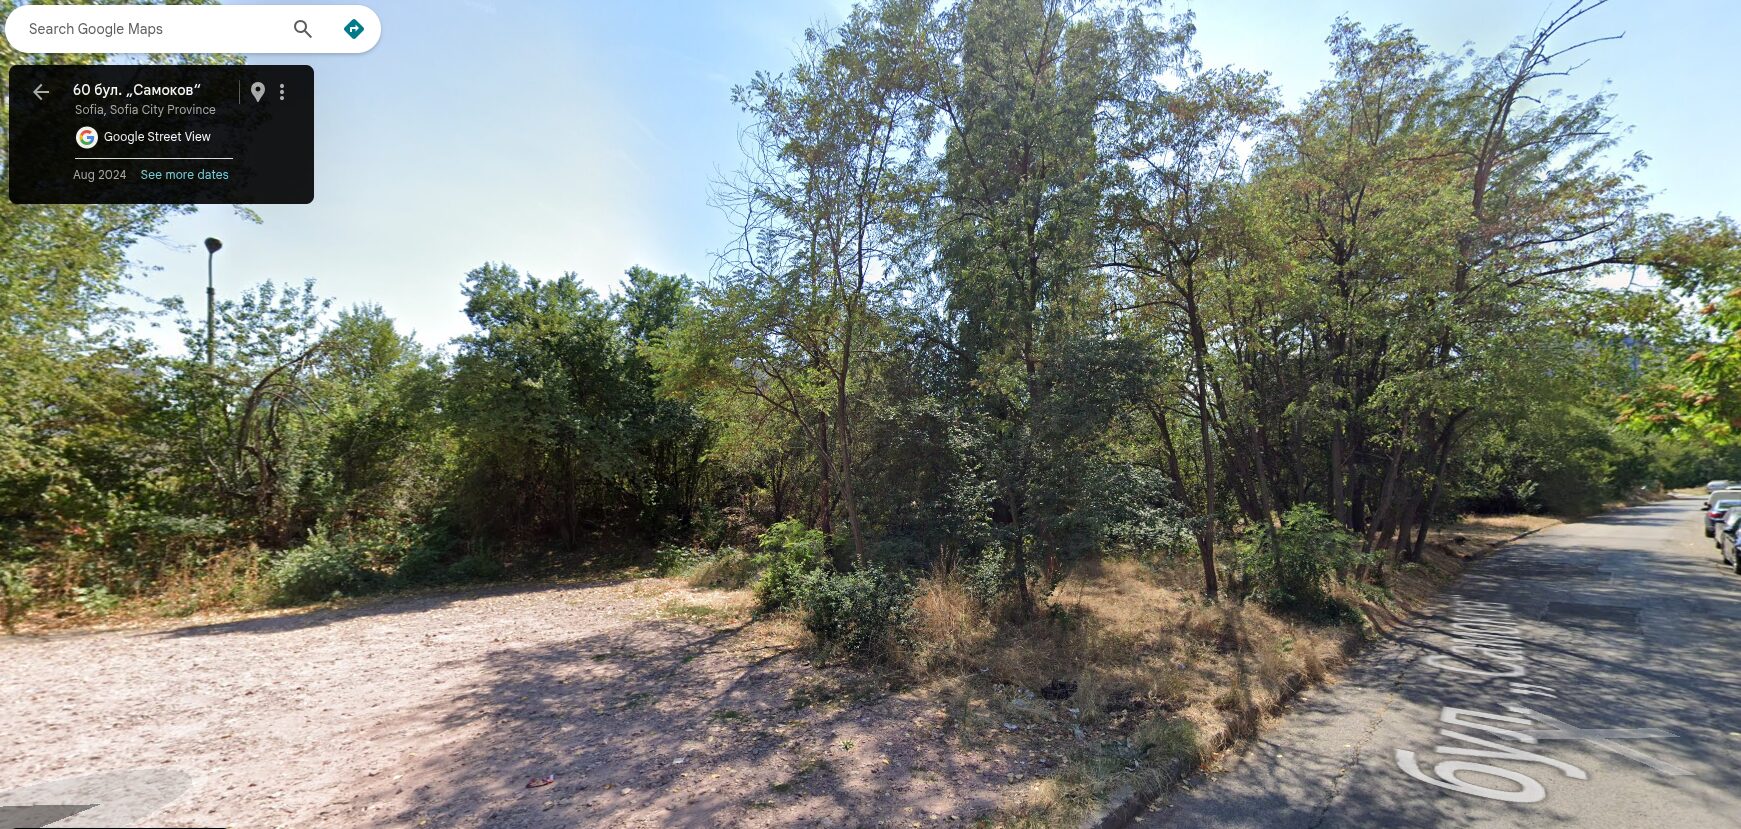
  • Снимка на мястото от края на 2024-та

Тук обаче въпросът е, че този наем не им дава право да изсичат дърветата, нито договорът за наем е основание да им се дава такова право. За целта независимо от собствеността на имота трябва да искат разрешение от район Изгрев, които са наясно с това. По наредба тези заповеди се издават при строго определени хипотези, следва да са публични също както протоколите от общинския служител присъстващ на сечта. Такива не са публикувани и приемайки за чиста монета демонстрираната загриженост на районния кмет за зелените площи, приемаме, че разрешение за сеч нямат.

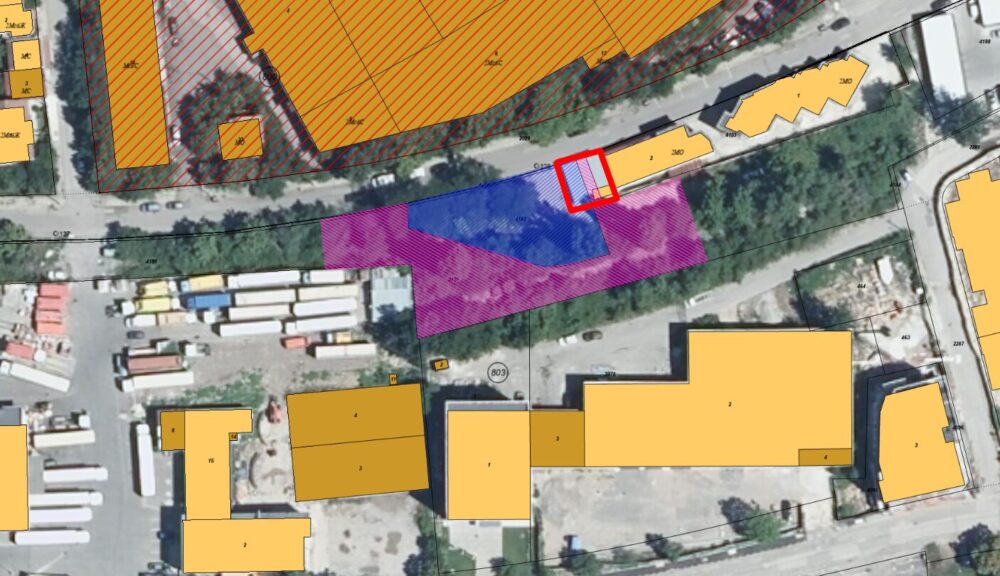
Вторият проблем е, че както се вижда на последната снимка, те са разчистили не само парцел 4182, но и 1.4 декара от 68134.803.4191. Вижда се с просто око дигата и бетонната стена. Този имот не влиза в хипотетичния договор за наем, а е основна част от Зеления ринг. За него със сигурност районният кмет Георгиев не следва да е подписал заповед за сеч предвид, че се похвали с това, че областния управител задейства прехвърлянето на въпросния парцел и други след решение на Министерски съвет и дълги усилия от неправителствени организации и Столична община да се случи това.

Третият проблем е, че от поне 15 години навесът, където се извършва основната дейност на автомивката не е законен, тъй като според кадастъра и ортофотозаснемането само малка част е в частния имот, а другите две части са в имота предполагаемо даден под наем, а имотът с решение за прехвърляне на общината минава точно между въпросните два парцела. Та, ако следваме стриктно закона, навесът следва да се събори и пространството с широчина от 2.5 да се освободи.

В синьо е имотът с предполагаем наем. В лилаво е какво допълнително са изсекли. В червено е незаконния навес.

Бързах за детската градина и не ми се обясняваше всичко това. С поведението им и клишираните въпроси „ти па от къде знаеш, че е незаконно“ не видях и причина да се обяснявам. В крайна сметка ми освободиха пътя пред колелото и продължих, а те тръгнаха да звънят на някого. Имам идея с кого, но не искам да спекулирам точно сега.

Сигналът през call.sofia пътува към районния кмет. Да видим дали този път ще направи нещо за разлика от десетките други подобни в района.

Това далеч не е първият подобен случай на територията на бъдещия Зелен ринг. Миналия август писах как буквално на метри от това място терен беше заграден и изравнен за сметище за строителни отпадъци, а тонове почвен слой – изхвърлен. В последствие се разбра, че извършителят е небезизвестният инвеститор Грийн Лайф стоящ туловището на Тинтява 80. Нашумя със схемата за ощетяване на купувачи на друг техен обект. В случая последствия за него нямаше тъй като районният кмет си изми ръцете, че било собственост на държавно предприятие. Нищо, че никой няма право да прави сметище дори на частен имот и най-малкото следва да задейства процедурата по санкциониране и премахване.

Подобно неглижиране и раздаване на държавни и общински имоти, както и изискванията за озеленяване и строителен контрол виждаме редовно и с всякакви мащаби. Ето няколко примера, за които съм писал през времето:

Залезът на варненския популизъм

Post Syndicated from Веселин Златков original https://www.toest.bg/zalezut-na-varnenskiya-populizum/

Залезът на варненския популизъм

Докато все още осъзнаваме резултатите от най-новите избори, можем с облекчение да отбележим едно: „варненската“ партия в следващия парламент ще е само една. Защо в кавички? Първо, „Възраждане“ отдавна е надраснала регионалния си произход. И второ, явлението „варненски политик“ надхвърля чисто географския си смисъл, защото предизвиква реакция едва когато се превърне в национален проблем.

Факт е, че за две десетилетия Варна даде на българския политически живот уникати като Веселин Марешки, Костадин Костадинов и Ивелин Михайлов. 

Има нещо гнило и този път не е в Дания. Но какво е то?

Провокации с думи и действия, съзнателно търсене на скандала в пленарната зала или на живо в телевизионното студио, вграден проруски уклон, завидно самочувствие и демонстративен манталитет – това са нещата, които дразнят най-много у „варненските“ народни избраници, особено у споменатите по-горе лидери. 

„Как все такива ги избирате, бе?!“ Тази реплика съм я чувал стотици пъти от хора, които не са от Варна. Истината е, че не ги избираме ние. И „Воля“, и „Възраждане“, и „Величие“ са постигнали резултатите си, които ги правят по някакъв начин важни, далеч от родния си град. А „Величие“ – далеч от родната си област. 

Новите проблеми на Варна
Варна като разказ за пропуснат шанс и за системно разминаване между амбиция и реалност. В града се строи повече, отколкото се живее, обещава се повече, отколкото се изпълнява. Между морето, имотите и провалените проекти наднича въпросът „Къде потъна потенциалът?“. От Веселин Златков.
Залезът на варненския популизъм

Варненските местни политици, не без доза самохвалство, обичат да казват, че варненският Общински съвет е нещо като лаборатория – каквото стане в него, скоро ще се повтори и в други градове, както и в държавата като цяло. В това може и да има някаква доза истина, но дори и да е така, изобщо не е повод за гордост. 

Като дългогодишен общински репортер лично мога да потвърдя, че именно в местния парламент се формира дразнещото поведение на „варненските“ политици. В него повечето съветници са представители не само на политическите си сили, а и на самите себе си – като част от неформални кръгове, браншове, съсловия, клубове, фамилии, ако щете и приятелски компании, често с голямо обществено влияние. 

И тъй като Варна не е толкова голям град, колкото ни се иска, винаги сред общинските съветници се пораждат лични конфликти. Понякога и с големи последствия. Марешки сигурно щеше още да е на политическата ни сцена, ако не беше ударил онзи прословут шамар на Костадин Костадинов, който в крайна сметка търкулна политическата му кариера по нанадолнището, за да се стигне до присъдата му за изнудване. Миналата година тя беше окончателно отменена от ВКС, като бизнесменът междувременно заяви, че е изгубил интерес към кандидатури и избори.

За Веселин Марешки политиката винаги е била застраховка за бизнеса му

Самият той е казвал, че законите, свързани с аптеките, са променяни поне пет пъти, за да се спре разрастването на веригата му. Влизайки в политиката, той получи възможност да заяви, че атаките срещу бизнеса му са заради това, че е критик на властта. И обратно – когато е атакуван политически, да каже, че това е опит разни сили да се намесят в бизнеса му. 

След като усети, че тази формула за постоянни оправдания работи, Марешки започна да прави каквото си иска, вдигна скандалния си „фитнес“ на плажа, построи си вила в Морската градина, купи от приватизираната БТК историческата Централна поща във Варна и я „украси“ с грамаден свой портрет. Фукаше се със скъпи коли и други причудливи превозни средства, започна да се държи арогантно с журналистите. Провокациите му (като да се появи в защитно облекло в Народното събрание в пика на ковид кризата) все по-често изглеждаха забавни единствено за него, но не и за избирателите му, привлечени основно с намаления в аптеките и бензиностанциите му. 

А при Костадин Костадинов нещата са съвсем различни 

Още във ВМРО той показа талант на професионален политик, както и умение да бъде достатъчно гъвкав в отношенията с конкурентите си, стига да има полза от това. Големият му пробив на местно ниво дойде на изборите през 2011 г., когато се оказа кандидат-кмет на много шарената коалиция „Варна утре“, съставена от ВМРО, „Новото време“, „Гергьовден“ и БНД, като последната тогава беше събрала най-популярните варненски фигури на разпадащото се НДСВ. 

Силната фигура зад коалицията беше Красен Кралев – бъдещ депутат от ГЕРБ и бъдещ спортен министър в две от правителствата на Бойко Борисов. В много любопитно интервю за „Дарик“ той обяснява, че вижда в Костадинов потенциален обединител на десницата във Варна. 

„Костадинов е всичко това, което останалите участници в кметската надпревара не са. Млад, суперинтелигентен, непокварен от изпълнителната власт, твърда и решима личност. Патриот!“, заявява Кралев. 

Днес и той, и Костадинов не обичат да говорят за това свое сътрудничество, реализирано във варненската политическа „лаборатория“. 

Бъдещият лидер на „Възраждане“ бързо показа, че обединител на десницата от него няма да излезе. Вместо това обидите и демонстрациите му срещу всяко възможно малцинство зачестиха и в крайна сметка се оказаха бързата писта към държавната политика, която той търсеше. 

Патриотична или националистична е българската диаспора?
Каква е политическата идентичност на българската диаспора? Този въпрос анализира Яна Хашъмова след последните изборни резултати и стабилния вот за „Възраждане“ в чужбина.
Залезът на варненския популизъм

Между другото, трябва винаги да се напомня откъде произлиза името на партията на Костадинов. Партия „Възраждане“ се появи на основата на инициативния комитет „Възраждане“, наречен на едноименния варненски жилищен квартал. Този комитет беше създаден заради проекта за изграждане на социален блок там.

Проектът, представен още през 2013 г., беше за осигуряване на жилища за хора с увреждания, пригодени специално за тях. В блока се предвиждаше да има и апартаменти за социално слаби лица. Костадинов и последователите му буквално насъскаха хората от квартала и ги наплашиха, че „ще им докарат цигани“. И жителите на „Възраждане“ се вдигнаха на протести, а Общината се отказа от проекта и обеща да намери друго място за социалния блок. Но и другите квартали се вдигнаха по същата схема, а хората с увреждания така и не си получиха жилищата.

Две години по-късно, през 2015-та, Общината се опита да рестартира проекта. Този път, вече организирана като партия, а не като гражданска структура, „Възраждане“ даде много по-шумен отпор на идеята.

След последните парламентарни избори Костадинов се представи като закрилник на страдащите и отритнатите и заяви, че левите избиратели могат да разчитат на „Възраждане“ като свой представител в парламента. Всеки да разбира това, както си иска. 

Ивелин Михайлов и „Величие” са другият ярък пример за „варненска политика“, който често се изтъква 

Това не е много справедливо, защото техният произход не е от община Варна, а от община Ветрино, но аналогията е ясна – варненския елемент в това серийно електорално чудо определено го има. 

В някои отношения политиката на Ивелин Михайлов прилича доста на тази на Веселин Марешки. Тя е функция за защита на бизнеса – ако някой го подлага на съмнение и проверки, се казва, че това е заради недоволството и критиките към властта; ако атаката е политическа, вади се обяснението, че е заради бизнес интереси. 

Къща от карти. Ще се скъса ли косъмът на „Величие“?
Съспенсът с партията на Ивелин Михайлов „Величие“ и нейното влизане в парламента продължава. Драмата е на много нива и работата е там, че все още никой не може да каже какво точно ще се случи, дори и да се променят последните изборни резултати. Емилия Милчева със статия по темата.
Залезът на варненския популизъм

„Величие“ обаче е съвсем различен феномен, при това не само заради факта, че е първият успешен пример за TikTok популизъм у нас. Проектът разчита на конкретна група хора, които търсят по-добър и по-смислен живот на село, обръщайки съзнателно гръб на града. А такива във Варненска област има много. Статистиката сочи, че към края на 2024 г. населението на град Варна се запазва и дори леко намалява, но пък жителите на областта се увеличават с над 3000 души. 

По-далеч от морето, но все пак близо, сред зеленина и спокойствие, с истинска храна от градината, но и с добра интернет връзка, без стреса на града и с много независимост, която не можеш да имаш в „мравуняка“ – тази идилична картина изкушава немалко варненци, които са запазили връзката си с региона. И като добавим и един „Исторически парк“, имаме си всичко. 

Ивелин Михайлов показа истинския си потенциал да е лидер на подобна общност в битката си с ветрогенераторите. По същия начин, по който Костадинов и „Възраждане“ не позволиха изграждането на социален блок и всеки варненски квартал, където се споменеше за проекта, се вдигаше на протест, така и „Величие“ настрои поредица от общини във Варненско срещу ветрогенераторите. За Михайлов стана ясно, че има основа за издигане на ново ниво, а ситуацията с недостигащите 21 гласа и всичко, което произлезе от това, придаде на партията му особен ореол в очите, отворени широко за всякакъв тип конспирации. Дали оставането извън парламента ще срине „Величие“, както стана с „Воля“ – това е въпрос на преценка на лидера. Но няма да се учудя „Величие“ да се възроди. 

И все пак защо всички тези явления идват от Варна? 

Обясненията са няколко и във всяко от тях има основание. Първото е, че варненци са просто наивни хора. В този случай обикновено се споменава рухването на финансовите пирамиди през 90-те, при което Варна се оказа най-сериозно засегната. Това промени много съдби и размести пластове в общността. Повечето хора, затънали в пирамидите, по детски вярваха, че ще се измъкнат преди рухването на измамните схеми. Мнозина бяха наясно в какво се забъркват, но решиха да пробват могат ли да измамят измамниците. 

Тарикатлъкът буквално беше завладял града като масова психоза, измествайки прагматичния скептицизъм, който сега доминира в мисленето на повечето варненци. Но урокът беше научен по трудния начин. А може би вече е забравен, кой знае?

COVID-19 за политическа употреба
Зорница Латева анализира вероятните фактори защо предвожданата от Костадин Костадинов партия „Възраждане“ събра близо 50 000 гласа повече спрямо изборите през април. Риториката на Костадинов на тема…
Залезът на варненския популизъм

Второто обяснение пак хвърля вината върху варненци. Те винаги се имат за нещо по-специално и повече, тресе ги местен шовинизъм и гласуват за „своите“. Освен мита за „лабораторията“ в местната политика във Варна има и друг – трябва да сме град държава. Специалният статус на „Морската столица“ – прозвище, което самите варненци вече използват само иронично, дълго време беше неизменна тема за кандидати за общински съветници и кметове. 

За кандидатите за депутати има друг мит – той е за „варненското лоби“, в което представители на враждуващи политически партии ще се обединят, за да защитят стратегическите интереси на града си. Което не се е случвало нито веднъж. 

Третото обяснение е малко по-различно. 

Варненци са като всички останали българи, но малко по-разочаровани. 

Годините на неадекватна или липсваща държавна политика в двете сфери, които определят съществуването на града – туризмът и морската индустрия, – изградиха огромно недоверие в централната власт. А оттам – в националните политици и партии. Често във Варна се виждат толкова неадекватни кандидатски листи от уж сериозни партии, че мнозина предпочитат да гласуват просто за други политици. „Варненски“, пък били те и очевидни популисти. Наивност, тарикатлък, разочарование – всеки сам да си избере обяснението. Важното е да има „критично мислене“, както каза големият нов победител. 

Fedora Linux 44 has been released

Post Syndicated from jzb original https://lwn.net/Articles/1070198/

The Fedora Project has announced
the release of Fedora Linux 44. There are “what’s new”
articles for Fedora
Workstation
, Fedora
KDE Plasma Desktop
, and Fedora
Atomic Desktops
. The Fedora Asahi Remix for Apple Silicon Macs,
based on Fedora 44, is also
available
. See the Fedora Spins page for a full list of alternative desktop options.

Fedora Linux 44 Workstation ships with the latest GNOME release,
GNOME 50. This comes with a long list of refinements to your desktop,
including everything from accessibility to color management and remote
desktop. Many of the applications that are installed by default on
Fedora Workstation have also seen improvements, from Document Viewer
to File Manager and Calendar. To learn more about these and other
changes, you can read the GNOME 50 release notes.

KDE Plasma Desktop: If you are a KDE user, you should also notice a
couple of very obvious changes. Fedora KDE Plasma Desktop 44 is based
on the latest Plasma 6.6, which includes the new Plasma Login Manager
and Plasma Setup to provide a more cohesive and integrated experience
from the moment the computer is powered on for the first time. The
installation process has been simplified, enabling you to easily set
up Fedora KDE Plasma Desktop for a computer for a friend or a loved
one.

The release
notes
include important changes between Fedora 43 and
Fedora 44 for desktop users, developers, and system administrators.

[$] Strawberry is ripe for managing music collections

Post Syndicated from jzb original https://lwn.net/Articles/1069368/

There are dozens of music-player applications for Linux; the options range
from bare-bones programs that only play local files to full-blown
music-management projects with a full suite of tools for managing (and playing)
a music collection. Strawberry
is in the latter category; it has a bumper crop of features, including smart
playlists, support for editing music metadata tags, the ability to organize music
files, and more.

In Memoriam: Tomáš Kalibera

Post Syndicated from jzb original https://lwn.net/Articles/1070185/

We have received the sad news that Tomáš Kalibera, a member of the
R Project core team, has
passed away
after a short illness
.

A friend who knew him well wrote to me: he was very happy, and
his work fulfilled him
. That is, perhaps, the best thing one can
say about a life in open source — that the work mattered, that it
reached millions, and that the person who did it found meaning in it.

Kalibera was mentioned in this 2019 article about C
programs passing strings to Fortran subroutines. He will be greatly
missed.

Get Motivated: What to Expect from Our Keynote at Rapid7’s Global Cybersecurity Summit

Post Syndicated from Emma Burdett original https://www.rapid7.com/blog/post/it-rapid7-global-cybersecurity-summit-keynote-rundown

Security teams prepare for incidents every day. Alerts are tuned, playbooks are built, and processes are tested. But when something actually happens, the challenge shifts. It becomes not just about making decisions under pressure, but how well that preparation has set teams up to make the right decisions when things heat up.

At this year’s Rapid7 Global Cybersecurity Summit, Persistence Under Pressure explores that shift directly. Former Special Forces operator Jason Fox draws on real-world experience where timing, clarity, and execution all have immediate consequences, and shows how that mindset applies to modern security operations.

In our keynote talk Persistence Under Pressure, former Special Forces operator Jason Fox brings experience from environments where timing, clarity, and execution all have immediate consequences. His session looks at how that mindset translates into modern security operations, where teams are expected to act quickly, often without complete information.

The parallels are clear: Incidents do not unfold in controlled conditions. Signals compete for attention, priorities shift, and decisions need to be made in real time. What matters in those moments is not just having the right tools, but knowing how to stay focused and act with confidence.

This session explores practical ideas that apply directly to security teams, from how preparation shapes response to how understanding the adversary influences decision-making, and why composure and clarity can make the difference when pressure builds.

It also reinforces a broader theme running throughout the summit. Preemptive security operations are not only about detecting threats earlier but about enabling better decisions across the entire lifecycle, from preparation through to response and recovery.

If you are looking to understand how security operations are evolving, this session offers a different but valuable perspective. One that connects strategy and technology back to the people responsible for making it work.

Join us May 12–13 and hear how these principles apply in practice. Register now.

Георги Гочев: Животът е усилие да овладеем изкуството на раздялата

Post Syndicated from Роси Михова original https://www.toest.bg/zhivotut-e-usilie-da-ovladeem-izkustvoto-na-razdyalata/

Въпросите задават духът Якша, цар Менандър I и Роси Михова

Георги Гочев: Животът е усилие да овладеем изкуството на раздялата

Знаете ли, че най-дългият литературен епос в световната история е „Махабхарата“? За негов автор се смята мъдрецът Вяса – основополагаща фигура в древноиндийската духовна традиция и познавач на свещените текстове на индуизма – Ведите. Твърди се, че Вяса е живял около 800 години – по-точно между IV век пр.Хр. и IV век сл.Хр. В този период той някак успява да събере и подреди 100 000 двустишия, групирани в 18 книги, в които се разказва за 18-дневната война между 18 армии. За сравнение, това е около десет пъти повече от „Илиада“ и „Одисея“, взети заедно.

Разбира се, съществува и другата възможност – антични бардове като Вяса и Омир, макар и с ореола на исторически личности, да са просто събирателен образ на куп безименни поети и разказвачи, пътуващи певци, аскети и оракули, които са пренесли до нас текстовете на древността. Така или иначе, техните думи ни застигат и днес.

Един от емблематичните откъси в „Махабхарата“ са въпросите, които духът Якша задава на принц Юдхищхира, за да прецени дали да съживи братята му от рода Пандави. Принцът се справя безупречно с отговорите, демонстрирайки проницателност, фантазия и смиреност. 

Тези въпроси обаче са детски гатанки в сравнение с въпросите, които се появяват в Упанишадите – философски трактати от VIII–II век пр.Хр., които бележат прехода от ритуализма на Ведите към индуистката метафизика. Самото име Упанишад произлиза от санскритските корени upa (наблизо), ni (долу) и shad (седя) и буквално описва ученик, който седи в краката на своя учител и му задава въпроси.

Днес бихме казали, че Древна Индия е влюбена в диалога като литературен жанр, затова играта на въпроси и отговори далеч не се ограничава с класическите образци, написани на санскрит. Пример за това е будисткият текст „Милинда Панха“ (II–I век пр.Хр.), чието заглавие в превод от езика пали означава „Въпросите на Милинда“.

Сюжетно това е витиеват, търпелив разговор между гръцкия цар Менандър I и будисткия мъдрец Нагасена. На практика обаче е челен сблъсък между елинския логос с неговия фокус върху логиката, анализа и външния свят и източното взиране в интуицията, вътрешното преживяване и мистично познание. Гъркът иска да разбере Вселената. Индиецът иска да се слее с нея.

А какво иска Георги Гочев*, предстои да разберем. Защото кой друг би могъл да отговори по-добре на въпросите на Якша и Менандър I от един дипломиран класически филолог, изтъкнат преводач от старогръцки език и тънък познавач на Платон и Аристотел?

В този наш разговор въпросите на индийските мъдреци са само отправна точка за свободен размисъл. Събеседването ни е отвъд усмирителната риза на конкретния исторически и културен контекст на литературните източници.


Доцент Гочев, ще Ви помоля за момент да си представите, че сте принц Юдхищхира и Ви предстои да отговорите на поредица от блицвъпроси. От Вашата убедителност зависи съдбата на цялото Ви семейство, на царството Ви и на космическия ред. И така, кой е по-голям от земята, кой е по-висок от небето и кой е по-бърз от вятъра?

Краткият ми отговор и на трите въпроса е един и същ. И той е не. Виждам недоумението Ви и ще обясня. Често привидно директните въпроси носят завоалиран, скрит смисъл. Мисля, че зад въпроси от типа кой е най-голям, кой е най-висок, най-бърз, най-силен, всъщност стои въпросът: Колко съм силен аз самият? Мога ли да покоря света? Мога ли да го владея? И моят отговор на това е не. Не мога. Защото това са царски въпроси – такива, каквито си задават царете. Аз обаче не съм цар и нямам подобни терзания. Те са за хора, които се питат колко дълго могат да управляват, докъде се простира властта им, колко ефективна е тя. Хора като Тръмп или Путин например. Мен ме питайте нещо друго.

Добре. Кой е най-добрият приятел?

Това също е въпрос, от който изскача друг по-важен въпрос – какво е приятел? В моето разбиране приятел е човек, заедно с когото мога да живея живота си като свой – да живея собствения си, а не нечий чужд живот.

Кой е врагът, който най-трудно може да бъде победен?

Този, който се преструва на приятел.

Коя е най-страшната болест?

Животът в неистина.

Кое е най-ценното притежание?

Свободата, разбирана като способност да се разделяме с нещата от живота. Защото животът може да бъде описан като поредица от раздели и загуби. С раждането си ние губим утробата. После губим детството, невинността, илюзиите. Губим приятели, родители, партньори, не дай боже – дете. Губим сили, губим енергия. И накрая губим себе си. Животът е усилие да овладеем изкуството на раздяла с нашите притежания.

В диалога „Федон“ Платон дава дефиниция за това какво е философията. Според него тя е подготовка за смъртта – за раздялата на тялото с душата. Човек – съзнателно или не – цял живот се готви за момента, в който ще загуби това свое най-ценно притежание. А то е ценно точно защото предстои да бъде изгубено. Именно загубата придава ценност на нещата. Без нея те нямат особена стойност. Без смъртта безсмъртието е тривиално.

Кое е най-горчивото нещо?

Илюзията. Какво казва принцът по този въпрос?

Юдхищхира казва, че най горчи това да зависиш от други хора. А какво е мъдростта?

Способността да живееш с вътрешните си противоречия, без да се опитваш да ги решиш или преодолееш.

Кой е най-големият парадокс на света?

Това, че хората не се блъскат един в друг, когато вървят по улицата. Обяснението ми е, че в желанието си да живеем живота си като свой ние приемаме, че и другите искат същото. Поради това им осигуряваме нужното пространство, като налагаме определени граници на своето. Ако не го правехме, щяхме да се блъскаме, докато заседнем в някакво гигантско човешко задръстване. Всъщност парадоксът е в това, че за да живеем свободно, се налага задължително да се самоограничаваме.

Вирджиния Улф го казва много хубаво на едно място в „Мисис Далауей“. Най-голямата загадка е, че тук има една стая, а там – друга. Че ме има мен, но го има и другия човек в отсрещната сграда. И по някакъв начин сме свързани, дори и да не се познаваме.

Мисля, че с този отговор засега опазваме вселенския порядък и можем да преминем към няколко въпроса, формулирани в Упанишадите. И така: Какво у човека спи всяка нощ? Какво винаги дреме у негo? Будни ли сме, когато сънуваме? (Прашна Упанишад)

Аз гледам на сънищата като на време, в което човек успява да говори със себе си по начин, различен от този, когато е буден. В този смисъл умът ни е буден, когато сънуваме. Буден по различен начин.

Добре, ако всяка нощ сънуваме, че сме господари, а всеки ден живеем като слуги, какви сме всъщност тогава? (Мандукя Упанишад)

Голямата разлика между господаря и слугата е привидна. В много отношения господарите са не-господари, защото се подчиняват на редица условности и очаквания. В много отношения слугите и робите са по-свободни, защото от тях не се изисква да вземат решения.

Аз винаги питам студентите дали знаят колко робски въстания е имало в Рим. Истината е, че те са много малко. За социална организация, просъществувала над 1000 години, документираните робски въстания се броят на пръстите на двете ми ръце. Защо робите не са поискали свободата си?

Защото в робството има поне две „свободи“ или подобия на свободи, които са невидими. Първата е свободата от отговорност да правиш житейски избори. Втората е свободата от идентичност. Като роб ти нямаш грижата да търсиш и да утвърждаваш себе си. Ти си закачен за идентичността на своя господар.

Искам да кажа, че влезем ли в тази парадигма на господаря и слугата, то едното винаги отчасти се съдържа в другото. Ние не можем да бъдем нито само слуги, нито само господари.

На този въпрос през IX век прочутият индуистки философ и поет Шанкара отговаря по следния начин. Докато сънуваш, че си господар, твоето щастие е истинско и твоята власт е реална в рамките на съня. Докато си буден и си слуга, ти наистина не си нищо повече от слуга. И тъй като двете състояния се изключват взаимно, то и двете са относителна реалност. Но ако помниш едновременно и съня на господаря, и живота на слугата, то значи ти си нещо по-голямо от тях двамата. Ти си „наблюдателят“.

Интересно е, че съвременната психоанализа предлага сходна интерпретация. Слугата е препратка към социалната ни роля, на чиито изисквания се подчиняваме всеки ден. Господарят е нашето несъзнавано, копнежите и чувствата ни, неподвластни на контрол. Тогава какви сме всъщност? Ние сме процесът на интегриране на тези две противоположности. Или както казахте преди малко – на практикуване на мъдростта да живеем в противоречията си, без да се опитваме непременно да ги преодолеем. Истинското ни аз е това, което помирява слугата и господаря.

Истината е, че този въпрос е подвеждащ, защото веднага те дърпа да интерпретираш какво е да си господар, какво е да си слуга. Но сега, като се разговорихме, чувам две други неща в него.

Едното е темата за часовете. Ние сме времеви същества. Времето ни на живот е ограничено и в този смисъл ние сме ограничени, ние сме слуги на този свят.

Второто е свързано с вътрешния ни диалог. Ние непрекъснато разговаряме със себе си по тази линия – господар/слуга и си заповядваме разни неща. Но границата кой върху кого господства, е много тънка. Защото съвестта и самозаблудата идват от едно и също място. Съвестта често е безкрайно нечестна с нас. Тя ни подвежда, че знаем какво е добро и какво е истина, но понякога ни предлага неистини. Мирното съвместно съществуване между царя и слугата върви с непрекъсната размяна на ролите и съзнателност за тази размяна. И когато вътрешният ни глас се включи с някоя реплика, съвет или заповед, много трудно можем да сме сигурни кой от двамата я произнася – господарят или слугата.

Смятам, че част от умението да живеем добре се състои в способността ни да не се държим вътре в себе си като цар и роб. Като диктатор и поданик. А да водим спокоен вътрешен диалог.

Кое е това нещо, чрез познанието на което всичко останало в този свят става познато? (Мундака Упанишад)

Дълбоко не вярвам, че има универсален ключ за разбиране на света и вселената.

Аз съм адепт на сократо-платоническата традиция, в която важното изречение не е „Еврика! Открих! Намерих ключа!“, а изречението „Знам, че не знам“. Това не е капитулация пред обема на непознатото. То е капитулация пред претенцията, че можеш да познаеш всичко. Освен това то е и вид етическа нагласа. Защото омнисциенцията е илюзия за омнипотенция.

Но искам да поразсъждавам още малко по въпроса. По принцип, когато изследваме или интерпретираме каквото и да било (думи, действия, поведения, знаци), ние задаваме два въпроса – защо и какво. Цялата западна култура от времето на Аристотел е ориентирана по линията на причинно-следствените връзки. Цялото ни образование е фокусирано върху въпроса защо с убеждението, че ако можем да отговорим на него, можем да отговорим и на всички останали въпроси.

Изтокът обаче (Изтокът, видян много на едро) си задава по-скоро въпроса какво. Какво е това? Този въпрос поставя питащия не в позиция на човек, който владее инструментите на познанието и може да стигне от факта до причината, а в ролята на наблюдател, на съзерцател.

Мисля, че ние надценяваме въпроса защо за сметка на какво. Ето Ви пример. Вълнува ме повече какво се е случило в Петрохан, а не защо се е случило. Бих искал, преди да питаме защо е станало това, да попитаме: „Какво всъщност е това?“ Мисля, че тогава ще видим картината в нейната по-голяма сложност, детайли и дълбочина. И няма да се подвеждаме само по водещите причинно-следствени връзки.

Тук стигаме до въпросите на гръцкия цар Менандър I, които той задава на монаха Нагасена, опитвайки се да открие логически пробойни в уредбата на будистката етика. И така, достоен ли е за уважение човек, който убива определен брой хора, за да спаси живота на повече хора, които иначе биха загинали, ако той не направи нищо? Тук бих добавила – доколко моралната стойност на нашите постъпки се определя от тяхната полезност?

Това е познатият мисловен експеримент с трамвая. Въпросът е дали бих дръпнал ръчката и бих го отклонил в друг коловоз, за да спася петима, завързани на релсите, но с цената на живота на един човек, завързан на другите релси. Първо, да не дава господ да изпадна в подобна ситуация. Тази морална аритметика колко на брой спасени живота оправдават колко на брой убийства, ми е дълбоко чужда. И смятам, че тя е част от същото това царско мислене, в което ти се възприемаш като господар на чужди животи.

В будизма има един принцип, който според мен осветява дълбината на това учение – „Не помагай другиму“. Защо да не му помагаш? Защото така се бъркаш в кармата му. Нашата идея за страданието е, че хората страдат незаслужено. Но в будистката парадигма, ако някой страда, то е, за да се излекува от грешки, направени в този или в предишни животи. И това е смисълът на съвета да не се бъркаш в кармата на чуждия живот. Не искам да съм нито спасител, нито погубител.

Цар Менандър I продължава да пита: Aко човек страстно желае да открадне нещо, но в крайна сметка не го прави, носи ли душата му товара на греха, защото той вече е съгрешил в помислите си? От съвременна гледна точка – носим ли вина за мислите си?

Не, не можем да носим вина за нещо, върху което нямаме никакъв контрол. Претенцията, че можем да владеем мислите и чувствата си, ми изглежда опасна. Това, което можем да управляваме, поне в някаква степен, са действията ни. Затова по-почтен е не този, който изобщо не си помисля да открадне, а онзи, който го мисли и има възможност да го направи, но въпреки това не го прави. Светостта или стоицизмът, смятам, не е в липсата на лоши помисли и пагубни емоции; светостта или стоицизмът, ако питате за тях, са в устояването пред лоши помисли и емоции.

Но ако не носим вина за мислите си, защо тогава законът наказва по-сурово умишленото в сравнение с неумишленото престъпление?

Винаги ще има вътрешни противоречия между намеренията и резултата от нашите действия. Но въпросът дали нашите намерения определят постъпките ни като добри или лоши, е в същината си детински въпрос. Децата и незрелите възрастни са тези, които оправдават своите грешки с добри намерения или с незнание.

Тогава за кого позорът е по-голям – за този, който умишлено причини зло, или за този, който причини зло поради незнание?

Тук юристите може да скочат срещу мен, но аз не правя голяма разлика между двете. Убеден съм, че дори злодеите в своята самоувереност не са истински наясно с това, което правят. Те си въобразяват, че знаят, но моментът на осъзнаване, ако изобщо го има, настъпва по-късно.

Будисткият монах е доста по-категоричен от Вас. Според него злото, причинено от незнание, а не с умисъл, е много по-страшно. И дава пример: кой ще се изгори повече – този, който грабва горещото желязо, знаейки, че може да се опари, или този, който го прави, без да подозира, че ще се опари? По неговата логика пораженията, причинени от невежество, са по-опасни. А незнанието, породено от леност на ума, се превръща във вид морално престъпление.

Може би. Но като човек, който работи в сферата на образованието, виждам как всекидневно преживяваме краха на голямата илюзия, че просвещението ще спаси света. Имам предвид убеждението, че ако просветите хората, ако им отворите очите за всички религиозни, културни, идеологически и политически догми в нашия живот, те ще станат по-добри и разумни. Този просвещенски проект, започнал в края на XVIII век, Кант онагледява по следния начин. Какво е просвещението? Това е да извадиш хората от състоянието на детството, което те са си самопричинили. Вярата, че като ги образоваш, хората стават възрастни, които са способни да поемат отговорност за живота си и да действат според разума.

И ние продължаваме да живеем в тази парадигма, в която знанието и информацията са върховна ценност. Зад замисъла на глобалната дигитална мрежа стои вярата, че свободно достъпното знание ще направи хората по-разумни в техните избори. Но нищо такова не се случва. Защо? Защото хората не действат единствено под диктата на разума. Дори когато са наясно например кои новини в интернет са фалшиви и кои – не, те избират не според истината, а според емоцията си. А когато става въпрос за чувства, разумът е безсилен.

Пренесете това на политическия терен. Има партии, които последователно градят образа си като глас на разума. Но не гласът на разума е това, което привлича хората. Още повече че когато някой говори разумно, той често го прави назидателно, дори осъдително. А избирателите имат и други, емоционални нужди. Те очакват от политиците да признаят съществуването им през техните емоции. Да чуят от тях, че имат право да са гневни и ядосани, имат право да грешат или да вярват в глупости.

Тогава за финал да се върнем на въпроса на духа Якша: какво е щастието?

В аналитичен план щастието се свежда до това да обичаш и да работиш. В личен план за мен щастието е дълъг неделен обяд. Така си го представям. И когато питате кой е приятел, то приятел е човек, когото бих поканил на дълъг неделен обяд.


* Георги Гочев е класически филолог, преводач от старогръцки език и доцент по класически езици и литератури в Нов български университет. От 2024 г. е заместник ректор по международната дейност на НБУ и ръководител на университетския консорциум ЕРУА за НБУ.

Превел е от старогръцки език „Държавата“ и „Пир“ на Платон, „Поетика“ на Аристотел, трагедията „Медея“ на Еврипид. Носител е на националните награди „Христо Г. Данов“ за 2016 г. (раздел „Хуманитаристика“) и наградата за хуманитаристика „Богдан Богданов“ (2019).
Security updates for Tuesday

Post Syndicated from jzb original https://lwn.net/Articles/1070184/

Security updates have been issued by Debian (openjdk-21 and webkit2gtk), Fedora (botan3, chromium, cockpit, firefox, flatpak, gum, libarchive, libcoap, mingw-python3, ngtcp2, nss, openssh, openssl, openvpn, PackageKit, python3-docs, python3.11, python3.12, python3.13, python3.14, vim, and xrdp), Oracle (firefox, gdk-pixbuf2, java-1.8.0-openjdk, java-21-openjdk, python3.12, python3.9, sudo, and tigervnc), Red Hat (tigervnc and xorg-x11-server-Xwayland), Slackware (mpg123 and proftpd), SUSE (emacs, firefox, fontforge, freeciv, freerdp, libngtcp2-16, libsystemd0, and strongswan), and Ubuntu (authd, clamav, glance, haproxy, jq, lcms2, nginx, nltk, ntfs-3g, packagekit, pillow, strongswan, and vim).

Shutdowns, power outages, and conflict: a review of Q1 2026 Internet disruptions

Post Syndicated from David Belson original https://blog.cloudflare.com/q1-2026-internet-disruption-summary/

In the first quarter of 2026, government-directed shutdowns figured prominently, with prolonged Internet blackouts in both Uganda and Iran, a stark contrast to the lack of observed government-directed shutdowns in the same quarter a year prior. This quarter, we also observed a number of Internet disruptions caused by power outages, including three separate collapses of Cuba’s national electrical grid. Military action continued to disrupt connectivity in Ukraine and also impacted hyperscaler cloud infrastructure in the Middle East. Severe weather knocked out Internet connectivity in Portugal, while cable damage disrupted connectivity in the Republic of Congo. A technical problem hit Verizon Wireless in the United States, and unknown issues briefly disrupted connectivity for customers of providers in Guinea and the United Kingdom.

This post is intended as a summary overview of observed and confirmed disruptions and is not an exhaustive or complete list of issues that have occurred during the quarter. A larger list of detected traffic anomalies is available in the Cloudflare Radar Outage Center. Note that both bytes-based and request-based traffic graphs are used within this post to illustrate the impact of the observed disruptions, with the choice of metric generally made based on which better illustrates the impact of the disruption.

Government-directed shutdowns

Uganda

In advance of the January 15 presidential election, Ugandan authorities ordered a nationwide Internet shutdown. The Uganda Communications Commission (UCC) instructed mobile network operators to suspend public Internet access, effective 18:00 local time (15:00 UTC) on January 13. The UCC reportedly defended the shutdown as necessary to “curb misinformation, disinformation, electoral fraud and related risks.” Domestic traffic at the Uganda Internet Exchange Point (UIXP) dropped from approximately 72 Gbps to 1 Gbps as a result of the action taken.

Similarly, Cloudflare data shows a near-complete loss of traffic from Uganda coincident with the start of the shutdown, with traffic remaining effectively at zero through 23:00 local time (20:00 UTC) on January 17, when Internet connectivity was partially restored after incumbent President Yoweri Museveni was declared winner of his seventh term. 

Full Internet restoration was announced by the UCC on January 26, with mobile network operators MTN Uganda and Airtel Uganda both confirming on social media that restrictions had been lifted. The shutdown prompted lawsuits against UCC and the telecoms companies and drew criticism from digital rights organizations including CIPESA.

Uganda also blocked Internet access during its 2021 election. Authorities had repeatedly promised this time would be different, stating as recently as January 5 that “claims suggesting otherwise are false, misleading.”

Iran

Iranian citizens spent a large part of Q1 2026 offline, or with severely limited connectivity, due to two nationwide Internet shutdowns. The first began around 20:00 local time (16:30 UTC) on January 8, and we explored the impact seen over the first few days in our What we know about Iran’s Internet shutdown blog post. Traffic from Iran remained near zero until January 21, when a small amount of traffic returned, only to disappear a little over 24 hours later. A similar brief restoration also occurred on January 25, before traffic recovered more aggressively starting on January 27.

A near-complete loss of announced IPv6 address space started several hours before the drop in traffic took place on January 8. Asiatech (AS43754) was by far the single largest contributor, losing 4.46 million /48-equivalents, accounting for ~9.4% of Iran’s entire IPv6 space loss on its own. RASANA (AS31549) was the second-largest, losing 4.19 million /48-equivalents (~8.8% of the country total). As would be expected, this resulted in the share of IPv6 traffic in Iran going to zero. Given the gap in timing between this change and the loss of traffic across the country, this may have been a leading indicator of what was about to happen, but likely not a direct cause of it. Some nominal shifts in announced IPv4 address space are visible during the shutdown, but levels remained fairly consistent during the shutdown period. These observations suggest that the shutdown was implemented by other means, such as filtering.


Cloudflare Radar social media posts (X, Bluesky, Mastodon) throughout January and into early February documented our observations about the state of connectivity in Iran over the course of that month.

On February 28, as military strikes on Iran escalated, a second nationwide Internet shutdown began. Cloudflare Radar observed a sharp drop in traffic from Iran beginning around 10:30 local time (07:00 UTC). Traffic levels fell to well under 1% of previous levels, with only small amounts of Web and DNS traffic egressing the country.

No significant shifts in announced IP address space were observed around the onset of this shutdown. IPv4 space remained fairly consistent, and IPv6 space remained consistently volatile, suggesting that route withdrawals were not the cause of this second shutdown.

The continued announcement of IP address space, and the presence of traffic from the country, even if just a small amount, supports reports that the shutdown was effectively achieved through aggressive filtering, with so-called “whitelists” and “white SIM cards” restricting access to only approved Internet sites by selected users.

Iran remained effectively offline through the end of the quarter. As of late April, this shutdown remains largely in place, making it one of the longest sustained Internet disruptions observed in recent years.

Republic of Congo

On March 15, as the Republic of Congo held a presidential election expected to extend President Denis Sassou Nguesso’s 42-year rule, a near-complete shutdown of Internet connectivity was observed in the country. Traffic from the country dropped precipitously around 06:30 local time (05:30 UTC), falling to near zero for approximately 60 hours through the election period and its immediate aftermath. Traffic began recovering around March 17 at 18:20 local time (17:20 UTC), rapidly returning to pre-shutdown levels. While Congolese authorities provided no official explanation for the drop in traffic, similar shutdowns were put into place during the 2021 and 2016 elections.

Military action

Ukraine (Dnipropetrovsk)

On January 7-8, Russian attacks on energy infrastructure in Ukraine caused power outages that disrupted Internet connectivity in Dnipropetrovsk and surrounding regions. Cloudflare Radar observed a significant drop in traffic from the region, reaching nearly 50% below the prior week’s levels, starting around 22:45 local time (20:45 UTC) on January 7. Recovery began approximately 06:00 local time (04:00 UTC) on January 8.

Ukraine (Kharkiv)

On January 26, Russia launched a drone and missile attack targeting energy infrastructure in Kharkiv. Cloudflare Radar observed an approximately 50% drop in traffic from the region beginning around 19:15 local time (17:15 UTC). Recovery progressed through January 27 as power was gradually restored.

Amazon Web Services Middle East (United Arab Emirates and Bahrain)

One of the most unusual disruptions of the quarter was the physical damage inflicted on Amazon Web Services data centers in the Middle East by drone strikes tied to the ongoing regional conflict. On the morning of March 1 (UTC), Amazon reported a fire started after objects hit a UAE data center. The following day, the company confirmed that two of its facilities in the United Arab Emirates (me-central-1 region) were “directly struck” by drones and that a facility in Bahrain (me-south-1 region) was also taken offline after being damaged by a nearby strike.

Cloudflare’s Cloud Observatory data showed elevated connection failure rates for the me-central-1 and me-south-1 regions beginning March 1-2 and remaining higher for multiple days. Connection failures occur when Cloudflare fails to successfully connect to an origin server when attempting to retrieve uncacheable content, or content not in/expired from cache. These graphs illustrate the increased rate of failures experienced when attempting to connect to servers in these impacted regions.

In a status post on the AWS Health Dashboard, Amazon acknowledged: “These strikes have caused structural damage, disrupted power delivery to our infrastructure, and in some cases required fire suppression activities that resulted in additional water damage.” The company warned that instability was likely to continue in the Middle East, making operations “unpredictable,” and urged customers with workloads in the affected regions to back up their data or migrate to other AWS regions.

The AWS me-south-1 region in Bahrain suffered an additional disruption on March 23, following further drone activity.

Power outages

Argentina (Buenos Aires)

On January 15, a power outage struck Buenos Aires during a summer heat wave. The outage caused nominal disruptions in Internet connectivity for customers of multiple providers in the Buenos Aires area, including Telecom Argentina (AS7303), Telecentro (AS27747), and IPLAN (AS16814), with traffic from these networks dropping between 17:30 and 19:30 local time (20:30 – 22:30 UTC). Traffic returned to expected levels approximately two hours after the outage began.

Moldova and Ukraine

An emergency power cut on Ukraine’s electricity grid on January 31 caused widespread power outages affecting Moldova and several Ukrainian regions including Kyiv and Kharkiv. Moldova was reportedly hit by widespread power cuts amid the Ukrainian grid problems, and the Ukrainian Energy Minister explained the cross-border impact, noting “Today at 10:42 a.m. (08:42 GMT), a technical malfunction occurred, causing a simultaneous shutdown of the 400 kilovolt line between the power grids of Romania and Moldova and the 750 kilovolt line between western and central Ukraine.” Traffic from Moldova, Kyiv, and Kharkiv began falling around 10:42 local time (08:42 UTC), reaching as much as 46% below the prior week, with recovery occurring around 14:00 local time (12:00 UTC).

Paraguay

On February 18, widespread power outages struck Paraguay after key transmission lines went out of service. The National Electricity Administration (ANDE) posted a series of updates on X documenting the incident and efforts to restore power. Internet traffic from Paraguay dropped as much as 72% compared to the prior week beginning around 15:15 local time (18:15 UTC), and the disruption lasted nearly three hours, with recovery occurring by approximately 18:30 local time (21:30 UTC).

Dominican Republic

A major failure in the Interconnected National Electric System (SENI) of the Dominican Republic caused a widespread power outage on February 23. The state-owned electric company Empresa de Transmisión Eléctrica Dominicana (ETED) posted updates on X documenting the failure and the recovery effort. Internet traffic from the country dropped sharply beginning around 10:50 local time (14:50 UTC), and recovered around midnight local time (04:00 UTC) on February 24, in line with a confirmation posted by ETED that “The authorities of the electric sector reported that the Interconnected National Electric System (SENI) was fully restored to 100% at 11:53 p.m. on this Monday…”.

Cuba

Cuba experienced three separate collapses of its National Electric System (SEN) during March, each causing widespread Internet disruption, reflecting the severe deterioration of the country’s electrical infrastructure. (Power outages also disrupted Internet connectivity in Cuba during September and March 2025, and October 2024.) 

The first collapse occurred on March 4, when a disconnection of Cuba’s National Electroenergy System cascaded from Camagüey to Pinar del Río, cutting power to the western half of the island, including Havana. OSDE/UNE (Cuba’s Electric Union) confirmed the failure on social media. Cloudflare Radar data showed traffic from the island dropping by nearly half beginning around 12:15 local time (17:15 UTC), with traffic recovering by approximately 05:01 local time (10:01 UTC) on March 5.

The second collapse occurred on March 16, when Cuba’s entire National Electric Power System was disconnected. EnergíaMinas Cuba posted updates on the situation on X. Cloudflare Radar data again shows a significant loss of traffic from Cuba beginning around 13:35 local time (17:35 UTC) on March 16, dropping approximately 65%. Traffic returned to expected levels by approximately 20:00 local time on March 17 (00:00 UTC on March 18), with the disruption lasting over 30 hours.

The third collapse (the second in just a week) happened just days later, on March 21-22. EnergíaMinas Cuba and OSDE/UNE again provided situation updates via X. Cloudflare Radar data shows another significant loss of traffic from Cuba beginning around 18:30 local time (22:30 UTC) on March 21, falling as much as 77% compared to the previous week. Traffic recovered around 21:39 local time on March 22 (01:39 UTC on March 23).

U.S. Virgin Islands

According to a Facebook post from the Virgin Islands Water and Power Authority (WAPA) on March 24, a loss of generation at the Richmond Power Plant combined with damage to an underground cable caused a power outage affecting St. Croix and St. Thomas in the U.S. Virgin Islands. Cloudflare Radar data shows traffic from local provider VI Powernet (AS14434), the primary ISP for the U.S. Virgin Islands, dropping to near zero beginning around 12:15 local time (16:15 UTC), with recovery occurring by approximately 14:45 local time (18:45 UTC). Although VI Powernet experienced a near-complete outage, traffic from St. Thomas only fell by around 60%, and approximately 40% from St. Croix due to the presence of other providers.

Severe weather

Portugal

Storm Kristin made landfall in Portugal on January 28, causing widespread damage and power outages across the country. Approximately 1,500 incidents were registered by Civil Protection between midnight and 08:00 local time (00:00 – 08:00 UTC), with the hardest-hit areas being the districts of Leiria and Coimbra. Significant infrastructure damage was reported, and by 07:00 local time (07:00 UTC), over 850,000 E-Redes customers were without electricity.

The associated power outages disrupted Internet connectivity across Portugal, which Cloudflare Radar observed primarily in the regions of Leiria, Santarém, and Coimbra beginning around 04:10 local time (04:10 UTC) on January 28. Internet traffic dropped as much as 70% in Leiria, and 52% in Coimbra.

Recovery was slow: over 290,000 customers remained without power as late as January 30, and Cloudflare continued tracking gradual recovery of regional traffic over the following weeks. (Coimbra returned to expected levels within the first several days after the storm.) More than three weeks after the storm, over 6,000 customers in Leiria reportedly remained without electricity.

Cable damage

Republic of Congo

Just after the New Year, Internet connectivity in the Republic of Congo was disrupted by an incident on the WACS (West Africa Cable System) submarine cable. Congo Telecom (AS37451) posted on X announcing “an international incident on the WACS cable” was causing Internet disruptions, and stating that backup solutions had been activated. Cloudflare Radar observed a significant drop in traffic from Congo beginning around 00:00 local time on January 2 (23:00 UTC on January 1), falling to 82% below expected levels. A follow-up post from Congo Telecom confirmed that repairs were ongoing, with users potentially experiencing slowdowns during peak hours. Traffic returned to expected levels by approximately 15:00 local time (14:00 UTC) on January 4.

Technical problems

Verizon Wireless (United States)

On January 14, a software issue impacted voice and data services for customers of Verizon Wireless (AS6167) across the United States. Verizon published an official statement acknowledging that the outage began January 14 and that by 22:15 ET (03:15 UTC on January 15) the issue had been resolved. Multiple updates on X from @VerizonNews kept subscribers informed throughout the evening. Cloudflare Radar data shows a minor drop in traffic beginning around 12:30 ET (17:30 UTC) on January 14, consistent with the reported onset of the outage.

Grenada

On February 9-10, customers of Flow Grenada (AS46650) – the primary Internet provider serving Grenada – experienced an island-wide service disruption lasting approximately 12 hours. The provider posted on Facebook acknowledging a service disruption, though no details about the root cause were provided. Cloudflare Radar data shows traffic from the network initially dropping around 11:30 local time (15:30) UTC on February 9, disappearing completely around 20:00 local time (midnight UTC on February 10), and recovering by approximately 23:30 local time (03:30 UTC on February 10). Routing data shows a complete loss of announced IPv4 space at the same time traffic dropped to zero. Major spikes in BGP announcements around the time the disruption initially started, and bookending the complete outage, suggest that the whole event may have been routing-related.

Unknown cause

Orange Guinée (Guinea)

Customers of Orange Guinée (AS37461) in Guinea were unable to make phone calls or access the Internet starting around 10:45 local time (10:45 UTC) on January 6. Orange Guinée subsequently confirmed an “exceptional breakdown” affecting mobile phone and Internet services due to a technical incident, with teams mobilized to restore service. Service was restored by approximately 14:00 local time (14:00 UTC) that same day. No further details on the root cause of the incident were publicly disclosed.

TalkTalk (United Kingdom)

On March 25, customers of UK broadband provider TalkTalk (AS13285) reported widespread service disruptions. TalkTalk acknowledged the issues on X but did not publicly disclose a root cause. Cloudflare Radar observed traffic from the provider drop nearly 50% as compared to the previous week beginning around 07:00 local time (07:00 UTC), with service restored by approximately 08:15 local time (08:15 UTC).

A quarter marked by major disruptions

The first quarter of 2026 was marked by an unusually high number of severe and prolonged Internet disruptions. The major government-directed shutdowns, particularly the extended blackouts in Uganda and Iran, underscore how Internet access continues to be weaponized as a tool of political control. Cuba’s three separate national grid collapses in a single month paint a troubling picture of infrastructure fragility with direct consequences for connectivity. And the drone strikes on AWS data centers in the Middle East represent an unprecedented escalation as active military conflict directly and physically damaged major cloud infrastructure, with disastrous consequences for the websites and applications hosted there.

The Cloudflare Radar team is constantly monitoring for Internet disruptions, sharing our observations on the Cloudflare Radar Outage Center, via social media, and in posts on blog.cloudflare.com. Follow us on social media at @CloudflareRadar(X), noc.social/@cloudflareradar (Mastodon), and radar.cloudflare.com (Bluesky), or contact us via email.

Network Stats for Q1 2026: Neocloud Traffic Trends

Post Syndicated from Brent Nowak original https://www.backblaze.com/blog/network-stats-for-q1-2026-neocloud-traffic-trends/

A decorative image with the words Q1 2026 Network Stats.

Welcome to our second quarterly Network Stats report covering Q1 of 2026. Along with Drive Stats and Performance Stats, Network Stats pulls back the curtain on real-world infrastructure data, particularly how network-level analytics reflect emerging AI industry trends and usage patterns. 

Get more Network Stats (and the details of the dataset)

If you are curious about what metrics we’re recording and how we classify data in this series, check out the details outlined in our Q3 2025 Network Stats  and Q4 2025 Network Stats report.

One of the roles of the Network Engineering (NetEng) team at Backblaze is to monitor how traffic moves into, out of, and across our platform—not just day-to-day, but over time as customer behavior and industry dynamics evolve. Right now, few forces are reshaping networks faster than AI. 

With the launch of B2 Overdrive in April 2025, we built a direct, high-performance path between our storage layers and neoclouds where processing, inference, and modeling take place. It has given us a front-row seat to the impact of AI and how network behavior is changing with it. This quarter, in addition to our regular data analysis, we’ve added some geographic heatmaps to understand where and how data is moving. 

Join us live for the webinar

Join us live for the Q1 2026 Network Stats webinarMonday, May 4, 2026 at 11:30 a.m. PT / 2:30 p.m. PT. We’ll explore where AI traffic concentrates, how high-magnitude data flows behave, and what early indicators suggest about the future of AI-native infrastructure design.

Can’t make it live, or reading this article after-the-fact? Sign up anyway and catch the recording on demand.

Get Inside Real AI Network Flows

AI: The elephant in the room

AI workflows don’t just need a place to store data, they need to be able to move it quickly, easily, and nearly constantly for short bursts. Large, multi-petabyte datasets are ingested, transformed, exported for training, pulled back for evaluation, and periodically refreshed as models evolve.  

Backblaze plays a key role at both ends of that lifecycle. We serve as a durable storage layer for the initial data ingestion, and as the high-throughput source feeding model training, evaluation, and validation to whatever best neocloud is suitable at the moment. Once that model has been trained, it needs to be stored, served, and periodically retrained, where we serve as the storage medium.

From a network perspective, this represents a meaningful shift from diffuse, internet-style traffic patterns to large, high-bandwidth flows between a smaller set of endpoints typical of AI-centric infrastructure.

Trends and spring renewal

The defining theme of the quarter is “winter freeze” as we observed what looks to be a quiet period of Neocloud and hyperscaler traffic over the winter months with an uptick in March. 

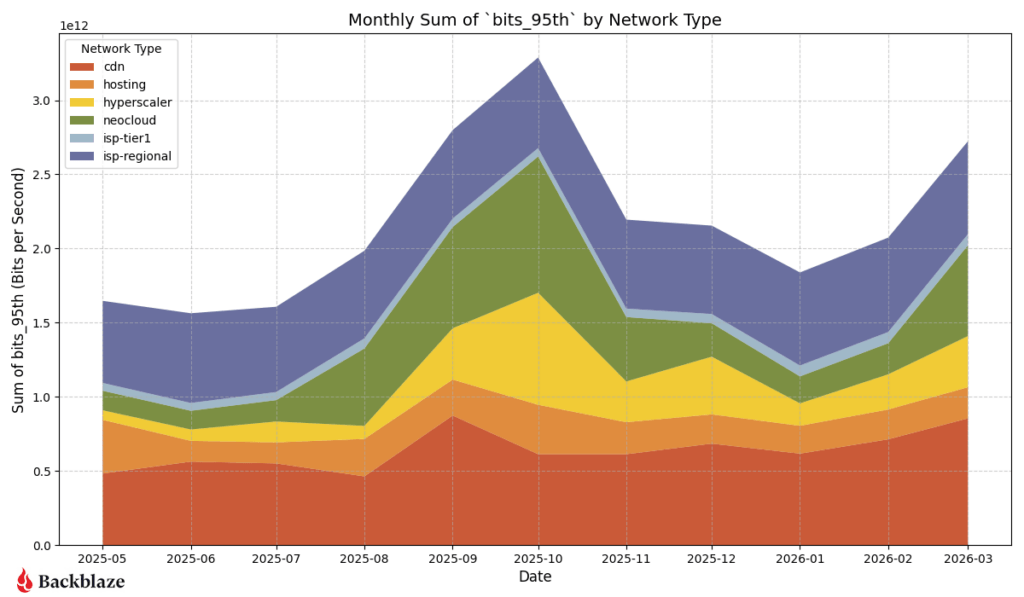
The stacked area graph below shows total traffic by network type over time updated with the most current data. Hosting and internet service provider (ISP) traffic stayed largely within historical norms reflecting steady-state usage patterns. Three slices stand out this quarter:

  • CDN traffic: Increase in CDN traffic over the winter months.
  • Neocloud traffic: After the October 2025 peak, we saw a decline in neocloud traffic heading into January. The winter months were a low volume period with an upward trend observed February into March 2026.
  • Hyperscaler traffic: Hyperscaler traffic also followed the Neocloud pattern of a low period during winter with an upward trend in March 2026.

With more than three quarters of data at our disposal, we can now start to see some trends over time. What do we think is happening? 

This could be an indication of the human element where the business cycle has a lot of downtime in the winter months—all of our code, infrastructure, computing jobs, and new innovations involve people somewhere along the chain and we all (hopefully) tend to take more time off in the winter months.

Another hypothesis is that our numbers only show bits transferred over our network links over time. If a large dataset has been stored with us, there may not need to be an update to the large stored dataset for a number of months as code and models are refined, and then suddenly a large amount of new data makes its way over our network links. Perhaps a combination of both—human and training lifecycle?

We’ll be tracking these metrics and updating in future reports, so this high-level view of network traffic segmented by network type will be interesting to watch.

Chart overview

Now let’s take a deep dive into our data and answer these questions:

Quarter over quarter heatmaps: How and where data moves

To better understand our network activity, we isolated variables like region and types of provider. Let’s look at the following dimensions: 

  1. Total traffic volume: Where did we send and receive the most traffic? 
  2. Magnitude: Where were the data transfers with the most bits per unique IP address?
  3. Uniqueness: What does the number of distinct IP addresses look like? 

Quick terminology refresher

  • Regions
    • US-West: Our largest and longest-running region
    • US-East: Region with the most observed proximity to neocloud infrastructure
    • CA-East: Our newest region in Canada. 
  • Network Types
    • CDN: Networks that use Backblaze as an origin store for content delivery 
    • Hosting: Traditional hosting providers that runs workloads like physical or virtual servers for web, database, or application tasks
    • Hyperscaler: Large, traditional cloud providers
    • ISP Regional: Local or regional ISPs, think of these as the “last mile” paths as these networks are very close to customer equipment and efficient 
    • ISP Tier1: National or international ISPs that carry our traffic long distances
    • Neocloud: AI -focused compute networks

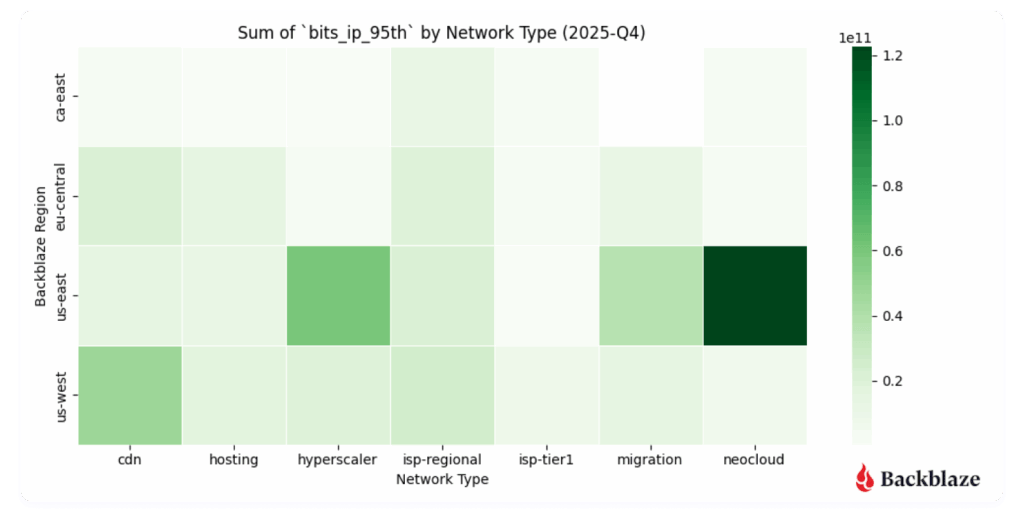
Heatmap #1: Where did we send and receive the most traffic?

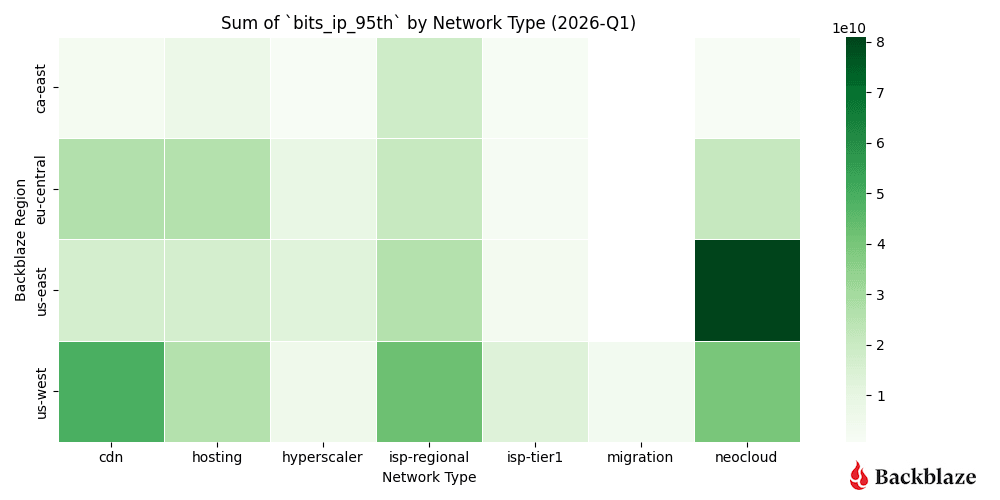
US-West ↔ ISP-Regional traffic continues to be a hotspot on the heatmap, as expected. This region has the largest footprint behind it and connections to internet exchanges (IX). This quarter, with a lull in neocloud and hyperscaler traffic over the winter period, we saw an increase in traffic to our CDN partners. The amount of traffic to CDN networks in the US-West, US-East, and EU-Central regions all increased quarter over quarter.

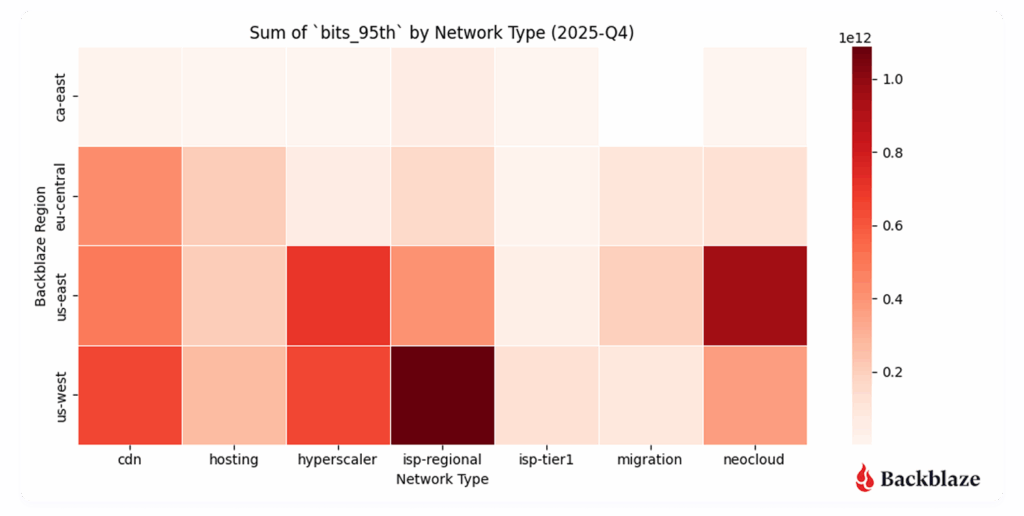
Heatmap #2: Where were the data transfers with the most magnitude (bits per IP address)?

Another metric we record is bits per IP or what we term “magnitude.” This combination of the amount of traffic transferred with how many actors are involved per network is a good proxy to measure how heavy or impactful individual data flows are. In short:

  • High volume, many IPs: Easier to distribute and load-balance across infrastructure. And many source and destination pairs means that we can traffic engineer at the WAN layer, sending some traffic over one provider and some over another.
  • High volume, few IPs: More difficult, but more interesting, from a NetEng perspective. 

Despite the total amount of traffic decreasing over the winter months for neocloud traffic, the magnitude of neocloud transfers still remains high. This speaks to the nature of the traffic pattern—when a GPU/compute cluster is ingesting or producing data, it does so at a high bitrate with just a few number of unique endpoints talking to each other.

As expected, the concentration of our magnitude metric is high for our US-East cluster, with an uptick in concentration in US-West and EU-Central. Where specifically is this new concentration in these regions? Spoiler: We explore neocloud traffic later in the report with geographical data!

As with last quarter, we see a high concentration of neoclouds in US-East, but our new heatmap also shows a rising activity in US-West and EU-Central. We also see more distribution in other use cases. 

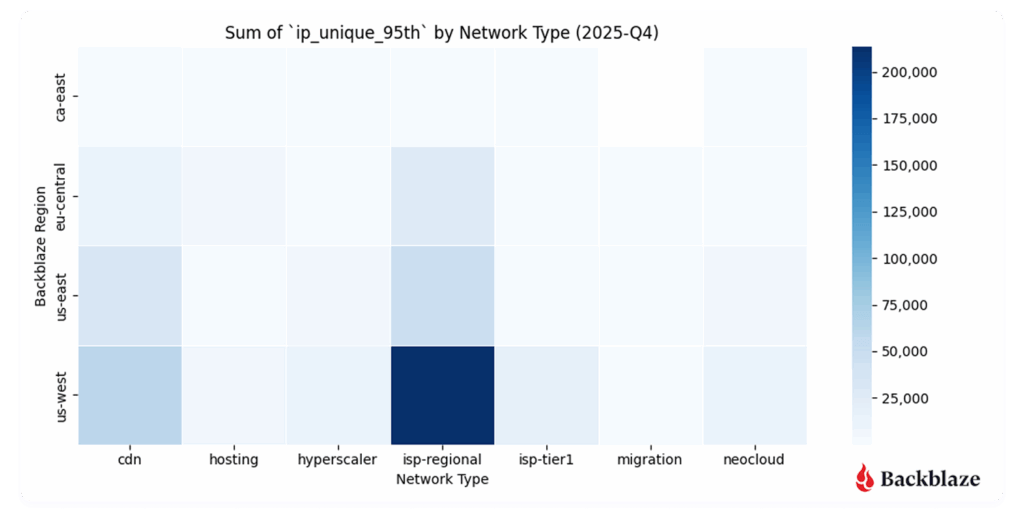
Heatmap #3: How many unique addresses do we interact with?

Uniqueness—measured by the number of distinct IP addresses per network type—adds another dimension to the story. Unsurprisingly, the quarter over quarter heatmap looks almost identical. This is expected with our US-West region being the most mature and serving a large amount of ISP Regional consumers and is a good sanity check on our dataset.

  • US-West shows the highest overall uniqueness, driven by its larger number of data centers and mix of workloads.
  • Neocloud traffic, by contrast, tends to involve fewer, more persistent endpoints, consistent with AI pipelines that rely on stable, long-standing connections between storage and compute. 

This is where we can clearly see those AI networking elephant flows showing up in the data.

Summary: Seasonal change in traffic flows

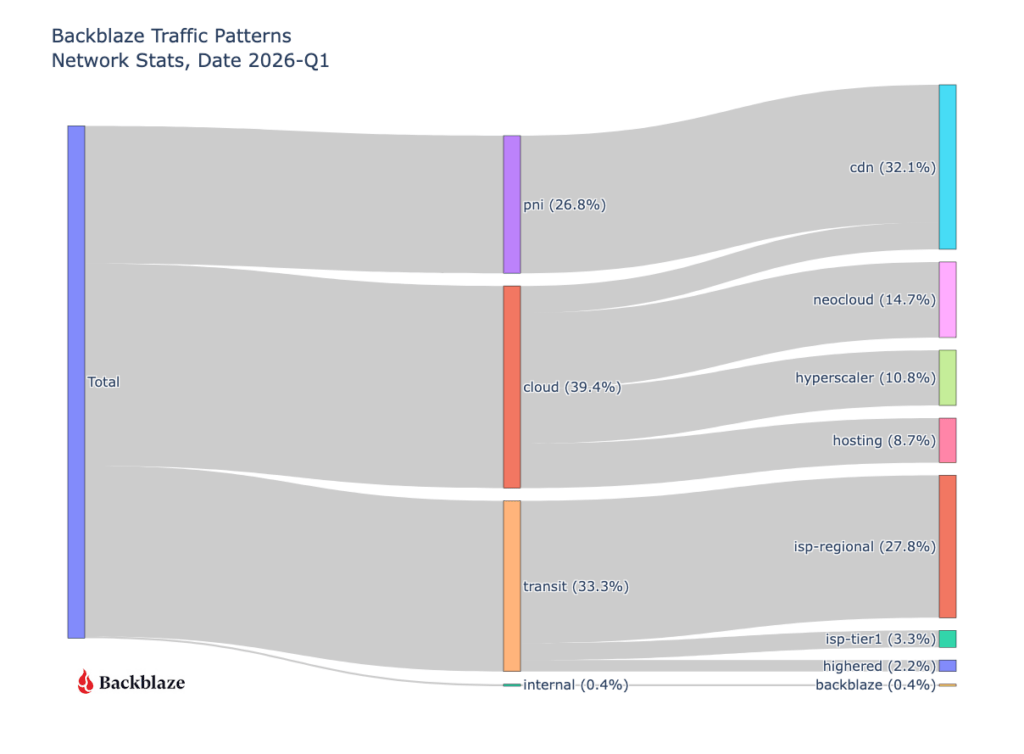
With a lull in bits transferred as noted in our top level graph, we can see what other networks by percentage took over. CDN traffic increased from around 20% to 32% of our total traffic, localized ISP regional traffic also increased 21.5% to 27.8%. Neocloud and hyperscaler traffic reduced from 36.4% in Q4 2025 to 25.5% in Q1 2026. 

Quarter over quarter data

We’re tracking our usual metrics here, and we gave you both this quarter and last quarter’s charts so you can easily spot potential trends.  

First let’s take a look at where all our traffic goes from a global perspective with an updated view of last quarter.

Next, let’s take a look at the geography of our network traffic. As we’ve already seen in previous heatmaps, data gravity is concentrating traffic into specific locations.

Where in the world is the neocloud?

New for March 2026, we’ve added geographic information to our dataset, allowing us to take a look at the concentration of traffic based on network types. We’re taking a look into the following locational slices:

  1. Countries
  2. Countries excluding the United States
  3. U.S. states

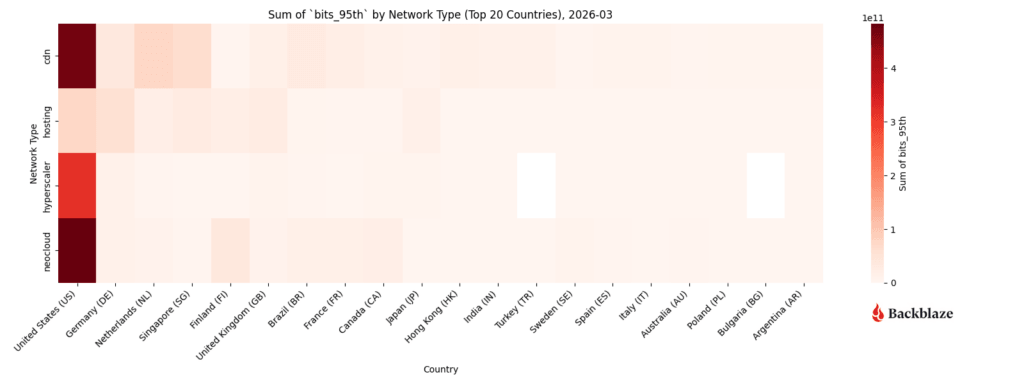
Heatmap #1: What countries show the highest concentration of traffic by network type?

Neocloud, hyperscaler, and CDN traffic in our dataset all show high concentrations in the United States. Is this due to our US-West and US-East regions being the largest of our deployments or is it related to how certain traffic types are present in the emerging AI market? A quick search shows that the U.S. contains around 40-45% of all data centers globally, so it’s likely the sheer deployment size and scope of US sites aligns with what we’re seeing at the network level.

That said, excluding outliers can show us additional geographic trends, which leads to our next heatmap.

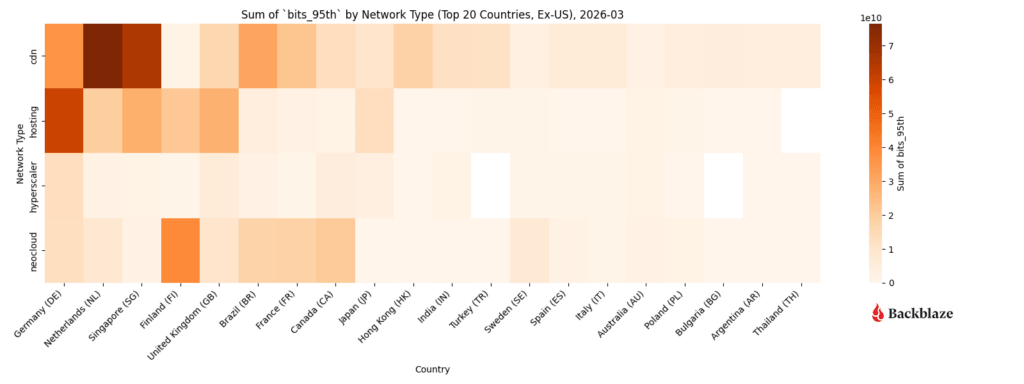
Heatmap #2: If we exclude the U.S., what countries show the highest concentration of traffic by network type?

Since the United States numbers highly skew the heatmap concentration, below is a heatmap without the US to give us better fidelity on ex-US datapoints. Interesting to note that we deliver a large amount of traffic to CDN entities in the Netherlands. This is due in part to our connectivity to AMS-IX (Amsterdam Internet Exchange). 

The network posture of Europe differs from the United States to where local IX networks are preferred over larger Tier1 ISP networks for transit (politically, cost, and preference wise). Second up is Singapore for CDN content and hosting activity in Germany. The next standout is a concentration of neocloud related activity in Finland, Brazil, France, and Canada.

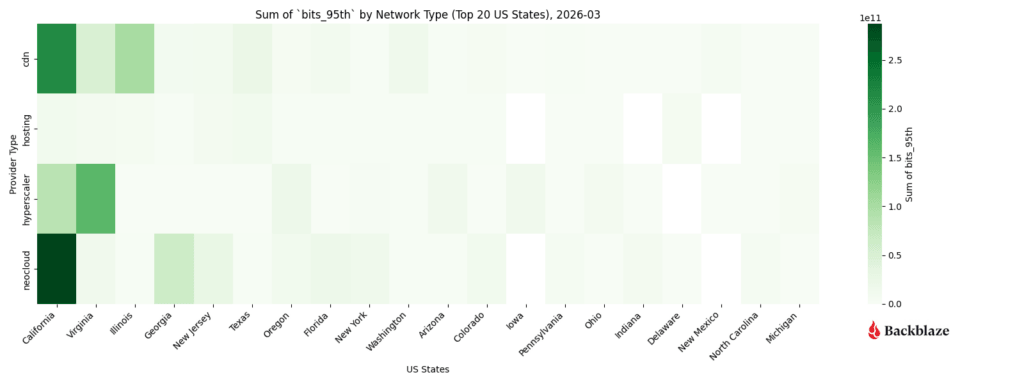
Heatmap #3: What U.S. States show the highest concentration of traffic by network type?

If we dive into just the U.S. States, we can see the heavily weighted concentration of neocloud traffic to and from California. Hyperscaler activity matching up with our expectations as California and Virginia (specifically the Ashburn and Reston corridor) have a high concentration of partner networks. CDN traffic for us concentrates more for Backblaze specifically since the US-West region is our largest cluster footprint and longest running sites, so naturally the data being served out of these sites is more long-lived content lifecycle wise.

These insights into data geography help us understand, plan, and modify our growth trajectory. I say “help,” because we’re also discovering that neocloud and hyperscaler activity is very bursty and has a high magnitude of traffic flow below. From a planning perspective, understanding whether those bursts translate to a higher baseline for increased demand—and how to support bursts when they happen—is a different conversation than the predictable network trends of years past. 

Neocloud and hyperscaler traffic vs predictive patterns

This quarter we’re sharing a deeper dive into the metrics associated with neocloud and hyperscalers over time. These two traffic types are driving innovation at Backblaze and are interesting to share to the larger industry. While CDN, hosting, and ISP regional traffic patterns are easy for us to model and account for as we manage our network infrastructure, neocloud and hyperscalers growth profiling are a challenge! As we said above, they are bursty and have a high magnitude (bits per associated IP address).

And, in the spirit of that conversation, we have several new views to share:

  • Neocloud and hyperscaler magnitude (bits per IP address) over time
  • Heatmaps over time
    • Neocloud
    • Hyperscaler
    • CDN
    • Hosting
    • ISP regional

Chart #1: What’s the magnitude of neocloud and hyperscaler traffic over time?

Matching our earlier charts, we saw a burst of activity from August to December of last year with a resurgence of high magnitude neocloud traffic in March of 2026.

Heatmap #1 and #2: How dynamic are neocloud and hyperscaler traffic patterns?

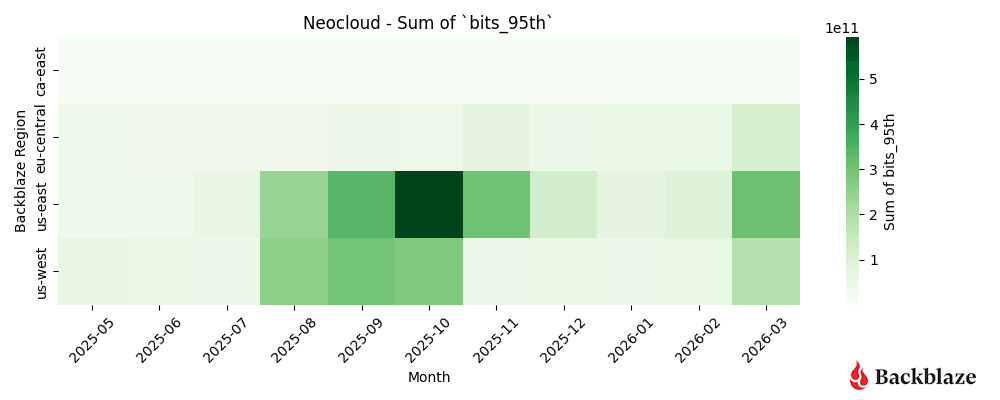
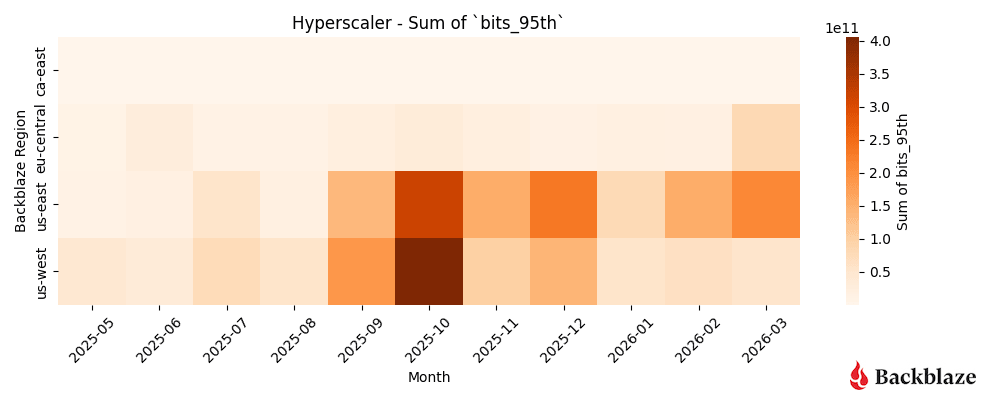
Neocloud and hyperscaler traffic patterns are the most impactful to our operations due to the magnitude of their data flows. Below is a more detailed look at these concentrations over time, with a burst of activity from August to November for Neoclouds, a quiet period over the winter months, and a pickup again in March. 

As expected our US-East region remains a hotspot of Neocloud related activity. One standout from this analysis is that the Neocloud activity in March is more spread out over our US-West, US-East, and EU-Central regions. It will be interesting to see if this spread grows or contracts over time.

Over the winter months, there was a noticeable decrease in activity for hyperscale related traffic, most notable in January, but when compared to neocloud traffic, the month-over-month traffic patterns remained strongly visible in our US-East region.

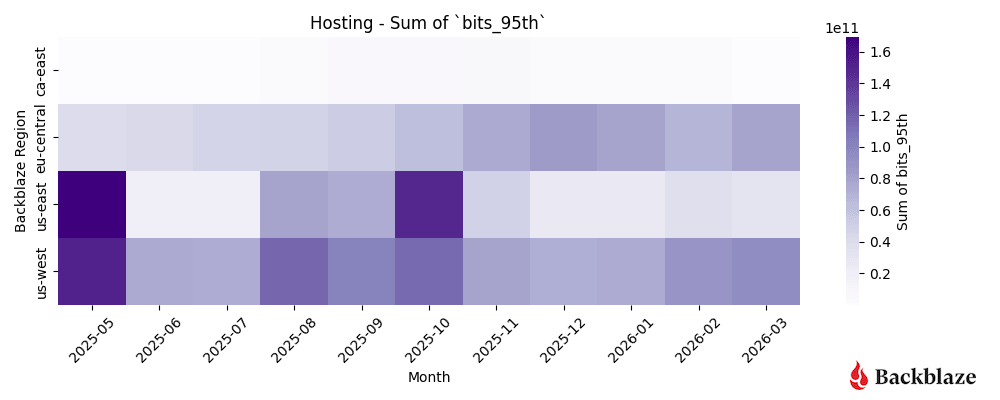
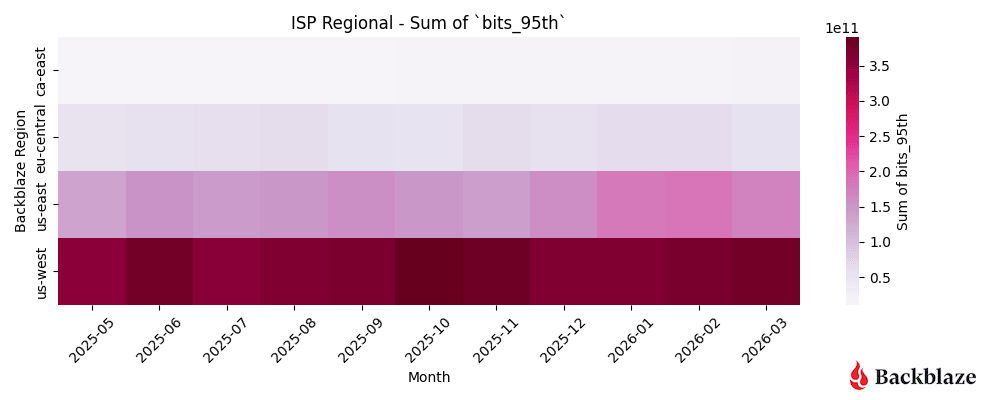
Heatmap #3, #4, and #5: How dynamic are CDN, hosting, and ISP regional traffic patterns?

We’re grouping CDN, hosting, and ISP regional types together because they represent a “steady-state” for us as network operators. These patterns are predictable, spread out over time, and generally do not change month-to-month. We do see visible bursts of traffic, like with a heavy blue tile for CDN in September and a few areas of hosting related traffic in May and October of 2025, but overall these are less impactful to our operations because the magnitude (bits per unique IP address) is lower—many sources are talking to many destinations, which as operators is easy to load balance.

The most striking example of this predictability is, unsurprisingly, ISP regional traffic. This represents your more consumer driven workflows and use cases.

Neocloud business cycle and geography

We can draw a conclusion from all these charts: neocloud and hyperscaler are both different traffic patterns and far more dynamic than CDN, hosting, and ISP regional traffic. For our Network Engineering group, this means we have two different stylistic approaches towards managing our network. 

First, when planning for the neocloud and hyperscaler traffic, our solutions entail adding large amounts of additional bandwidth in increments of 100G and often 400G ports to handle burst rates, ensuring that our inter-switch links inside our datacenter can also handle bursts of traffic, and reaching out to select partners to establish private network-to-network interface (PNI) connections where appropriate for zero-settlement transit. 

Our steady state growth patterns stem from CDN, hosting, and ISP regional traffic with easy to model growth curves. Looking over monthly numbers indicates a clear pattern for us, and that’s easy to plan for.

The last factor that we’re placing more emphasis on is the geographical location of our network interconnections. We’re seeing a high concentration of demand located in the United States, specifically in regions like California, Virginia, Illinois, and Georgia.

With more datapoints, we can clearly see the magnitude of the neocloud and hyperscaler transfers when compared to other network types. As above, it’s a bit early to claim concrete quarter over quarter patterns, but we’ll keep monitoring and updating the dataset. 

What’s next?

Anything specific you want to see? Let us know in the comments or reach out to the Network Stats team. Or, keep up-to-date with the latest technical content with our Developer Newsletter. 

The post Network Stats for Q1 2026: Neocloud Traffic Trends appeared first on Backblaze Blog | Cloud Storage & Cloud Backup

What Anthropic’s Mythos Means for the Future of Cybersecurity

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2026/04/what-anthropics-mythos-means-for-the-future-of-cybersecurity.html

Two weeks ago, Anthropic announced that its new model, Claude Mythos Preview, can autonomously find and weaponize software vulnerabilities, turning them into working exploits without expert guidance. These were vulnerabilities in key software like operating systems and internet infrastructure that thousands of software developers working on those systems failed to find. This capability will have major security implications, compromising the devices and services we use every day. As a result, Anthropic is not releasing the model to the general public, but instead to a limited number of companies.

The news rocked the internet security community. There were few details in Anthropic’s announcement, angering many observers. Some speculate that Anthropic doesn’t have the GPUs to run the thing, and that cybersecurity was the excuse to limit its release. Others argue Anthropic is holding to its AI safety mission. There’s hype and counterhype, reality and marketing. It’s a lot to sort out, even if you’re an expert.

We see Mythos as a real but incremental step, one in a long line of incremental steps. But even incremental steps can be important when we look at the big picture.

How AI Is Changing Cybersecurity

We’ve written about shifting baseline syndrome, a phenomenon that leads people—the public and experts alike—to discount massive long-term changes that are hidden in incremental steps. It has happened with online privacy, and it’s happening with AI. Even if the vulnerabilities found by Mythos could have been found using AI models from last month or last year, they couldn’t have been found by AI models from five years ago.

The Mythos announcement reminds us that AI has come a long way in just a few years: The baseline really has shifted. Finding vulnerabilities in source code is the type of task that today’s large language models excel at. Regardless of whether it happened last year or will happen next year, it’s been clear for a while this kind of capability was coming soon. The question is how we adapt to it.

We don’t believe that an AI that can hack autonomously will create permanent asymmetry between offense and defense; it’s likely to be more nuanced than that. Some vulnerabilities can be found, verified, and patched automatically. Some vulnerabilities will be hard to find but easy to verify and patch—consider generic cloud-hosted web applications built on standard software stacks, where updates can be deployed quickly. Still others will be easy to find (even without powerful AI) and relatively easy to verify, but harder or impossible to patch, such as IoT appliances and industrial equipment that are rarely updated or can’t be easily modified.

Then there are systems whose vulnerabilities will be easy to find in code but difficult to verify in practice. For example, complex distributed systems and cloud platforms can be composed of thousands of interacting services running in parallel, making it difficult to distinguish real vulnerabilities from false positives and to reliably reproduce them.

So we must separate the patchable from the unpatchable, and the easy to verify from the hard to verify. This taxonomy also provides us guidance for how to protect such systems in an era of powerful AI vulnerability-finding tools.

Unpatchable or hard to verify systems should be protected by wrapping them in more restrictive, tightly controlled layers. You want your fridge or thermostat or industrial control system behind a restrictive and constantly updated firewall, not freely talking to the internet.

Distributed systems that are fundamentally interconnected should be traceable and should follow the principle of least privilege, where each component has only the access it needs. These are bog-standard security ideas that we might have been tempted to throw out in the era of AI, but they’re still as relevant as ever.

Rethinking Software Security Practices

This also raises the salience of best practices in software engineering. Automated, thorough, and continuous testing was always important. Now we can take this practice a step further and use defensive AI agents to test exploits against a real stack, over and over, until the false positives have been weeded out and the real vulnerabilities and fixes are confirmed. This kind of VulnOps is likely to become a standard part of the development process.

Documentation becomes more valuable, as it can guide an AI agent on a bug-finding mission just as it does developers. And following standard practices and using standard tools and libraries allows AI and engineers alike to recognize patterns more effectively, even in a world of individual and ephemeral instant software—code that can be generated and deployed on demand.

Will this favor offense or defense? The defense eventually, probably, especially in systems that are easy to patch and verify. Fortunately, that includes our phones, web browsers, and major internet services. But today’s cars, electrical transformers, fridges, and lampposts are connected to the internet. Legacy banking and airline systems are networked.

Not all of those are going to get patched as fast as needed, and we may see a few years of constant hacks until we arrive at a new normal: where verification is paramount and software is patched continuously.

This essay was written with Barath Raghavan, and originally appeared in IEEE Spectrum.

НСИ и броят родени деца на България

Post Syndicated from Боян Юруков original https://yurukov.net/blog/2026/nsi-rajdania/

Пиша за демографията и статистиката свързана с нея отдавна и в началото на всяка година критикувам журналисти и политици за сензационни твърдения хващайки се за първото налично число без да разбират какво всъщност значи. В следващата си статия ще опиша подробно петте числа, които имаме за ражданията в България. Сега искам да се спра по-подробно на едно от тях.

През годините винаги съм настоявал да се чака края на април, когато излизат данните на НСИ. Причината е, че за останалите нямаме методология или някакво обяснение какво показват. Това, което ще опиша тук, не променя това ми становище, а внася яснота какво виждаме.

НСИ и европейският регламент за статистиката

Заради значителното разминаване – с три до шест хиляди деца – между данните на НСИ и първо на регистъра на ражданията, а в последно време с тези на НЦОЗА и НЗИС, през годините многократно съм търсил информация и питал за детайлите около процеса и източника на данните. В публикуваната методология на НСИ е описано, че данните се регистрират чрез формуляр „Съобщение за раждане“ в ЕСГРАОН. Такъв формуляр се издава само в България от болниците регистриращи ражданията. Т.е. ражданията в България.

За съжаление, това не е цялата история и го научих едва наскоро след като зададох тези въпроси отново. Има добри причини за това и е важно да ги разберем.

От обяснението им става ясно, че имат задължение да съблюдават Регламент 2025/2458 на ЕП и Съвета. Там изискването е цялата статистика се води спрямо мястото на обичайното пребиваване на лицата. Това е логично, но създава трудности на практика. Трябва да знаем не само приблизително колко души пребивават предимно в България, а кои хора конкретно, в случай че им се роди дете. Както описах в статията ми за данните на диаспората ни в Германия, това е трудна задача дори за германската статистическа служба, която разчита на изключително стриктна адресна регистрация, но пак вижда разминаване между различните оценки за броя българи с до 19.2% или 70 хиляди души, а през 2022-ра направиха корекция надолу в преброяването с 10.18%. Аналогично, в България при преброяването имаше ревизия на населението с 9.47% надолу.

Какво общо има това с ражданията? Освен съобщенията за ражданията идващи от болниците, в ЕСГРАОН се вписват и деца родени в извън България на база актове за раждане от чужбина. Това означава, че поне някои от ражданията регистрирани от НСИ са се случили в чужбина. Това се прави за онези жени – или мъже когато майката не е българка – които не само имат настоящ адрес в страната, но и според данните събрани от МВР, НАП, НОИ, МВР и други източници няма информация, че са извън страната. Доколкото често при местене в друга държава не сменяме настоящия си адрес, останалите източници помагат да се допълнят тези данни.

Все пак, има немалко българи, за които няма данни, че са постоянно в чужбина. Част от тях имат деца, а част от тези ги регистрират в България, за да имат документи. Това създава няколко проблема.

Проблемът с „обичайно пребиваване“

Първо, НСИ са длъжни по европейски регламент да броят раждането към родната статистика независимо къде се е случило, тъй като няма надеждни сведения за друго постоянно пребиваване. Възможно е, например, детето да е родено в клиника по репродукция другаде или по време на пътуване. НСИ няма право да предполага според европейския регламент. Липсва и механизъм за обмен на информация между държавите в ЕС за регистрацията и пребиваването на граждани на други страни. Същите правила важат за всички статистически агенции в ЕС.

Вторият проблем е, че НСИ взима от ЕСГРАОН данните за децата родени в чужбина между февруари и април в календарната година. Както описах в последната ми статия с данните между 1990 и 2018-та, доста от тях се регистрират месеци и дори години по-късно. При това поради редица фактори дялът на регистрираните деца родени в чужбина не е постоянен във времето. Влияе се от отпуски, празници, проблеми с пътуването и прочие.

Към февруари 2025-та, например, само 8 хиляди деца родени в чужбина са били регистрирани в ЕСГРАОН с година на раждане 2024-та. Към същия момент обаче 15 хиляди са въведени на база акт за раждане в чужбина и година на раждане 2023-та. Скоро ще публикувам последните данни до този момент и оценка на тенденцията.

Всичко това значи, че НСИ отчита предимно децата, които са бързо регистрирани в България от родителите, за които няма данни, че са в чужбина въпреки, че не са променили настоящия си адрес. Това всъщност подобрява оценката, тъй като ако живеят обичайно в България, много по-вероятно е да регистрират детето си скоро след раждането. В такъв случай по-рестриктивен подход би помогнал още – да се гледа не само година на раждане, но и дали ЕГН-то е издадено до 3 месеца след чуждестранния акт.

Третият проблем е, че по този начин се отчитат само живородените, но не е мъртвородените. Няма механизъм за съобщаване на последните, а и няма акт за състояние или някакъв смисъл за родителите в такъв труден момент да взаимодействат с българската администрация. Това е очаквано и разбираемо. Ефектът обаче е, че така растат живородените и ражданията като цяло докато съотношението на мъртвородените стои нисък. Така виждаме известно изкривяване в статистиката на последните.

Родените на територията на България и още разминавания

Поисках от НСИ данните им за броят раждания в България и тези в чужбина, които са длъжни да включат по регламента. За 2024-та казаха, че имат информация за 49714 родени на територията на България и 3714 – в чужбина по критериите описани горе. През 2023-та – 51127 в България и 6070 – в чужбина. За последните 10 години дялът на тези в чужбина варира широко между 6 и 10% от ражданията в официалната статистика. Като дял от всички деца родени в чужбина и в последствие регистрирани в България, тези взети от НСИ са средно около 20-25%. За това може да има много фактори, както описах горе.

Тези числа не потвърждават данните на НЦОЗА и НЗИС и не оправдават вариациите в тях. Отклонението помежду им варира в граници от 1500 деца, което пак е много. През 2020 и 2022-ра НЦОЗА на база данните на НЗОК отчита съответно 225 и 478 живородени по-малко от НСИ, които грубо казано гледат издадени ЕГН-та. През 2018 и 2023-та пък отчита с 1082 и 1332 повече. Разликата с НЗИС за 2023 и 2024-та е съответно 263 и 603.

Тези отклонения достигащи 2.5% са достатъчни, за да продължим да се съмняваме в данните на НЗОК гледаща само фактурите и НЗИС разчитаща на съвеста на болниците да въвеждат информация своевременно. Непостоянството през времето неизменно ще води до грешни изводи. Поставят също сериозни въпроси относно качеството на здравната ни статистика отгоре на вече известните проблеми с данните по причини за смъртност, особено тези свързани с бременността, данните за вътрешноболничните инфекции и диагностиката.

Доколкото точното число на броя раждания може да не е от значение за някои, всъщност е важен компонент от демографията. Причината защо тази нова информация, че се включват някои раждания от чужбина, да не променя позицията ми спрямо данните на НСИ е, че няма как по друг начин да изчислим коефициенти като раждаемост и фертилност.

Защо е неизбежно и не променя ключовите демографски параметри?

Раждаемостта често се бърка като термин с броя раждания. В действителност показва броя живородени деца на всеки 1000 души население. Заедно с фертилността – или по-точно коефициента на плодовитост – са ключови показатели за посоката, в която се движи населението на станата и колко бързо. Ако фертилността е под 2.1, както е случая с цяла Европа и почти целия свят, няма заместване на населението. България е под това ниво, но все пак едно от най-високите в Европа – над 1.7.

Тези коефициенти се изчисляват на база население за първия и жени по възрастови групи за втория, за които се знае, че пребивават в България. Отново – следва се стриктно европейския регламент. Докато може да знаем, че едно раждане на жена на 28 години се е случило извън страната, то далеч не може да знаем дали още 100 жени на 28 години не са в действителност в България. Ако изключим това раждане от статистиката на НСИ въпреки, че нямаме никакви данни, че майката живее постоянно в чужбина, то тогава изкуствено ще влошим статистиката за раждаемостта и фертилността. С други думи – с настоящия си подход НСИ не само отговарят на статистическите стандарти, но и съпоставят сравними неща – брой раждания от родители, за които нямаме данни, че са в чужбина спрямо цялата оценка за населението, за което нямаме данни, че е в чужбина.

Така получаваме коефициент на плодовитост 1.72 за 2024-та и 1.81 през 2023-та. Преди две години обясних защо са толкова високи числата и защо имаше привиден скок преди това. Причината беше, че с преброяването НСИ обнови базата си данни и оценката за населението надолу. От там доста повече хора бяха маркирани като живеещи извън страната, отколкото деца регистрирани на база чуждестранен акт за раждане. Това нямаше да е възможно, ако не се използваше тази методология и не се правеше ревизия на населението.

Разбираема е критиката, че тези няколко хиляди бебета може би никога не биха се върнали в България със семействата си и следователно не бива да ги броим така. Навярно е така, но от друга страна поне в момента се оказва, че доста се връщат. По данни на имиграционните в Германия, само от там за 2025 с 10 хиляди български граждани повече са се изнесли, отколкото са се нанесли. Данните на двете статистически служби до сега сочат, че мнозинството са се насочили към България. По-важното е, че в този метод на статистика има коректив – при преброяването се прави ревизия на старите данни и предположения, които не са могли да бъдат проверени към настоящия момент.

Утре ще излязат демографските данни за 2025-та на НСИ и ще обясня по-подробно как се различават методологиите на различните източници.

Предишни статии за ражданията в България

Това са част от текстовете по темата, които съм писал до сега:

MDR Selection is a Partnership Decision

Post Syndicated from Alan Simpson original https://www.rapid7.com/blog/post/dr-mdr-selection-partnership-decision

Managed Detection and Response (MDR) is a cybersecurity service that combines human expertise and technology to detect, investigate, and respond to threats 24/7.

I write this as a Field CISO at Rapid7, but also as someone who has had to live with the operational reality of MDR on the customer side. I have seen what happens when a service is a black box, when technology and service drift apart, and when cost, retention, and accountability are misaligned. That experience shapes the view in this piece: MDR selection is not just about buying monitoring in isolation, but about choosing a partner that can help your team reduce risk and improve the way security operates over time.

When organisations evaluate MDR, they often start in the wrong place. The discussion begins with integration counts, dashboards, pricing tables, and increasingly bold claims about AI or dramatic reductions in alert volume. Those things all matter to a degree, but they are not the centre of the decision. The real question is whether you are choosing a provider that will work as a genuine partner, help you reduce risk over time, and strengthen the way your team operates when the environment becomes noisy, complex, or difficult to manage.

That matters because MDR is not a service that sits neatly off to one side of the security function. It becomes part of the operating model. It influences how visibility is created, how incidents are handled, how priorities are surfaced, and how much confidence a leadership team has in the people and processes around it. For that reason, I do not think MDR selection is primarily a tooling exercise. It is a partnership decision.

What poor MDR looks like in practice

My own view on this has been shaped by more than one experience. In one case, our MSSP was part of a defence company that was later carved out into a separate business. The service was built around a legacy SIEM. They had plenty of interest elsewhere in automation and future-state capability, but the fundamentals were being missed. We could talk about what we wanted to automate, but not with enough confidence about the quality of the underlying visibility, the operational process around it, or how the service was supposed to mature over time.

In another case, the issue was an MSSP overlay wrapped around a well-known, high-cost log indexer. On paper, that should have been a strong foundation. In practice, the management layer around it was poor. There was a lack of expertise, no credible roadmap, and very little meaningful tuning. As the MSSP was also reselling the ingest, there was no obvious incentive to optimize data use in the customer’s favour. Ingest was capped because of cost, retention was limited to 90 days, and we were left with the uncomfortable combination of high spend, constrained visibility, and a service that did not appear to be improving in any meaningful way.

Those experiences shaped how I think about MDR because they exposed the same underlying problem. The technology was not absent, but the service model around it was weak. When the gap between the platform and the service becomes too wide, the customer ends up paying for capability in theory while carrying the operational risk in practice.

Why the gap between platform and service matters

This is where many MDR relationships start to fail. Even when the tooling is capable, the provider still has to connect platform, people, process, and commercial model into one coherent service. If that does not happen, the customer ends up living with support issues, awkward hand-offs, misaligned contracts, unclear accountability, and a constant sense that there are too many moving parts and not enough ownership.

That is why I would start any MDR evaluation by looking at how the relationship is meant to work in practice. 

  • Does the provider genuinely own the experience end to end, or are they effectively brokering one element through another?

  • Can they show how the programme will improve over the first year, not just how onboarding works in the first month?

  • Do they understand the rest of your security ecosystem and how to operate within it, or do they assume every answer involves expanding their footprint?

Strong providers think holistically. They understand that the customer already has an environment to manage, existing tools to work with, and internal teams who need clarity rather than additional friction. They think in terms of operating model, monitoring, response, and continuous improvement over time, rather than treating the service as a thin wrapper around a platform. That is usually where the difference between coverage and real partnership becomes obvious.

Proactive defense starts with the fundamentals

True partnership is defined by its ability to deliver proactive defense and continuous improvement. By this, I do not just mean threat hunting or faster triage. I mean exposure reduction in the broader sense. It is understanding attack paths, using intelligence well, tuning detections properly, improving visibility where it matters, and building a service rhythm that reduces the conditions attackers rely on.

That sounds obvious, but it is surprisingly easy for organisations to be distracted from those fundamentals. Low entry prices often mask a fundamentally constrained operating model, shifting risk and cost back to the customer. 

Sweeping promises about single digit alert volumes should be treated carefully, especially before a provider has properly understood the environment. The same is true of broad agentic AI claims. Automation can absolutely help, but it does not replace accountability, operational judgement, or the need for a provider to show how the service will improve over time.

For me, that last point is one of the clearest tests of whether the relationship is working. An MDR service should not be something you set and forget. A mature partnership should look better in month twelve than it did in month one. Visibility should improve. Tuning should improve. The roadmap should improve. Confidence in escalation and response should improve. If none of that is happening, it becomes very difficult to describe the relationship as a real partnership. At that point, you may simply have outsourced a queue.

When displacement becomes the right answer

That is also how I think about displacement. An incumbent should not be displaced simply because another provider has a sharper demo or a more fashionable story. Displacement makes sense when the existing model has stopped improving, when the service feels static or opaque, when the team lacks the expertise to tune and evolve it properly, or when the commercial structure and delivery model are working against the customer rather than with them.

If the relationship is held together by workarounds, if there is no meaningful roadmap, or if the customer is left carrying too much of the integration and governance burden themselves, the problem is usually structural rather than temporary. In that situation, the question is no longer whether the service can be tweaked around the edges. The question is whether the model is fit for purpose at all.

Consolidation is only useful if it improves the model

That does not automatically mean consolidation is the answer. Consolidation can be valuable, but only when it improves the operating model rather than simply reducing the number of logos in the environment. In some cases, the right answer will be to build a broader relationship with a provider that has earned trust and shown it can deliver more. In others, the right answer will be better integration and a clearer division of responsibilities.

What matters is whether the provider helps create a more coherent, scalable, and accountable way of operating. If consolidation leads to better hand-offs, stronger accountability, and a simpler way of reducing risk, it can be very valuable. If it does not, then consolidation is not the point. A better operating model is.

This broader view is also consistent with established security guidance. NIST CSF 2.0 frames cybersecurity as a risk management discipline across governance, protection, detection, response, and recovery [1]. NIST’s latest incident response guidance reinforces that response should be integrated into wider risk management and improved over time [2]. The NCSC makes a similar point in its guidance on building a SOC and on security monitoring, where tools, skills, and operating model all need to work together [3]. CISA’s exposure reduction guidance points in the same direction by focusing on reducing the conditions attackers rely on before incidents escalate [4].

Questions worth asking any MDR provider

There are a few practical questions I would encourage any CISO, Security Director, or Security Operations Manager to ask, whether they are reviewing an incumbent or evaluating a new provider:

  • How will the service improve over the first year and beyond?

  • Where do the hand-offs happen between your platform, your analysts, and my team?

  • How do you work with the security and IT tools we already rely on?

  • How predictable is the commercial model as coverage expands?

  • What are you doing to reduce risk before the next incident, not just respond after it?

  • If your commercial model benefits from more ingest, what incentive do you have to tune it down?

Those questions reveal far more than a polished demo ever will.

Ultimately, the organisations that get the most value from MDR tend to be the ones that treat it as part of a wider security partnership rather than a neatly outsourced function. They expect transparency, progress, and a provider that understands both the environment they have today and the operating model they are trying to build over time. That is the standard worth holding. If the provider is not improving the programme over time, you do not have a real partnership. And if consolidation does not lead to a better operating model, it is probably not worth doing in the first place.

Learn more about Rapid7’s approach to preemptive MDR.

⠀

Alan Simpson is Field CISO for the UK and Ireland at Rapid7, advising CISOs and senior leaders on cyber risk, resilience, and security strategy that supports business outcomes. Before joining Rapid7, he served as Global Security Operations Manager and Acting CISO at Keyloop, where he led security operations and wider information security initiatives. He has also held senior security leadership roles at Allianz and LV=, with experience across security operations, incident response, architecture, awareness, supplier assurance, and security testing.

⠀

[1] https://nvlpubs.nist.gov/nistpubs/CSWP/NIST.CSWP.29.pdf

[2] https://nvlpubs.nist.gov/nistpubs/SpecialPublications/NIST.SP.800-61r3.pdf

[3] https://www.ncsc.gov.uk/collection/building-a-security-operations-centre

[4] https://www.cisa.gov/resources-tools/resources/exposure-reduction

BIG AI Cluster Little Power the 8x NVIDIA GB10 Cluster

Post Syndicated from Patrick Kennedy original https://www.servethehome.com/big-cluster-little-power-the-8x-nvidia-gb10-cluster-marvell-cisco-ubiquiti-qnap-arm/

We built a big AI cluster that used relatively little power. The 8x NVIDIA GB10 cluster shows what scaling this platform can do

The post BIG AI Cluster Little Power the 8x NVIDIA GB10 Cluster appeared first on ServeTheHome.

pip 26.1 released

Post Syndicated from jzb original https://lwn.net/Articles/1070010/

Version 26.1 of
the pip package installer for Python has been released. Richard Si
has published a blog
post
that looks at some of the highlights of 26.1 including
dependency cooldowns, experimental support for pylock (pylock.toml)
files, and resolver
improvements
that will move pip closer to the goal of removing its
legacy resolver. The release also includes several security fixes and
drops support for Python 3.9.

The collective thoughts of the interwebz