Post Syndicated from The History Guy: History Deserves to Be Remembered original https://www.youtube.com/watch?v=F9ngDi1QDiQ
Кабинетът „Желязков“. Консервативният удобен брак
Post Syndicated from Емилия Милчева original https://www.toest.bg/kabinetut-zhelyazkov-konservativniyat-udoben-brak/

Разни караконджули наплашиха хората, че ако няма редовно правителство, българите ще ги сполетят какви ли не злини. Гражданите се отвратиха от политиците, политиците се умориха и изхабиха от поредицата избори и ето че кабинетът е факт. След такова „бабуване“ обществото изглежда готово да преглътне почти всичко, което политиците му сервират – дори най-противоречивите съюзи.
Погледнато отвън, в България вече управлява коалиция с проруска партия в редиците си. С такова заглавие излезе The Financial Times предвид участието на БСП в управляващото мнозинство, формирано от ГЕРБ–СДС. В този съюз влизат още националпопулистите от „Има такъв народ“ (ИТН) и формалните либерали от ДПС – Демокрация за права и свободи (ДПС–ДПС). То предостави своите 19 гласа, за да гарантира с мнозинство от 126 народни представители избирането на кабинета с премиер Росен Желязков (ГЕРБ–СДС).
Вярва ли някой, че такива обиграни и особено прагматични политици, каквито са несъмнено в ДПС, ще подкрепят управляващо мнозинство с решаващи гласове, без да поискат нищо в замяна? Историята говори друго, а последните събития са показателни.
През юли 2023 г. ДПС, тогава още оглавявано от олигарха Делян Пеевски, санкциониран по „Магнитски“, стана партньор в коалицията между ГЕРБ–СДС и ПП–ДБ, по-известна като не-коалиция и сглобка. Макар да не бе обявено публично, беше известно, че срещу участие в мнозинство за конституционни промени на ДПС е гарантирано запазване на влиянието в регулаторите. Когато се разбра, че им отказват, сглобката се разпадна при ротацията след едва шест месеца управление. А отменените от Конституционния съд текстове от основния закон не само обезсмислиха съглашението, но и нанесоха трудно поправими репутационни щети на ПП–ДБ.
Единственият приоритет със срок
Обновяването на най-значимите органи е сред първите приоритети на новото мнозинство, както се разбира от споразумението за управление. До 30 дни от подписването му, тоест до средата на февруари, трябва да е готова хронограмата за избор на контролни и регулаторни органи.
Всички органи с изтекъл мандат следва да бъдат попълнени в рамките на 1 година от подписването на настоящото споразумение.
Първите са Висшият съдебен съвет и неговият Инспекторат, омбудсманът, Антикорупционната комисия, Комисията за конфискация и Сметната палата. На фона на общите фрази и клишета, с които е пълно споразумението, като например „извеждане на качеството на живот на хората като първостепенен приоритет с фокус върху здравеопазването, образованието и развитието на пазара на труда“, тази конкретика е забележителна. И не само. В цялото споразумение от 11 страници всъщност има вписани само два срока – законодателна програма до месец, хронограма и избор на членове на регулатори и в съдебната власт – в рамките на година.
Но най-важните членове се избират с най-голямо мнозинство – от 160 депутати, така реши 50-тият парламент по предложение на сглобката. Затова и споразумението за кабинета „Желязков“ предвижда управляващите да обсъдят възможност за кандидати и на други формации. Някои започнаха да подсказват, че това би било шанс за ПП–ДБ, след като изгубиха възможността да участват в правителството.
На 5 януари, час след края на поредните разговори между ГЕРБ и „Демократична България“, от партията на Бойко Борисов съобщиха, че ги прекратяват заради нежеланието на ДБ да подкрепи Росен Желязков за премиер. Запазвайки тогава мълчание, ДБ проговориха едва сега, за да обявят, че не са били информирани предварително за решението на ГЕРБ и че мерките, които биха изолирали Пеевски от институционалното обновление, са останали извън споразумението.
Затова пък другото ДПС не е в изолация. А и все едно кое ДПС. Движението винаги е било част от статуквото, също и от тъмните нелегитимни мрежи на влияние, функциониращи зад кулисите на институциите. Какво се е променило? Да не би ДПС да дава своя десятък в борбата за правова държава, отказвайки се от дял във властта, само и само врагът Пеевски начело на другия брат близнак да е в опозиция? Оглавяваната от Ахмед Доган партия ДПС – Демокрация за права и свободи, успешно изигра ролята на жертва на олигарха, но виктимизацията, свързана с натиск върху активисти и кметове и с антикорупционни и прокурорски „бухалки“, не пречи да бъде поставен въпросът с какво ценностно едното ДПС е по-различно от другото. В крайна сметка тяхното ДНК е не просто сходно, а идентично.
Отделянето на Пеевски с част от някогашния елит на ДПС и със създаден от него нов не променя същността на формацията, разделила се на две. Едно е ясно – политическата аритметика може да изглежда различна, но правилата на играта в българската политика остават непроменени.
Засега обаче кръгът около Доган е наложил стратегическата фасада на политическа сила, която не иска нищо в замяна на подкрепата си. Същото направи и Пеевски в предходния парламент в опит да се препозиционира като конструктивен играч в процеса на изграждане на „правова държава“ и в предните редици на евроатлантиците.
С въздишки на облекчение
Липсата на открити претенции за участие във властта може да е ход за намаляване на общественото недоволство, докато зад кулисите се дърпат конците. ДПС има черен колан в тази игра на влияние, а „изпуснатата“ в навечерието на връчването на мандата информация, че искат постове, но им е отказано, е просто игра. Така, от една страна, се демонстрира, че без тях не може, от друга – колко твърди и непреклонни са ГЕРБ. Обществото обаче едва ли вярва, че ДПС е обикновена подпора на правителството и мнозинството, а въпросът какво е поискало, скоро ще намери своя отговор в реализацията на приоритетите.
След гласуването на правителството, избрано повече от 80 дни след изборите, въздишките на облекчение са повече, независимо от реториката в пленарната зала. Партиите не искат нови избори. Дори и за някои от най-кресливите в опозиция, каквито са „Възраждане“ и МЕЧ, е по-изгодно да са част от работещ парламент, макар че конкуренцията в тази част на политическия спектър е огромна, а избирателите на Костадин Костадинов се умориха да чакат кога ще вземат властта.
За ГЕРБ–СДС би било недопустимо отново да се провалят в опита да съставят правителство. А и във всеки момент могат да разтурят коалицията, в случай че започне да им пари под краката. Бойко Борисов не влиза в конфронтация с Пеевски.
ГЕРБ има шанс да извлече позитиви след влизането на България в еврозоната, което е все по-вероятно да стане от 1 януари 2026 г. Така Борисов ще се похвали с пълен цикъл, след като в края на третото му правителство България беше приета в Европейския банков съюз и в т.нар. чакалня на еврозоната – механизма на валутните курсове ΕΡΜ II.
В споразумението за съставяне на кабинета пътят към еврото е изчерпан с изречението:
4.4. Продължаване на усилията за членство на България в еврозоната.
Засега министрите на БСП, която открито се противопоставя на този процес, избягват коментари по темата. Те най-вероятно са заети да четат списъци за назначения, които в скоро време ще извършат.
За еврозоната другият партньор във властта – ИТН, мисли като „Възраждане“: някой ден, но не сега. Нали двете политически сили заедно искаха да правят такъв референдум. По Нова телевизия в петък депутатът от ИТН Станислав Балабанов обясни позицията.
ИТН са „за“ България да влезе в еврозоната, но когато е готова – с тази дупка от 18 млрд. лева по-скоро не е готова.
За ПП–ДБ оставането в опозиция ще е изпитание и за лидерството им, и за вътрешнокоалиционните връзки – напрежението между двете формации е видимо, а фактът, че преговорите с ГЕРБ водеше само ДБ, намали шансовете за добър изход. В първите часове след гласуването на новия кабинет от „Продължаваме промяната“ обявиха, че пускат канал в ΥοuTube „Опозиция“, в който ежедневно ще представят позициите си.
Борисов пък обвини лидерите на ПП в съглашателство с Пеевски и неговото ДПС – Ново начало, споменавайки за „погледите като на мартенски мачароци между Асен Василев и Данчо Цонев“.
Всички колеги много искахме „Да, България“ да влезе в правителството. Затова приехме всички компромиси за съдебната реформа. Затова и чакахме до последно. Ние положихме много усилия с ДБ. Но не стана. Затова преценихме, че по-добрият вариант е АПС. Защото няма нужда от празнодумни декларации, които повече от месец да ми ги веят. Когато вкарваш в правителството най-големия враг на Делян Пеевски – Ахмед Доган… Как по-ясно да го кажа?! Да ви кажа, че няма да работим с Пеевски?! Няма да работим с Пеевски.
Запазването на Борислав Сарафов като и.ф. главен прокурор за още шест месеца не вещае добри новини за ръководството на ПП в лицето на Кирил Петков, Лена Бориславова и Асен Василев. На първите двама бяха поискани имунитетите, но Бориславова не се е отказала от своя, за разлика от Петков. Василев е застрашен от евентуални показания на сътрудника му Лъчезар Ставрев, арестуван за длъжностно престъпление и пране на пари и оставен за постоянно в ареста от Софийския апелативен съд. Много свидетелски показания изтекоха контролирано в медии, свързвани с Пеевски.
Лика-прилика
А обединилите се в правителство политически сили повече си приличат, отколкото се различават. Консерватизмът им започна да личи още повече след избора на Доналд Тръмп за американски президент, също и проруските симпатии, изразени по-слабо или по-силно при всяка от тях. (Лидерът на ИТН Слави Трифонов беше поздравил Доналд Тръмп за избирането му като американски президент като част от общото консервативно семейство.) Коалиралите се в правителството партии могат да бъдат разграничени единствено по формални белези, като членство в европейското политическо семейство например. Макар че БСП е твърде далеч от европейските социалдемократи.
Част от този консервативно-патриотичен блок е и президентът Румен Радев, без чието съдействие правителството не би било възможно. За първи път ГЕРБ ще управлява с министър-председател, който не се нарича Бойко Борисов. Това би могло да донесе само неприятности на Росен Желязков въпреки неговата маневреност и опит и в ГЕРБ, и в държавната администрация.
В парламента цялата отговорност за укрепване на мнозинството пада на гърба на Борисов. Лидерите на БСП са в правителството, групата лесно може да бъде „пробита“. ИТН са доказали, че не са от най-стабилните съюзници. Ако партия „Величие“ влезе в парламента, мнозинството става трудно за удържане и с цената на кой знае какви компромиси.
Консервативният удобен брак ще издържи ли?
Social Engineering to Disable iMessage Protections
Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2025/01/social-engineering-to-disable-imessage-protections.html
I am always interested in new phishing tricks, and watching them spread across the ecosystem.
A few days ago I started getting phishing SMS messages with a new twist. They were standard messages about delayed packages or somesuch, with the goal of getting me to click on a link and entering some personal information into a website. But because they came from unknown phone numbers, the links did not work. So—this is the new bit—the messages said something like: “Please reply Y, then exit the text message, reopen the text message activation link, or copy the link to Safari browser to open it.”
I saw it once, and now I am seeing it again and again. Everyone has now adopted this new trick.
One article claims that this trick has been popular since last summer. I don’t know; I would have expected to have seen it before last weekend.
В черната кутия на изкуствения интелект
Post Syndicated from Диана Кулчицкая original https://www.toest.bg/v-chernata-kutiya-na-izkustveniya-intelekt/

В последните години все повече се говори за изкуствения интелект (ИИ). През изминалата 2024 година той продължи да показва стремителен ръст в най-различни сфери. Технологията стана още по-разпространена и със сигурност можем да кажем, че съвременният човек се сблъсква с ИИ почти постоянно, макар и невинаги да си дава сметка за това. Когато използваме програми за автоматичен превод, когато търсим нещо в интернет, когато включваме гласовия помощник в нашия телефон, ние си имаме работа cъс самообучаващи се алгоритми. Те вече са част от нашия живот и в близко време няма да изчезнат.
Независимо от широкото разпространение на ИИ, в масовото съзнание той остава нещо като черна кутия, от която може да излезе какво ли не. Често самата технология се възприема като мистична, понякога дори зловеща. Най-песимистично настроените рисуват апокалиптично бъдеще, в което човечеството е във властта на машините. Други пък са излишно оптимистични и виждат само положителните аспекти на внедряването на ИИ, бързат да го прилагат безконтролно дори там, където това създава сериозни рискове. Може би по-балансираният и рационален подход би могъл да помогне да не отричаме ползите от тази иновация, но и да не си затваряме очите за съвсем реалните заплахи.
Развитието на ИИ през 2024 г.
2024-та беше белязана от много ключови събития, свързани с ИИ. Почти масов стана визуалният генеративен изкуствен интелект, който позволява да се създават изображения и видеа. Инструменти като Midjourney и DALL-E генерираха големи печалби и привлякоха милиони потребители по целия свят. През изминалата година ИИ започна по-активно да се използва в сферата на медицината и здравеопазването. При разработването на нови лекарства учените все по-често прибягват до него и тези опити вече носят конкретни резултати. Освен това доста малки и средни бизнеси използват ИИ в практиката си. Отминаха времената, когато технологията беше достъпна само за големите компании със сериозни финансови възможности.
През изминалата година обаче имаше и трудности за софтуерните гиганти, които разработват ИИ. Още в края на 2023 г. световноизвестният американски вестник New York Times заведе дело срещу Open AI. Всекидневникът обвини създателите на Open AI, че са нарушили авторските права и са използвали нерегламентирано текстовете на медията. Делото стана повод за голяма дискусия относно интелектуалното право в епохата на ИИ. Някои анализатори изказаха мнение (вж. например тук, тук и тук), че е по-добре да захранваме ИИ с качествени текстове вместо с всевъзможни източници, много от които със съмнителна стойност, за да може езиковият модел да се учи и да работи с проверени данни. Несъгласието на големите традиционни медии да предоставят съдържанието си осуетява този процес.
В България 2024 година също беше богата на събития, свързани с ИИ. През есента институтът INSAIT представи bgGPT – първия езиков модел изцяло на български. Той разполага с повечето функции, които притежава ChatGPT на компанията Open AI, но работи с български източници и е изцяло безплатен. Освен това родните медии за първи път открито започнаха да прилагат активно ИИ за изготвяне на дописки. Появи се и първият виртуален водещ, генериран от ИИ. През март Bulgaria On Air представи Иван, който е създаден изцяло с помощта на ИИ и си партнира в сутрешния блок на телевизията с двама истински водещи.
Общ поглед към развитието на ИИ
Според теорията за дифузия на иновациите, популяризирана от Евърет Роджърс през 1962 г., всяка технология преминава през стандартни етапи в своето разпространение, преди да стане масова. Първоначално има малка група от иноватори, които я създават и допринасят за развитието ѝ. След това се появява т.нар. ранно мнозинство. То се състои от хора с напредничаво мислене, които не се страхуват от новото. Те започват да използват технологията и да я популяризират. После идва късното мнозинство. Накрая, когато дадена технология вече е станала масова, се появяват изоставащите – онези, които доста късно решават да се обърнат към иновацията.
Ако анализираме ИИ от тази гледна точка, ще видим, че технологията вече започва да става масова, но още не е минала пиковия си момент на развитие. Както при разпространението на други технологии, високите очаквания, а също и крайно изразените страхове показват, че още не сме съвсем наясно къде ще ни отведе ИИ. В същото време от статистическа гледна точка през изминалата година разпространението му става доста масово. Проучване на McKinsey, публикувано през май 2024 г., показва, че използването на ИИ в работна среда продължава да расте. Все повече хора признават, че интегрират технологията в работата си по един или друг начин. Според проучването, включващо участници от цял свят, около 65% от запитаните казват, че в техните организации ИИ се използва редовно. Това число представлява почти двойно увеличение в сравнение с 2023 г.
Отношенията между ИИ и човека. Реални и потенциални проблеми
Известният британски математик и информатик Стюарт Ръсел е привърженик на „човешки центрирания“ подход към ИИ. Той смята, че технологията трябва да служи на човека, а не да преследва свои собствени цели. За момента все още не съществува свръхинтелект, тоест машина, която притежава съзнание и може да действа самостоятелно. Днес използваме алгоритми, които имат доста конкретно и ограничено приложение. Това обаче не значи, че в близкото бъдеще няма да се появи компютър, който притежава когнитивните способности на човека и дори ги превъзхожда.
Ръсел също така отбелязва, че не бива да се позволява на ИИ да взема решения, които са свързани със съдбата на човека. Например ученият смята, че използването на оръжие, управлявано от ИИ, може да доведе до катастрофални последствия, дори до геноцид.
Ако създаването на свръхефективен ИИ за момента е по-далечна перспектива, сегашната информационна среда крие по-осезаеми рискове. Манипулирането на данни и създаването на фалшиви видеа с помощта на ИИ никога не е било толкова лесно, колкото е в момента. Deep fake клипове са залели социалните медии. Днес на практика всеки може да създаде подобно съдържание, дори не е необходимо да притежава скъп софтуер и специални умения. Това прави дезинформацията и злонамереното изопачаване на фактите много по-лесно.
Друг проблем е свързан с неконтролираното използване на ИИ от ученици и студенти. Писането на есета само с помощта на ChatGPT, без редактиране и осмисляне на предложения от него вариант, води до това, че умението за създаване на авторски текстове се губи. Може би забраната на използването на ИИ в обучението не е най-добрата идея, но със сигурност има нужда да се формулират нови правила за оценяване и нови задания, които да не изкушават учащите се да прибягват до ИИ за решаване на всеки въпрос.
Трети проблем, който активно се обсъжда в различни индустрии, са промените в пазара на труда и отпадането на някои специалности, в които човекът може да бъде заменен от ИИ. Такава заплаха потенциално съществува, но е доста преувеличена. За момента ИИ прекрасно се справя с механични задачи, изчисления и търсене на закономерности, но не е добър в творчеството, защото работи със шаблони. Той може да бъде използван и в дизайна, и в изкуството, обаче без необходимата намеса на човека понякога създава произведения със съмнителна художествена стойност, макар и да има интересни попадения.
Политика и ИИ
ИИ вълнува не само учените и обикновените потребители, но и политиците. САЩ продължават да бъдат лидер в сферата, но и Европейският съюз не иска да изостава в тази технологична надпревара. От една страна, през 2024 г. видяхме големи инвестиции в технологичните компании в Европа. От друга страна обаче, станахме свидетели на приемането на първите общоевропейски регулации на ИИ. В ЕС те са най-строгите, ако ги сравняваме с въведените в САЩ и Китай. Налагането на правила в тази сфера със сигурност е необходимо, но и прекалената регулация може да изиграе лоша шега на европейската ИИ индустрия, тъй като е възможно да стопира – или поне да забави – развитието на иновацията със създаването на бюрократични пречки.
Великобритания също не иска да изостава в тази надпревара. Преди броени дни премиерът на Обединеното кралство Киър Стармър направи изявление, посветено на ИИ. Стармър каза, че технологията вече е част от днешната реалност и че той иска неговата държава да е начело на новата технологична революция, която вече е в ход по света.
Старият страх от новите технологии
Всяко ново изобретение първоначално буди страх и неразбиране. Така е било с радиото в началото на неговото развитие. Някои са смятали, че децата няма да могат да заспят след слушането на радиопредавания и ще сънуват кошмари. Известно е, че изобретяването на телефона също е предизвикало много бурни реакции. Има исторически свидетелства, че мнозина са смятали телефонните линии за проводници на зли духове. Класикът на българската литература Иван Вазов получил като подарък един от първите телефони в България, но отказвал да го използва.
Изкуственият интелект буди сериозни притеснения сред хората. Мнозина смятат, че ще загубят работните си места, че децата ще затъпеят и няма да искат да мислят сами, а програмите за генериране на съдържание ще убият креативността като цяло.
Много учени отбелязват, че ИИ е поредният инструмент, който може да се използва както за добро, така и за лошо. Както казва Лин У от Университета в Пенсилвания (САЩ), трябва да си дадем сметка в какво са добри хората, в какво – машините и как те могат да работят заедно, за да постигнат по-добри резултати. Тя също така смята, че ако човек е добър в дадена сфера и използва ИИ, може да стане само по-ефективен. Но ако не е добър в работата си и залага изцяло на алгоритмите, това може да му попречи сериозно. Винаги трябва критично да се отнасяме към резултатите, получени с помощта на ИИ, защото технологията не е безупречна и вероятно никога няма да бъде. Затова критичното мислене и медийната грамотност са ключови за минимизиране на рисковете, свързани с ИИ.
Coup D’état
Post Syndicated from The History Guy: History Deserves to Be Remembered original https://www.youtube.com/watch?v=HfBqGT_oUS0
Comic for 2025.01.17 – Incoming Danger
Post Syndicated from Explosm.net original https://explosm.net/comics/incoming-danger
New Cyanide and Happiness Comic
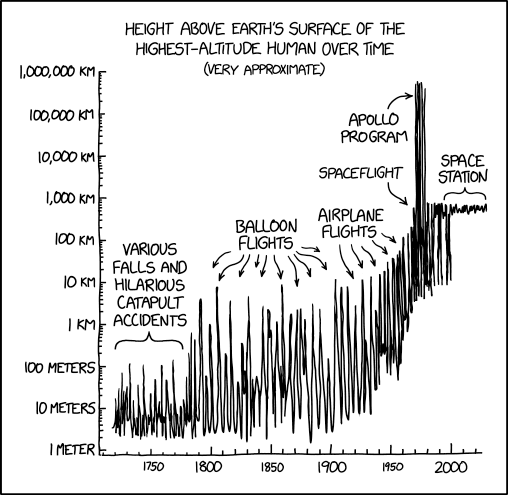
Human Altitude
Post Syndicated from xkcd.com original https://xkcd.com/3039/
A First in Discovery
Post Syndicated from The History Guy: History Deserves to Be Remembered original https://www.youtube.com/watch?v=Cgh8Kp83faY
Lenovo Buying Infinidat for Enterprise Storage
Post Syndicated from Cliff Robinson original https://www.servethehome.com/lenovo-buying-infinidat-for-enterprise-storage/
Lenovo is buying Infinidat to bolster its offerings in the enterprise storage space and increase coverage in its infrastructure solutions
The post Lenovo Buying Infinidat for Enterprise Storage appeared first on ServeTheHome.
Serverless ICYMI Q4 2024
Post Syndicated from Eric Johnson original https://aws.amazon.com/blogs/compute/serverless-icymi-q4-2024/
Welcome to the 27th edition of the AWS Serverless ICYMI (in case you missed it) quarterly recap. At the end of a quarter, we share the most recent product launches, feature enhancements, blog posts, webinars, live streams, and other interesting things that you might have missed!
In case you missed our last ICYMI, check out what happened in Q2 here.

2024 Q4 calender
Serverless at re:Invent 2024
AWS re:Invent 2024 had 60,000 in-person attendees and 400,000 online viewers for the keynotes. The conference delivered 1,900 sessions from 3,500 speakers and included 546 AWS service and feature announcements.
The serverless content consisted of two tracks: Serverless (SVS) and App Integration (API). These tracks included 70 unique sessions and attracted nearly 11,000 attendees. Serverlesspresso, the coffee shop powered by serverless technology, operated in two locations during the event: the Expo Hall and the certification lounge.

Serverlesspresso booth in the expo hall
Videos are available on Serverless Land YouTube.
AWS Lambda and Amazon Elastic Container Service (Amazon ECS) 10-year anniversary.
AWS marked significant milestones in serverless computing, celebrating 10 years of AWS Lambda and Amazon ECS. Lambda now serves over 1.5 million monthly customers and processes tens of trillions of requests each month. Amazon ECS launches more than 2.4 billion container tasks weekly and is used by over 65% of new AWS container customers.
AWS is commemorating this anniversary with insights from AWS Serverless Heroes, product leads, principal engineers, and AWS leadership sharing their perspectives on serverless evolution and future directions. These stories and insights are available at https://aws.amazon.com/serverless/10th-anniversary/.
AWS Lambda
The AWS Lambda team has spent a significant amount of time improving the Lambda development experience. Several enhancements have been made in the console as well as the local development experience.

Code-OSS as the new AWS Lambda inline editor
Lambda has launched a significant upgrade to its console by integrating Code-OSS, the open-source version of Visual Studio Code, delivering a familiar development experience directly in the cloud. The new Lambda Code Editor supports viewing larger function packages up to 50 MB, features a split-screen interface for simultaneous code editing and testing, and includes built-in Amazon Q Developer AI assistance for real-time coding suggestions. This enhancement comes at no additional cost and prioritizes accessibility with features like screen reader support and keyboard navigation. The update bridges the gap between cloud and local development by simplifying the process of downloading function code and AWS SAM templates, ultimately providing developers with a more streamlined and familiar serverless development experience. Watch the video explaining the changes in detail.
Additionally, the Lambda console enhances developer experience with two new features: a built-in CloudWatch Metrics Insights dashboard that surfaces key function metrics, and CloudWatch Logs Live Tail support for real-time log streaming and analysis, enabling faster troubleshooting without leaving the Lambda environment.

Top 10 Functions
Lambda now supports native JSON structured logging for .NET managed runtime applications, improving log searchability and analysis capabilities without requiring manual configuration of logging libraries.
Lambda has expanded its runtime support by adding Python 3.13 and Node.js 22 as both managed runtimes and container base images, providing access to the latest language features and ensuring long-term support through October 2029 and April 2027, respectively.
Lambda SnapStart capability is now available for Python and .NET runtimes, delivering sub-second startup performance for latency-sensitive applications by caching initialized execution environments.

SnapStart support comparison
New CloudWatch metrics for Lambda Event Source Mappings provide enhanced visibility into event processing states for Amazon Simple Queue Service (SQS), Amazon Kinesis, and Amazon DynamoDB event sources, helping customers monitor and troubleshoot event processing issues.
Lambda introduces Provisioned Mode for Kafka event source mappings, allowing customers to optimize throughput by configuring dedicated event polling resources for applications with stringent performance requirements.
Finally, Lambda introduces an enhanced local development experience through the AWS Toolkit for Visual Studio Code, streamlining the serverless application development workflow. The update features a new Application Builder interface that guides developers through environment setup, offers sample applications, and provides quick-action buttons for common tasks like build, deploy, and invoke operations. Developers can now efficiently iterate on their code with features such as configurable build settings, step-through debugging, and the ability to sync local changes quickly to the cloud or perform full deployments. The toolkit integrates with AWS Infrastructure Composer for visual application building and includes comprehensive local testing capabilities with shareable test events. This enhancement simplifies the Lambda development process by enabling developers to author, test, debug, and deploy serverless applications without leaving their preferred IDE environment.

Local IDE getting started
Amazon ECS and AWS Fargate
AWS enhances observability for containerized applications with CloudWatch Application Signals for Amazon ECS, adding infrastructure metrics correlation to existing traces and logs monitoring, enabling operators to identify and resolve performance issues across their application stack.
Amazon ECS adds service revision and deployment history tracking, allowing customers to monitor changes, track ongoing deployments, and debug deployment failures for long-running applications deployed after October 25, 2024.

Service revisions and deployment history
Amazon ECS expands testing capabilities by supporting network fault injection experiments on AWS Fargate through AWS Fault Injection Service, enabling developers to verify application resilience using six different types of fault injection actions, including network disruptions and resource stress testing.
Amazon EventBridge
Amazon EventBridge announces significant performance improvements, reducing end-to-end latency by up to 94% from 2,235ms to 129.33ms at P99, enabling faster event processing for time-sensitive applications like fraud detection and gaming.
Amazon EventBridge and AWS Step Functions now integrate with private APIs through AWS PrivateLink and Amazon VPC Lattice, enabling secure connectivity between cloud and on-premises applications without custom networking code.

Connections to Private APIs
EventBridge API destinations introduces proactive OAuth token refresh for public and private authorization endpoints, helping prevent delays and errors by automatically refreshing tokens before expiration.
AWS Step Functions
AWS Step Functions introduces the ability to export workflows as CloudFormation or SAM templates directly from the AWS console, enabling repeatable provisioning across accounts. Developers can export and customize templates from existing workflows, and use AWS Infrastructure Composer to visually connect workflows with other AWS resources.
Step Functions also adds Variables and JSONata support to enhance workflow development. Variables allow data assignment and reference between states, simplifying payload management, while JSONata provides advanced data transformation capabilities, including date formatting and mathematical operations. These features reduce the need for custom code and intermediate states, making it easier to build distributed serverless applications. Watch the in depth video to learn more.

JSONata and variables
Amazon Kinesis
Amazon Kinesis introduces significant updates to its client libraries. The new Kinesis Client Library (KCL) 3.0 reduces compute costs by up to 33% through enhanced load balancing, while the Kinesis Producer Library (KPL) 1.0 improves performance and security. Both libraries now support AWS SDK for Java 2.x and eliminate dependencies on SDK for Java 1.x, enabling seamless upgrades without requiring application code changes.

KCL 3.0 metrics
Amazon MQ
Amazon MQ adds support for AWS PrivateLink, enabling customers to access Amazon MQ API endpoints directly from their VPC through interface VPC endpoints, eliminating the need for internet access and providing enhanced security through AWS’s internal network infrastructure.
Amazon Finch
AWS announces general availability of Linux support for Finch, an open source container development tool that simplifies building, running, and publishing Linux containers across all major operating systems. The release includes support for the Finch Daemon with Docker API compatibility and is available through RPM packages for Amazon Linux 2 and Amazon Linux 2023.
Amazon Simple Queue Service (SQS)
Amazon SQS increases the in-flight message limit for FIFO queues from 20,000 to 120,000 messages, enabling higher concurrent message processing. This enhancement allows customers to scale their receivers and process up to six times more messages simultaneously, provided they have sufficient publish throughput.
Amazon Managed Streaming for Apache Kafka(Amazon MSK)
Amazon MSK now introduces Managed Streaming for Apache Flink blueprints to simplify real-time AI application development. The service enables vector-embedding generation through Amazon Bedrock, streamlining the integration of streaming data with generative AI models. Using a straightforward configuration process, users can generate and index vector embeddings in Amazon OpenSearch, while leveraging LangChain’s data chunking capabilities for enhanced data retrieval efficiency. The service handles all integration aspects between MSK, embedding models, and Amazon OpenSearch vector stores.
AWS Amplify
AWS Amplify launches the Amplify AI kit for Amazon Bedrock, providing fullstack developers with tools to integrate AI capabilities into web applications. The kit includes a customizable React UI component, secure Bedrock access, and context-sharing features, enabling developers to implement chat, search, and summarization functionalities without machine learning expertise.
AWS AppSync
AWS AppSync launches AppSync Events, enabling developers to broadcast real-time data to multiple subscribers through serverless WebSocket APIs. The service eliminates the need to build and manage WebSocket infrastructure while providing secure, scalable event broadcasting capabilities. Developers can create APIs that automatically scale and integrate with services like Amazon EventBridge. The system supports features such as channel namespaces, event handlers, and multiple authorization modes, and is available in all regions where AWS AppSync operates. Users only pay for API operations and real-time connection minutes used.

Creating an AppSunc Event API
Amazon API Gateway
Amazon API Gateway released a significant enhancement to Amazon API Gateway, enabling customers to manage private REST APIs using custom private DNS names. This highly requested feature allows API providers to use user-friendly domain names like private.example.com, while maintaining TLS encryption for security. The implementation process involves creating a private custom domain, configuring certificates through AWS Certificate Manager (ACM), mapping private APIs, and setting resource policies. The feature supports cross-account sharing through AWS Resource Access Manager (AWS RAM) and is now available in all AWS Regions, including AWS GovCloud (US).
Serverless blog posts
October
- Designing Serverless Integration Patterns for Large Language Models (LLMs)
- Simplifying Lambda function development using CloudWatch Logs Live Tail and Metrics Insights
- Introducing an enhanced in-console editing experience for AWS Lambda
- Introducing an enhanced local IDE experience for AWS Lambda developers
November
- Python 3.13 runtime now available in AWS Lambda
- The serverless attendee’s guide to AWS re:Invent 2024
- Serverless containers at AWS re:Invent 2024
- Implementing custom domain names for private endpoints with Amazon API Gateway
- Node.js 22 runtime now available in AWS Lambda
- Introducing new Event Source Mapping (ESM) metrics for AWS Lambda
- How Infinitium reduced fraud detection time by 95% with Amazon ECS and AWS Fargate on AWS Graviton
- Improving deployment visibility for Amazon ECS services
- Simplifying developer experience with variables and JSONata in AWS Step Functions
- Automating event validation with Amazon EventBridge Schema Discovery
- Implementing transactions using JMS2.0 in Amazon MQ for ActiveMQ
- Optimize compute resources on Amazon ECS with Predictive Scaling
- Introducing Provisioned Mode for Kafka Event Source Mappings with AWS Lambda
- Transforming Istio into an enterprise-ready service mesh for Amazon ECS
Serverless Office Hours

Serverless office hours videos
October
- Oct 1 – Fullstack apps with Amplify Gen 2
- Oct 8 – Step Functions + containers
- Oct 22 – GraphQL fun with AppSync
- Oct 29 – Serverless testing with Pawel Zubkiewicz
November
- Nov 5 – Stripe event destinations
- Nov 12 – 10 years of Lambda & ECS
- Nov 19 – Enhancing Lambda DevEx
- Nov 25 – pre:Invent 2024
Still looking for more?
The Serverless landing page has more information. The Lambda resources page contains case studies, webinars, whitepapers, customer stories, reference architectures, and even more Getting Started tutorials.
You can also follow the Serverless Developer Advocacy team on X (formerly Twitter) to see the latest news, follow conversations, and interact with the team.
- Eric Johnson: @edjgeek
- Julian Wood: @julian_wood
- Marcia Villalba: @mavi888uy
- Romain Jourdan: @rjourdan_net
And finally, visit the Serverless Land for all your serverless needs.
$90 Foam Insert for Starlink Mini: Worth It?
Post Syndicated from Crosstalk Solutions original https://www.youtube.com/watch?v=imfKI-2T_SE
The many names of commit 55039832f98c
Post Syndicated from corbet original https://lwn.net/Articles/1005222/
The kernel is, on its face, a single large development project, but
internally it is better viewed as 100 or so semi-independent projects all
crammed into one big tent. Within those projects, there is a fair amount
of latitude about how changes are managed, and some subsystems are using
that freedom in the search for more efficient ways of working. In the end,
though, all of these sub-projects have to work together and interface with
kernel-wide efforts, including the stable-release and CVE-assignment
processes. For some time, there has been friction between the direct
rendering (DRM, or graphics) subsystem and the stable maintainers; that
friction recently burst into view in a way that shows some of the
limitations of how the kernel community manages patches.
Automate topic provisioning and configuration using Terraform with Amazon MSK
Post Syndicated from Vijay Kardile original https://aws.amazon.com/blogs/big-data/automate-topic-provisioning-and-configuration-using-terraform-with-amazon-msk/
As organizations deploy Amazon Managed Streaming for Apache Kafka (Amazon MSK) clusters across multiple use cases, the manual management of topic configurations can be challenging. This can lead to several issues:
- Inefficiency – Manual configuration is time-consuming and error-prone, especially for large deployments. Maintaining consistency across multiple configurations can be difficult. To avoid this, Kafka administrators often set the create.topics.enable property on brokers, which leads to cluster operation inefficiency.
- Human error – Manual configuration increases the risk of mistakes that can disrupt data flow and impact applications relying on Amazon MSK.
- Scalability challenges – Scaling an Amazon MSK environment with manual configuration is cumbersome. Adding new topics or modifying existing ones requires manual intervention, hindering agility.
These challenges highlight the need for a more automated and robust approach to MSK topic configuration management.
In this post, we address this problem by using Terraform to optimize the configuration of MSK topics. This solution supports both provisioned and serverless MSK clusters.
Solution overview
Customers want a better way to manage the overhead of topics and their configurations. Manually handling topic configurations can be cumbersome and error-prone, making it difficult to keep track of changes and updates.
To address these challenges, you can use Terraform, an infrastructure as code (IaC) tool by HashiCorp. Terraform allows you to manage and provision infrastructure declaratively. It uses human-readable configuration files written in HashiCorp Configuration Language (HCL) to define the desired state of infrastructure resources. These resources can span virtual machines, networks, databases, and a vast array of cloud provider-specific offerings.
Terraform offers a compelling solution to the challenges of manual Kafka topic configuration. Terraform allows you to define and manage your Kafka topics through code. This approach provides several key benefits:
- Automation – Terraform automates the creation, modification, and deletion of MSK topics.
- Consistency and repeatability – Terraform configurations provide consistent topic structures and settings across your entire Amazon MSK environment. This simplifies management and reduces the likelihood of configuration drift.
- Scalability – Terraform enables you to provision and manage large numbers of MSK topics, facilitating the growth of your Amazon MSK environment.
- Version control – Terraform configurations are stored in version control systems, allowing you to track changes, roll back if needed, and collaborate effectively on your Amazon MSK infrastructure.
By using Terraform for MSK topic configuration management, you can streamline your operations, minimize errors, and have a robust and scalable Amazon MSK environment.
In this post, we provide a comprehensive guide for using Terraform to manage Amazon MSK configurations. We explore the process of installing Terraform on Amazon Elastic Compute Cloud (Amazon EC2), defining and decentralizing topic configurations, and deploying and updating configurations in an automated manner.
Prerequisites
Before proceeding with the solution, make sure you have the following resources and access:
- To simplify the setup, use the provided AWS CloudFormation template. This template will create the necessary Amazon MSK provisioned cluster and required resources for this post. You can create an MSK Serverless cluster using the Amazon MSK console and use it in this solution. This is sample template, not production ready, and AWS Identity and Access Management (IAM) policies should be implemented using best practices and the principle of least privilege. For more details, see Get started with AWS managed policies and move toward least-privilege permissions. An EC2 instance will be created as a part of this template. The MSK cluster and EC2 instance will be created on a single virtual private cloud (VPC); however, you can install Terraform in a different account or on different VPC. For more details, see Connect Kafka client applications securely to your Amazon MSK cluster from different VPCs and AWS accounts.
- For this post, we use the latest Terraform version (1.10.x) and Terraform plugins – Mongey/Kafka provider. In Terraform, plugins are binary executables responsible for implementing resource types and providers. The plugins are installed automatically when we initialize a Terraform configuration using the terraform init
- You need access to an AWS account with sufficient permissions to create and manage resources, including IAM roles and MSK clusters. For more information, see IAM access control.
By making sure you have these prerequisites in place, you will be ready to streamline your topic configurations with Terraform.
Install Terraform on your client machine
When your cluster and client machine are ready, SSH to your client machine (Amazon EC2) and install Terraform.
- Run the following commands to install Terraform:
- Run the following command to check the installation:

This indicates that Terraform installation is successful and you are ready to automate your MSK topic configuration.
Provision an MSK topic using Terraform
To provision the MSK topic, complete the following steps:
- Create a new file called
main.tfand copy the following code into this file, replacing the BOOTSTRAP_SERVERS and AWS_REGION information with the details for your cluster. For instructions on retrieving thebootstrap_serversinformation for IAM authentication from your MSK cluster, see Getting the bootstrap brokers for an Amazon MSK cluster. This script is common for Amazon MSK provisioned and MSK Serverless. - Add IAM bootstrap servers endpoints in a comma separated list format:
- Run the command
terraform initto initialize Terraform and download the required providers.

The terraform init command initializes a working directory containing Terraform configuration files(main.tf). This is the first command that should be run after writing a new Terraform configuration.
- Run the command
terraform planto review the run plan.

This command shows the changes that Terraform will make to the infrastructure based on the provided configuration. This step is optional but is often used as a preview of the changes Terraform will make.
- If the plan looks correct, run the command
terraform applyto apply the configuration. - When prompted for confirmation before proceeding, enter
yes.

The terraform apply command runs the actions proposed in a Terraform plan. Terraform will create the sampleTopic topic in your MSK cluster.
- After the
terraform applycommand is complete, verify the infrastructure has been created with the help of the kafka-topics.sh utility:

You can use the kafka-toipcs.sh tool with the --list option to retrieve a list of topics associated with your MSK cluster. For more information, refer to the createtopic documentation.
Update the MSK topic configuration using Terraform
To update the MSK topic configuration, let’s assume we want to change the number of partitions from 50 to 10 on our topic. We need to perform the following steps:
- Verify the number of partitions on the topic using the
--describecommand:

This command will show 50 partitions on the sampleTopic topic.
- Modify the Terraform file
main.tfand change the value of the partitions parameter to 10: - Run the command
terraform planto review the run plan.

- If the plan shows the changes, run the command
terraform applyto apply the configuration. - When prompted for confirmation before proceeding, enter
yes.

Terraform will drop and recreate the sampleTopic topic with the changed configuration.
- Verify the changed number of partitions on the topic, ad rerun the
--describecommand:

Now, this command will show 10 partitions on the sampleTopic topic.
Delete the MSK topic using Terraform
When you no longer need the infrastructure, you can remove all resources created by your Terraform file.
- Run the command
terraform destroyto remove the topic. - When prompted for confirmation before proceeding, enter
yes.

Terraform will delete the sampleTopic topic from your MSK cluster.
- To verify, rerun the
--listcommand:

Now, this command will not show the sampleTopic topic.
Conclusion
In this post, we addressed the common challenges associated with manual MSK topic configuration management and presented a robust Terraform-based solution. Using Terraform for automated topic provisioning and configuration streamlines your processes, fosters scalability, and enhances flexibility. Additionally, it facilitates automated deployments and centralized management.
We encourage you to explore Terraform as a means to optimize Amazon MSK configurations and unlock further efficiencies within your streaming data pipelines.
About the author
 Vijay Kardile is a Sr. Technical Account Manager with Enterprise Support, India. With over two decades of experience in IT Consulting and Engineering, he specializes in Analytics services, particularly Amazon EMR and Amazon MSK. He has empowered numerous enterprise clients by facilitating their adoption of various AWS services and offering expert guidance on attaining operational excellence.
Perfect Fit or Business Threat? How to Mitigate the Risk of Rogue Employees
Post Syndicated from Chris Boyd original https://blog.rapid7.com/2025/01/16/perfect-fit-or-business-threat-how-to-mitigate-the-risk-of-rogue-employees/
Rogue employees present significant financial and cybersecurity risks to organizations. Rapid7 threat researchers and penetration testers are actively observing how malicious actors exploit hiring pipelines to infiltrate businesses. This blog highlights real-world tactics, including:
- Insider Reconnaissance: Rogue applicants leveraging interviews to map office layouts, identify vulnerable devices, and even plant malware during site visits.
- Tech Tricks: The use of deepfake technology, AI-generated photos, and VoIP to fake identities, bypass background checks, and mask locations.
- North Korean Operations: State-sponsored actors posing as remote IT workers with fake resumes and stolen identities to fund illicit activities like missile development.
- Hiring Weaknesses: Gaps in hiring processes—such as 43% of organizations skipping background checks—leaving businesses vulnerable to exploitation.
Read on to discover how to fortify your hiring and onboarding practices against this business risk.
Understanding the threat
Rogue employees have long been an issue for hiring departments. The Occupational Fraud 2024: A Report to the Nations study reported worldwide losses of more than $3.1 billion from 1,921 fraud cases. Other studies suggest that a typical business may lose as much as 5% of their annual revenue due to this problem. Sadly, the days of “only” having to worry about employees who show up late every day, or tell a few small tales on their work history record, are but a distant memory.
While organizations have been aware of the broad risk from bogus hires for some years, many are playing catch-up with hitherto unknown cybersecurity implications, particularly when state-sponsored actors are at the helm. For example, the FBI issued warnings about remote North Korean workers sending funds to the regime back in 2022, and estimated the number of fake North Korean workers to be in the thousands. These workers generate revenue for ballistic missile development, and according to a 2022 advisory “…may share access to virtual infrastructure, facilitate sales of data stolen by DPRK cyber actors, or assist with the DPRK’s money laundering and virtual currency transfers.”
Multiple examples of other DPRK-centric malicious employment fraud have gone public over the past year. Security education firm KnowBe4 highlighted the detection and removal of a North Korean worker, who’d bypassed various checks at the hiring stage and attempted to deploy malware. In October 2024, an unnamed firm revealed a similar ploy where a remote IT worker faked employment history, downloaded data, and issued a ransom demand. A few months prior to this, a Tennessee resident was arrested for his alleged involvement in a DPRK-centric laptop farm involving stolen identities and software installed without permission.
Even without North Korean involvement, there are many other ways rogue hires can cause security issues across a business. What else lies in wait for the unwary hiring department? More importantly, how can your organization combat these threats?
Rogue hire archetypes
Rogue hires fall into certain categories. Some are potentially more damaging to a business than others, with some overlap in terms of tactics and objectives. If you run into any of the below, then this is what you can expect them to be doing.
- Malicious applicants: They may be working alone, or as part of a team to steal financial or customer data. The incentive may be financial or tied to data exfiltration, but the attack’s starting point could involve phishing, malware deployment, or BEC (business email compromise). They may intend to continue as a rogue employee if hired, or plan to compromise a business at the physical interview stage and never be seen again.
- State-sponsored threat actors: These are commonly encountered as freelance workers from North Korea (albeit not exclusively), targeting positions in general IT support, mobile development, virtual currency exchanges, and firmware development across the US, Europe, and East Asia. They often present themselves as being Chinese, South Korean, and Japanese, while making use of forged or stolen identity documents. The FBI believes that most engage in non-malicious IT work, though some make use of privileged systems access to enable malicious cyber intrusions.
- Proxy employees: They receive one-off or continued payments from a real would-be employee in return for fielding the interviews. The proxy may also take on work-related tasks on behalf of the employee assuming the latter is ultimately hired. The FBI has previously warned that deepfake technology is often used for multiple remote work scams, with available positions granting access to “…customer PII (personal identifying information), financial data, corporate IT databases and/or proprietary information.”
The malicious applicant game plan
Malicious applicants may operate alone, but have the potential to be backed by groups or nations with access to a wide range of resources denied to more common fraudsters. These resources could include fake or stolen identity documents, or unknown malware and vulnerabilities. Their interests are frequently financial, but may veer into data exfiltration should the opportunity arise.
Some rogue hires may not intend to take on employment; instead, the interview is used as a pretext for more direct reconnaissance and malware deployment. To illustrate how a typical malicious applicant could exploit an interview process, a Rapid7 penetration tester shared their experience of a workplace infiltration assignment that they participated in:
“Standard OSINT techniques revealed several open interviews available while I was going to be on location. I typically review job postings for technology stacks the organization uses, in case I want to fall back on phishing campaigns. I also vet for potentially vulnerable endpoint software which may be in use. They did at least have a sign-in sheet and a guard to lead me to the interview.”
It’s worth noting that a penetration tester’s objectives and methods will differ from more targeted, state-sponsored attempts to compromise organizations for specific espionage or other goals. However, there will be some overlap across different groups and individuals.
“I was taken through a variety of rooms and offices, granting me a handy mental map of layout, equipment, possible locations of important devices like servers or network access. During the interview, I asked if I could visit the bathroom and was permitted to walk freely in the office. An unattended logged-in device could be susceptible to malware on a USB stick; I might find physical employee directories, or post-it note passwords. I’m wearing office clothes. If there’s no lanyard requirement enforced, who would suspect anything?”
A networked printer could be a launchpad for malware outbreaks or firmware manipulation. An unguarded stack of expense paper could help to pave the way for BEC once the interviewee has left the premises.
Seemingly innocent interview questions about standard business operations can lead to password reset phishing campaigns, designed to resemble familiar email login pages and MFA (multi-factor authentication) systems. From here, the attacker can use compromised accounts to perform social engineering, or gain deeper access into the network.
Fictitious HR workers can be deployed to send malware-laden hiring or policy documents via email domains imitating the real thing. There is a very real possibility in this scenario of long-term compromise and data exfiltration. Should the attacker decide to escalate further, they may turn to ransomware and double extortion, leading to blackmail and public data exposure.
Now that we’ve highlighted some of the worst-case scenarios from an interview gone wrong, we’ll explore in detail where the hiring pipeline is at its most exposed.
The riskiest stages of hiring
Assuming you’ve posted your job description, the key stages of ingress for bogus hires are now exposed to the wild. The three main areas of interaction are:
- Screening and shortlisting.
- The interview(s).
- Onboarding of successful hires.
Providing barriers to entry at each stage will increase the likelihood of catching rogue personnel.
Businesses most commonly search an applicant’s employment history, perform criminal record checks, and verify their education history [PDF, page 48]. Checks on social media, directorship searches, and specialist vetting are all less likely. However, an astonishing 43% of organizations surveyed said no background checks were run on perpetrators prior to hiring.
This piecemeal approach to hiring gives opportunists a direct line to your organization’s most valuable assets. Those fake HR workers mentioned earlier could just as easily have been bogus IT administrators, responsible for rolling your patches out to users of your software. Now you’re a compromised third-party vendor, enabling the flow of a supply chain attack to multiple customers. They, too, could be at risk from further network ingress, malware, and data exfiltration—all because you failed to perform any background checks on a potential hire.
Beyond this, most businesses do not generally vet staff once employed. This is why precautions are still advisable during initial hire or onboarding. KnowBe4 issuing a limited access laptop to the North Korean IT hire is one reason for the would-be attacker’s lack of success.
Screening and shortlisting
What they want to do:
- Present a convincing and comprehensive overview of experience and work history.
- Spread a veneer of credibility on the resume that dissuades further investigation.
What you need to do:
- Use an applicant tracking system (ATS). An ATS is invaluable for weeding out potential fakes. They’re very good at finding reused names, emails, or even phone numbers across multiple profiles. This is especially useful considering a typical job post can receive hundreds of applications an hour on LinkedIn alone.
- Third-party background checks. Many services offer to take on the responsibility of background checks from the employer, with some all-in-one solutions offering 100+ types of background check.
Explore LinkedIn data. If you suspect the candidate’s photograph is a stock image or AI generated, reverse image search and AI checking tools can help. In the KnowBe4 incident, the fake employee used AI to alter a stock photograph. Note that many other tricks exist to bypass checks, such as flipping the photograph horizontally or altering the colors.
You should also consider the authenticity of the profile. Has it been created very recently but boasts many years of work? Does the candidate claim 5 to 10 years of experience despite having few or no reputable contacts in the industry you work in? Are recommendations from co-workers entirely absent?
The interview
In an ideal situation for fraud, fake employees want to:
- Stay off camera.
- Answer your questions via a third-party through headset or offscreen.
- Use VoIP to mask their real location.
- Avoid discussing anything related to their background.
The interview: what you need to do
- Create phone and video rules. Insist on a VoIP-free phone call during the hiring process, whether landline or mobile. This, alongside other data gathered, can help you to decide if a candidate really is located in France, Belgium, or Scotland. For web calls, make camera interaction mandatory. Ask for blurred backgrounds (or similar features) to be disabled so you can see where the candidate really is.
Using cameras has many additional benefits, such as impeding the flow of a proxy hire (someone who is paid to take interviews on the potential employee’s behalf.) It’s much more difficult for fraudsters to take instructions from a headset or even mime(!) if you can see the candidate at all times. Being able to see candidates means there’s also less chance of totally different people showing up to subsequent interviews.
- Build a consistent picture. Are you permitted to use conferencing tools which allow you to view/log IP addresses or other relevant system information? Fraudsters (particularly proxy hires) use multiple people at different stages of the interview often separated by large distances. These small digital pointers could build up a very different picture of who you think you’re dealing with.
- Dig into background details. Select 2 or 3 pieces of information from a resume. This could be their hometown, a previous employer, or perhaps their area of expertise. Ask about what it was like growing up in the city they mention, or places of interest they enjoy in their hometown. Faltering answers may be a big clue.
If multiple interviews are planned, record these answers and have subsequent interviewers reuse a few questions. If the candidate is making it up as they go, then the story will quickly fall to pieces.
Onboarding
Even if a rogue has bypassed screening and interviews, you still have a chance to catch them in the act. Here’s what you can do at this stage:
- Restricting laptop or equipment pickup to a depot where valid identification is required will help prevent it from falling into the wrong hands.
- Ensure the device is running all required security tools, does not grant admin permissions, and provides access only to work-essential tools such as email, comms, and day-to-day necessities. The device should be “bare-bones” and not come with company data stored locally on the system.
- Do not allow the new hire any facility to upload files outside of necessities such as old payslips, ID, proof of address/utility bills, and tax details.
- If you use tools like Slack or Microsoft Teams, ensure the new hire is restricted from accessing channels they don’t need.
Someone who successfully passes the 3 interview steps above has a wealth of options at their disposal. They might immediately try to compromise systems or data before being discovered. Alternatively, they may spend weeks or months exfiltrating data and social engineering other employees. Initial knowledge of common business practices for laptops and remote security, system updates, and authentication can potentially make it easier for them to try and bypass measures in place. It’s a much better idea to not let them get anywhere near this stage in the first place.
Hire with confidence
Rogue workers of all types are a very real threat to your data security and business revenue. From security organizations to blockchain firms, anyone is potentially at risk from a bad hire. Adapting the above hiring practices and combining them with a defense-in-depth approach will help you proactively and confidently deal with these threats to your network, and the people using it.
Fortinet firewalls hit with new zero-day attack, older data leak
Post Syndicated from Caitlin Condon original https://blog.rapid7.com/2025/01/16/etr-fortinet-firewalls-hit-with-new-zero-day-attack-older-data-leak/
Executive summary
Rapid7 is investigating two separate events affecting Fortinet firewall customers:
- Zero-day exploitation of CVE-2024-55591, an authentication bypass vulnerability in FortiOS and FortiProxy disclosed earlier this week. Successful exploitation could allow remote attackers to gain super-admin privileges via crafted requests to the Node.js websocket module.
- A January 15, 2025 dark web post from a threat actor who looks to have published IPs, passwords, and configuration data from 15,000 FortiGate firewalls. The data leaked online appears to be several years old (2022). Rapid7 has not attributed any CVEs to the leaked data at this time.
FortiGate data leak
On Wednesday, January 15, 2025, a threat actor named “Belsen Group” published a trove of Fortinet FortiGate firewall data on the dark web, allegedly from 15,000 organizations. The data released included IP addresses, passwords, and firewall configuration information — a potentially significant risk for organizations whose data was leaked.
Security researcher Kevin Beaumont has an initial analysis of the leaked data, along with his assessment that the data leaked this week appears to be from 2022. After conducting our own outreach to potentially affected organizations, Rapid7 has also confirmed that at least some of the leaked data originated from 2022 incidents where customer firewalls were compromised. Based on Beaumont’s analysis and observations from our own investigations, it’s likely that the data dump published by the threat actor contains primarily or entirely older data.
Rapid7 has not attributed the data leak to a specific CVE at this time. Beaumont said his observations from incident responses indicate that CVE-2022-40684 (a Fortinet firewall zero-day flaw from 2022) may have been the initial access vector that allowed for the large-scale firewall data leak.
New Fortinet zero-day CVE also exploited in the wild
Separately, on Tuesday, January 14, 2025, Fortinet disclosed CVE-2024-55591, a new zero-day vulnerability affecting FortiOS and FortiProxy. Security firm Arctic Wolf had previously published a blog on threat activity targeting Fortinet firewall management interfaces exposed to the public internet, saying that “a zero-day vulnerability is likely” but an initial access vector had not been confirmed. According to Arctic Wolf, the campaign “involved unauthorized administrative logins on management interfaces of firewalls, creation of new accounts, SSL VPN authentication through those accounts, and various other configuration changes.”
Fortinet’s advisory for CVE-2024-55591 includes indicators of compromise (IOCs) and notes that the vulnerability was reported as exploited in the wild at time of disclosure. No individual or firm is explicitly credited for discovering the vulnerability in Fortinet’s advisory, and Fortinet has not confirmed that CVE-2024-55591 is the zero-day vulnerability Arctic Wolf speculated was being leveraged threat activity.
Rapid7 MDR threat hunters have observed activity from IP addresses publicly attributed to the threat campaign targeting CVE-2024-55591, but our team has so far only noted connections consistent with scanning or reconnaissance activity and not exploitation.
Zero-day vulnerabilities in Fortinet FortiOS, the operating system that runs on FortiGate firewalls, have been a relatively common occurrence in recent years and have been leveraged in a wide range of financially motivated, state-sponsored, and other attacks. In addition to CVE-2024-55591, prominent FortiOS zero-day flaws have included:
- CVE-2024-21762, an out-of-bounds write disclosed February 2024
- CVE-2023-27997, a heap-based buffer overflow disclosed June 2023
- CVE-2022-42475, a heap-based buffer overflow disclosed December 2022
- CVE-2022-40684, an authentication bypass (CWE-288) disclosed October 2022
- CVE-2018-13379, while not a zero-day, was disclosed in 2019 and allowed attackers to download SSL-VPN system files and steal credentials. It was consistently exploited in the years following disclosure despite a wide range of warnings and publicly available information on known threat activity.
Like CVE-2022-40684, CVE-2024-55591 is an authentication bypass using an alternate path or channel (CWE-288). While it does not currently appear likely that CVE-2024-55591 is the vulnerability that enabled the collection and release of FortiGate firewall configuration data on January 15, 2025, the vulnerability is nevertheless being exploited in the wild and should be treated with urgency.
Mitigation guidance
According to Fortinet’s advisory, the following products and versions are vulnerable to CVE-2024-55591:
- Fortinet FortiOS 7.0.0 through 7.0.16 (fixed in 7.0.17 or above)
- Fortinet FortiProxy 7.2.0 through 7.2.12 (fixed in 7.2.13 or above)
- Fortinet FortiProxy 7.0.0 through 7.0.19 (fixed in 7.0.20 or above)
Per Fortinet, other versions of FortiOS (6.4, 7.2, 7.4, 7.6) and FortiProxy (2.0, 7.4, 7.6) are not affected. Customers should update to a fixed version immediately, without waiting for a regular patch cycle to occur, and review Fortinet’s IOCs to aid investigations into suspicious activity. Indicators include examples of administrative or local users added by adversaries.
Customers should also ensure that firewall management interfaces are not exposed to the public internet and limit IP addresses that can reach administrative interfaces. If your organization was impacted by the January 15, 2025 FortiGate firewall data leak, you should change administrative and local user passwords immediately. FortiOS also supports multi-factor authentication (MFA) for local user accounts, which Rapid7 strongly recommends implementing.
Rapid7 customers
InsightVM and Nexpose customers can assess their exposure to CVE-2024-55591 with vulnerability checks available in the January 15, 2025 content release. Customers already have coverage for all other FortiOS vulnerabilities mentioned in this blog from past content releases.
Video Surveillance Storage in the Cloud
Post Syndicated from Jeremy Milk original https://www.backblaze.com/blog/video-surveillance-storage-in-the-cloud/
If you manage a video surveillance platform, storage is either the unsung hero of your infrastructure or your biggest headache. Maybe what started as a neat and functional setup for your video surveillance storage has turned into a complex system that demands far more maintenance than you expected.
As your storage volume grows and costs climb, the initial solutions begin to show their cracks, demanding more resources and attention. And, higher resolution cameras lead to even more storage demand, not to mention the increase in the number of cameras your customers want to install.
Today, I’m outlining some of the obstacles I’ve seen companies encounter in video surveillance storage as well as the benefits cloud storage offers to help you streamline operations, rein in costs, and regain control over your architecture, without sacrificing performance or flexibility.
Video surveillance storage challenges
Storage infrastructure is the backbone of your service—but it can also be one of the most demanding aspects to manage whether your data is stored in on-premises NVR/DVR systems, in the cloud, or in a hybrid model. Some of the key challenges include explosive data growth in the industry, balancing cost and performance, regulatory and compliance hurdles, latency and accessibility, and data security and redundancy. I’ll dig into each, and talk about some of the pitfalls you might face.
- Explosive data growth: The sheer volume of video data generated by modern surveillance systems is staggering. With cameras capturing high-definition footage 24/7, even modest setups can produce terabytes of data per day. Scaling storage to keep up with this growth without compromising performance or breaking the bank is no small feat.
- Balancing cost and performance: As storage needs grow, so do bandwidth requirements, data egress, and ongoing maintenance costs. Striking the right balance between affordability and the high availability your customers expect is a constant juggling act.
- Regulatory and compliance hurdles: Platforms must manage varying retention policies, ensure data privacy, and provide secure access controls to adhere to all relevant standards and requirements, such as GDPR and local video retention regulations—all while keeping everything running smoothly.
- Latency and accessibility: Your customers demand quick access to their video footage, whether it’s for live viewing or playback. High latency or sluggish retrieval times can lead to frustration and impact trust in your platform. Designing storage that ensures fast, reliable access to data across geographies is critical, but challenging.
- Data security and redundancy: Video footage isn’t just data—it’s sensitive, often mission-critical information that cybercriminals are increasingly targeting. Protecting it from ransomware, accidental loss, or corruption requires robust encryption, multiple backups, and careful management of access rights. Achieving this level of security without overcomplicating your architecture is a balancing act.
- Integrating AI: AI-powered analytics can enhance video surveillance capabilities (e.g., object detection, behavior analysis), but integrating AI is not without its challenges, and it’s something you need to consider carefully.
Advantages of the cloud for video surveillance platforms
Picking the right cloud storage platform can help you meet these challenges. Cloud storage offers a host of advantages that can transform how video surveillance platforms manage and scale their operations. Here’s why it’s worth considering:
1. Scalability and flexibility
Need to add storage for hundreds—or thousands—of new cameras per month? On-site storage solutions, such as physical servers, hard drives, or NAS systems have fixed capacities. Cloud storage scales with your platform, whether you’re serving small businesses or sprawling enterprise deployments. And, it adapts whether your customers are integrating additional cameras or extending their retention periods.
2. Cost optimization
Traditional on-prem solutions demand upfront investments in hardware and then ongoing maintenance. Cloud storage eliminates the need for those upfront hardware purchases. And the right cloud storage provider with pricing models built for your use case can help you get an edge in a competitive market.
The unique challenge of PUT requests
The video surveillance use case involves uploading a metric ton of data. In cloud terms, when you upload data, you typically use a PUT request. Many cloud providers charge for these API calls for hot and cold storage tiers. For example, it might be tempting to use a cold storage class to save on the base cost to store your video surveillance data, but a cold storage class like Amazon’s Glacier Instant Retrieval (GIR) charges $0.00002 per PUT request. When you’re making thousands or tens of thousands of PUT requests per day, even when the charges are tiny, costs can quickly escalate into the six figure range.
3. Accessibility
Whether your users are in the same city or halfway around the world, cloud storage makes video footage instantly accessible. Low-latency retrieval options and distributed cloud infrastructure mean faster access to the right data, regardless of location.
4. Reduced risk of data loss
Using the cloud for your data storage infrastructure mitigates the risks associated with physical vulnerabilities in the devices used by your customers. By automatically storing video footage in the cloud, even if the devices suffer damage, malfunction, or failure, the footage remains accessible thanks to the backup in the cloud. Replicate data across multiple geographically dispersed data centers, further reducing the risk of data loss due to hardware failures or natural disasters.
5. Enhanced security
Modern cloud storage solutions come with enterprise-grade security baked in, from end-to-end encryption to role-based access controls to scalable application keys. With built-in redundancy and regular backups, the cloud offers peace of mind that on-prem systems can’t always match—no more worrying about a single failed drive wiping out critical footage.
6. Minimized maintenance and IT overhead
Maintaining on-premises NVR/DVR systems requires substantial hardware and IT resources. In contrast, cloud systems are easier to manage. Updates, patches, and maintenance are handled by the cloud service provider. Your IT teams can focus on strategic tasks rather than routine server upkeep. This shift reduces your operational costs and streamlines management.
7. Ease of integration with AI and analytics
Storing your footage in the cloud makes it easier to integrate advanced features like AI-powered analytics, motion detection, and real-time alerts. You have a centralized repository of data that’s easy to analyze at scale. And, as opposed to on-prem systems, cloud platforms offer instant access from anywhere, making it more viable to train AI models on your own data.
Backblaze for video surveillance storage
Unlike some cloud providers and classes, Backblaze makes it affordable to secure, grow, and use your surveillance data. Backblaze’s straightforward pricing with zero PUT fees means you don’t have to worry about fees adding up, allowing you to store, manage, and access your data anywhere, anytime. And with 3x free egress for all plus unlimited free egress via many compute and CDN partners, you can more easily integrate with AI tools, sending your footage where the right GPUs are available without breaking the bank.

The future of video surveillance is in the cloud
Beyond the obvious scalability and operational gains of cloud storage, its biggest advantage in the coming years will be its AI readiness. AI innovations are poised to revolutionize security and video surveillance systems. By leveraging the cloud for AI and analytics, video surveillance platforms can move beyond mere storage to deliver actionable insights and real-time intelligence. This not only enhances the value you provide to customers but also differentiates your platform in an increasingly competitive market.
Cloud storage isn’t a one-size-fits-all solution, but for video surveillance platforms looking to streamline operations and future-proof their offerings, it’s hard to ignore the shift towards the cloud.
The post Video Surveillance Storage in the Cloud appeared first on Backblaze Blog | Cloud Storage & Cloud Backup
Security updates for Thursday
Post Syndicated from jake original https://lwn.net/Articles/1005292/
Security updates have been issued by AlmaLinux (fence-agents, raptor2, and rsync), Debian (chromium), Fedora (rsync and seamonkey), Mageia (openjpeg2), Red Hat (tuned), Slackware (git), SUSE (dcmtk, dnsmasq, govulncheck-vulndb, libQtWebKit4, libraptor-devel, opera, python311-Pillow, python311-translate-toolkit, rsync, and SDL2_sound-devel), and Ubuntu (linux-raspi-5.4, neomutt, and python2.7).
Ще бъдем силна опозиция
Post Syndicated from Bozho original https://blog.bozho.net/blog/4443
Можех да фокусирам изказването си днес при избора на кабинет върху думи на представители на управляващото мнозинство в миналото кой с кого няма никога да се коалира. Но това щеше да бъде дребно политическо заяждане, от което гражданите са се уморили. Вместо това в изказването си казах следното:
За страната е важно да има редовно правителство, което да решава проблеми и да напредва по стратегически решения
за страната. Но моето дълбоко опасение е, че това правителство няма да е такова. По много причини.
Например, колебливите позиции на част от партиите по отношение на еврозоната, която е стратегически приоритет за страната.
Или начинът, по който се стигна до реализиране на това правителство. След прекратяване на преговорите с Демократична България, нямаше никаква светлина върху процеса – нито кой преговаря, нито за какво преговаря, като единствената информация изтичаше през медиите на Пеевски. Накрая видяхме просто един списък с министри. И то преди да обществото са научи приоритетите на управлението.
Но най-проблемното е отказът да се ограничи влиянието на Пеевски. От коалиционното споразумение, до което уж бяхме стигнали на пети януари, са премахнати всички конкретни мерки за ограничаване на нелегитимните влияния в съдебната и изпълнителната власт. Това е ясна заявка, че това мнозинство няма за цел да реши този системен проблем, който чрез задкулисие генерира нестабилност.
Смятам, че това беше основната тема на несъгласие с нас, и не беше коректно спрямо г-н Желязков да го използват за оправдание.
И по тези и по много други причини, има сериозни рискове, това правителство да се провали, а това ще е провал и за страната.
Такъв провал включва и опасността в променяща се международна среда тази нехомогенна коалиция да вземе грешни решения за дългосрочното позициониране на страната.
Вярвам, че мнозинството си дава сметка за тези рискове и проблеми и знае, че ще му е трудно. Дано неизбежните компромиси бъдат с партийното и личното его, а не с обществения интерес. Когато са с обществения интерес, ние ще реагираме остро.
Ще бъдем силна опозиция. Не деструктивна, не креслива, а такава, която показва, че може по-добре.
Няма да злорадстваме за всеки неуспех, да профанизираме трудните компромоси и да атакуваме малките неволни грешки. Но управляващите добре знаят, че различаваме неволните грешки от съзнателното потъпкване на обществения интерес.
Ще се противопоставяме остро на всички опити за дозавладяване на държавата и за укрепване на нелегитимните влияния.
Но и ще подкрепяме всички правилни политики, свързани с борбата с корупцията, модернизацията на страната, еврозоната, намаляването на административната тежест, оптимизацията на публичните разходи. Ще предлагаме решения, които са в духа на постигнатите широки, принципни съгласия.
И вместо патетично заключение искам да благодаря на българските граждани за доверието, което са инвестирали в политическите партии в толкова сложна ситуация. Да подходим с отговорност към това доверие, особено тези, които ще упражняват изпълнителната власт.
Материалът Ще бъдем силна опозиция е публикуван за пръв път на БЛОГодаря.
The 1993 Consumer Electronics Show via Computer Chronicles
Post Syndicated from LGR original https://www.youtube.com/watch?v=YVViepyE0ug
Change is the Only Constant: 2024 in Review
Post Syndicated from Michael Kammer original https://blog.zabbix.com/change-is-the-only-constant-2024-in-review/29528/
Time waits for no one, and as impossible as it may seem, one of the most consequential years in the history of Zabbix is already in the books. You can be forgiven for feeling at times like we were trying to cram a decade of events into a single year, which is why we’ve prepared this handy look back at the highlights of 2024 – just in case there’s anything you were too busy to notice as it happened!
Re-imagining the product
One of the year’s unquestioned highlights was the long-awaited release of Zabbix Cloud on October 1. As our first new product release since the creation of Zabbix, Zabbix Cloud is designed to provide the Zabbix features our community members know and love, but with easier deployment and management as well as automatic upgrades and easier scalability.
To celebrate the release itself, we held a release party at our Riga HQ with members of our global community who were in town for Zabbix Summit 2024, which kicked off a few days later. The release definitely got our community talking – the level of interest in this new “portable” version of Zabbix exceeded even our highest expectations.
Our team also released Zabbix 7.0 LTS on June 4, packed full of improvements and upgrades that our users have been asking for, including upgraded performance and scalability, new ways to visualize data, faster network discovery speed, and more. We followed that in December with the release of Zabbix 7.2, which added improved monitoring features and workflows as well as a host of new templates.
It can’t be stressed enough – all these new products, innovations, and updates were the result of feedback and suggestions from our global community. We listen, we learn, and we take your ideas to heart!

Security first
In 2024, Zabbix transitioned to the ISO/IEC 27001:2022 certification, with an extended scope to cover Zabbix Cloud. This milestone also includes compliance with ISO/IEC 27017:2015, further enhancing cloud-specific security controls.
Meanwhile, the HackerOne bug bounty program continues to be a success. 2024 brought us 33 valid submissions, and we paid $35,000 in bounties. Out of those, we have already fixed and published 24 vulnerabilities for source code.
The Zabbix CVE (Common Vulnerabilities and Exposures) program and processes are also continuing to mature. Recently, an audit was performed against our organization’s CVE submission for 40 submissions in the NIST NVD (National Vulnerability Database). Not only did we pass the audit and gain contributor status, but Zabbix is currently the only CVE Numbering Authorities (CNA) in Latvia.
Making our presence felt
Our community members piled up the frequent flier miles as we traveled the globe to keep in touch with our ever-expanding community and win over new converts. The events we took part in this year included the following:
• 31 meetings (with first-time visits to many destinations in North America)
• 1 forum in Mexico City
• 18 meetups (both online and in a variety of global locations)
• 4 conferences (Benelux, China, Japan, and Latin America)
• Far too many exhibitions, trade fairs, and expos to list conveniently
• One extremely successful Zabbix Summit in Riga
“The long hours and even longer flights really paid off, as this year was our most successful yet in terms of new business. The events we held in North America were especially helpful in terms of breaking new ground. We understood that we have an amazing Zabbix community in the United States and a much bigger market to work with.” – Ronalds Sulcs, Zabbix Head of Sales

A year of continuous growth
2024 saw us add new team members in every location we operate in, while also recruiting remote workers from nearly every corner of the globe. All told, the team grew by 30 people, which means we are now almost 200 strong! Meanwhile, the Partners team was also operating at full throttle, adding 12 new highly-skilled Certified Partners and 16 Resellers in locations from Australia to Morocco. All partners and resellers were chosen for their unique blend of experience and expertise, and we’re confident that they’ll provide best-in-class knowledge where it’s needed most.
The fact that we’ve managed to build on our status as an employer of choice across three continents while adding an ever-increasing number of quality partners in every corner of the globe speaks to the hard work and competence of our colleagues as well as the quality of the products and services we provide. Congratulations to everyone who did their part to make sure we continue to add talent and expertise!
Giving back
2024 was an exceptionally successful year in terms of bringing our products and services to the world, but we’re proud of the fact that we also managed to export our values of openness, transparency, and a desire to give back to the communities we live and work in. This took multiple forms throughout the year:
• The LatAm team worked with the DEDICA Foundation – Foundation for Digital Development and Open Knowledge to create the Zabbix Innova Challenge. The challenge is designed to encourage creativity and stimulate technological development in local communities through a Hackathon and other activities, with the goal of introducing Zabbix to a new generation of tech talent.
• In December, we made a generous donation to Pārtikas banka “Paēdušai Latvijai” (Food Bank “For a Full Latvia”) in support of their mission of getting nutritious food to communities in need. We also gave to support Bērnu slimnīcas fonds, Latvijas Bērnu fonds, Autisma atbalsta punkts, and Ziedot.lv – all with the goal of supporting children’s health, while our employees in the Riga office prepared gifts for senior citizens at the Rīga Social Care Center Mežciems as part of the “Eņģeļa pasts (Angel’s Mail)” charity project, Santa’s Workshop.
• The end of the year also saw us contribute €50,000 to Dod pieci!, the Latvian charity marathon organized by Latvijas Radio, Latvijas Televīzija, LSM.lv, and Ziedot.lv. The marathon helps make life-saving cancer treatment more affordable.
It’s been our experience that making a difference and donating to good causes reinforces a shared commitment to the company as well as to each other. We’d like to thank and congratulate everyone who took part in our outreach efforts over the past year!

Getting noticed
The news about what we got up to in 2024 seemed to be everywhere, as tech journals, newspapers, and global organizations showered us with positive publicity. At Interop Tokyo 2024, the Zabbix Japan team picked up the prestigious “Best of Show” Grand Prize in the Management and Monitoring category for the Zabbix 7.0 LTS release. The award is granted by a jury made up of some of the world’s most knowledgeable IT and monitoring experts, so recognition was truly an honor.
In Latin America, Milenio published a profile of our CEO and Founder Alexei Vladishev that brought the Zabbix story to thousands of new readers, while Mexico’s Encuentro Vidal marked the occasion of Zabbix Conference Mexico in November with a look at how Zabbix is helping countries in the region on their journey to digital transformation.
Globo published a well-written and informative piece that explored how the Brazilian city of Extrema has been investing in new technologies (with Zabbix prominent among them) in order to better serve the population of the city and make its administration more efficient and transparent.
Carrying our momentum into 2025
As 2025 gets underway, remember to stay on top of Zabbix news by following us on social media, reading our blog, and checking our forum.
“2024 was an eventful year that was full of excitement, growth, and change. It was the year we made Zabbix Cloud a reality, and a true milestone in the growth of our company and our community. I’m sure that everyone in the Zabbix family is excited to see what our 20th Anniversary year of 2025 will bring!” – Alexei Vladishev, Zabbix Founder and CEO
The post Change is the Only Constant: 2024 in Review appeared first on Zabbix Blog.